
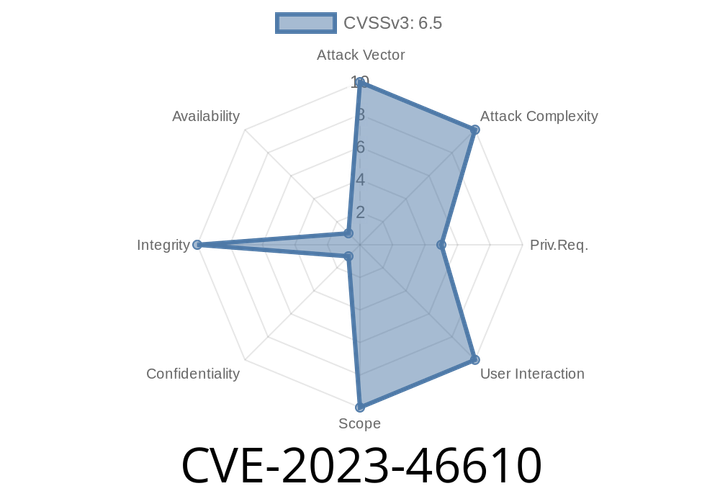
CVE-2023-46610 - How Missing Authorization in Quill Forms Puts Your WordPress at Risk
In late 2023, a security flaw identified as CVE-2023-46610 was uncovered in the popular WordPress plugin Quill Forms. This bug lets attackers exploit
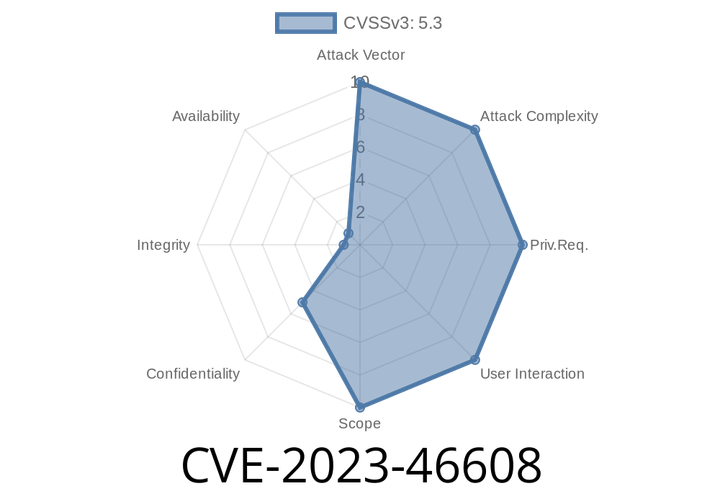
CVE-2023-46608 - How Missing Authorization in WPDO DoLogin Security (<=3.7.1) Exposes Your WordPress Site
If you are using the popular DoLogin Security plugin for WordPress, listen up. A critical vulnerability tracked as CVE-2023-46608 was recently disclosed, and
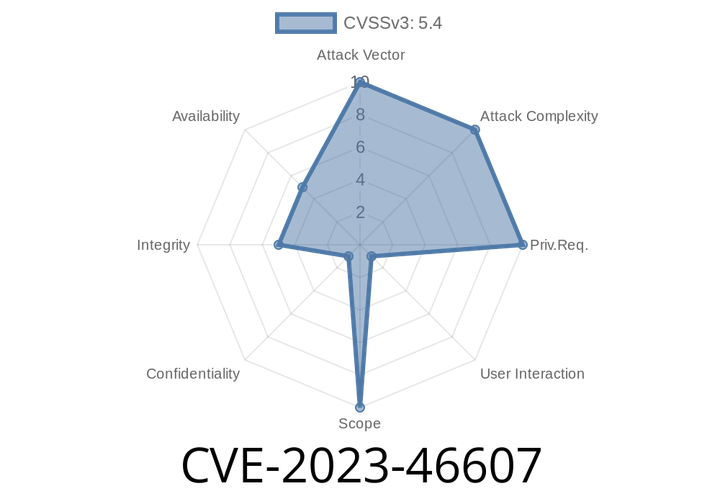
CVE-2023-46607 - How Hackers Can Exploit Missing Authorization in WP iCal Availability (≤ 1..3) – Deep Dive & Exploit Example
In November 2023, an important security flaw (CVE-2023-46607) was discovered in the WordPress plugin WP iCal Availability, a tool designed to display rental
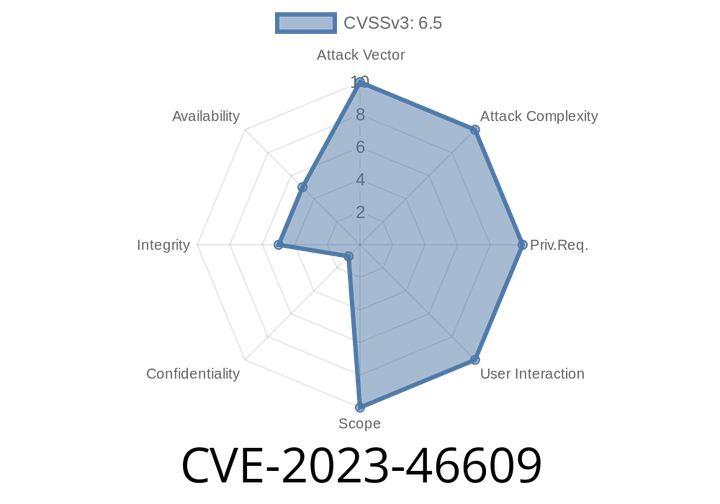
CVE-2023-46609 - Exploiting Authorization Flaws in FeedFocal Plugin (v1.2.2 and Below)
Vulnerabilities arising from missing or improperly configured access controls are some of the most dangerous yet commonly overlooked issues in web applications. In late 2023,
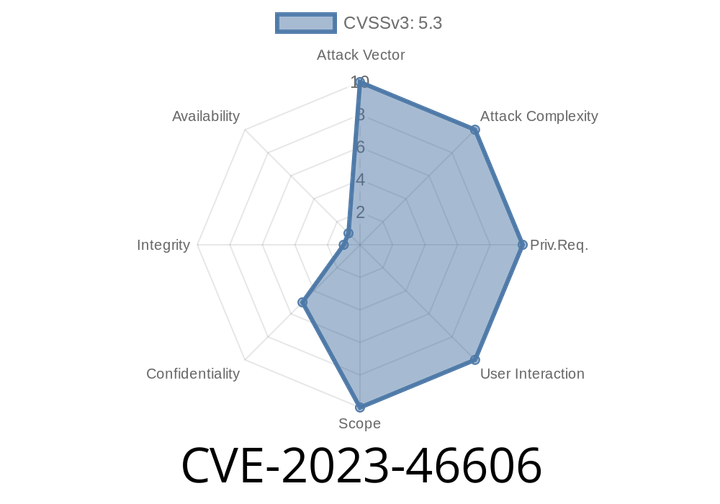
CVE-2023-46606 - Exploiting AtomChat’s Missing Authorization Leading to Data Exposure (Exploit Details & Fix)
---
What is CVE-2023-46606?
CVE-2023-46606 is a critical vulnerability found in AtomChat (versions through 1.1.4). AtomChat is a popular chat
Episode
00:00:00
00:00:00