
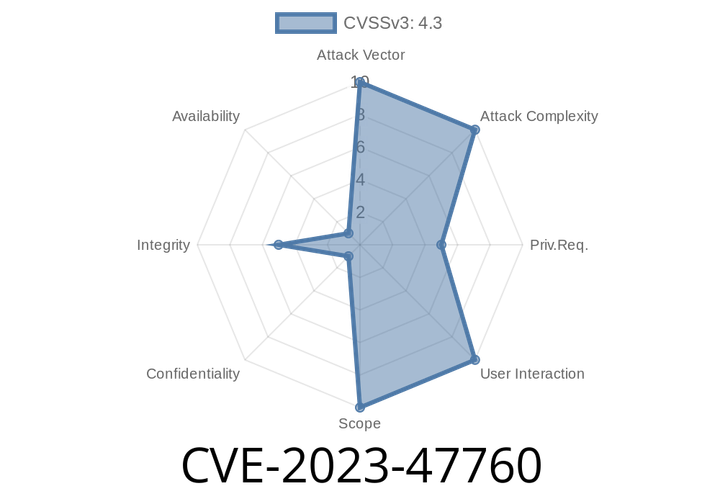
CVE-2023-47760 - Exploiting Missing Authorization in Essential Blocks for Gutenberg (WordPress Plugin)
A critical vulnerability—CVE-2023-47760—was discovered in the popular WordPress plugin Essential Blocks for Gutenberg. This plugin is used by thousands to add
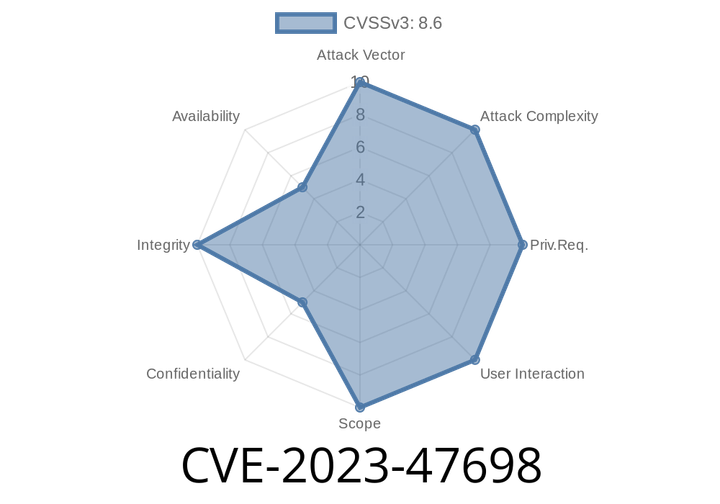
CVE-2023-47698 - How Incorrect Access Controls in Artisan Workshop Japanized For WooCommerce Led to a Serious Authorization Vulnerability
Summary:
A critical security vulnerability, identified as CVE-2023-47698, was found in certain versions of the “Japanized For WooCommerce” plugin for WordPress. This flaw

CVE-2023-47761 - Exploiting the Missing Authorization Flaw in WPDeveloper Simple 301 Redirects by BetterLinks
WordPress is everywhere, and plugins are what make it fun and versatile. Security, though, can sometimes get lost in the quest for features. Today, let’
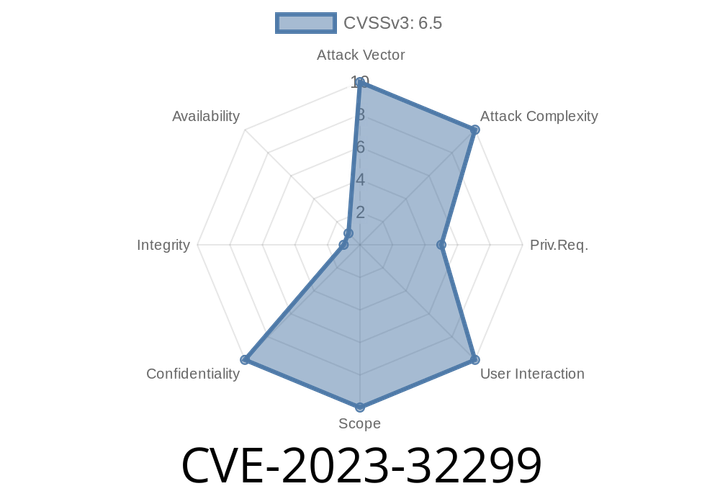
CVE-2023-32299 - How a Missing Authorization Bug in Ni WooCommerce Sales Report Exposed Your Store Data
---
Introduction
In 2023, security researchers discovered a critical vulnerability identified as CVE-2023-32299 in the WordPress plugin Ni WooCommerce Sales Report. This plugin, widely
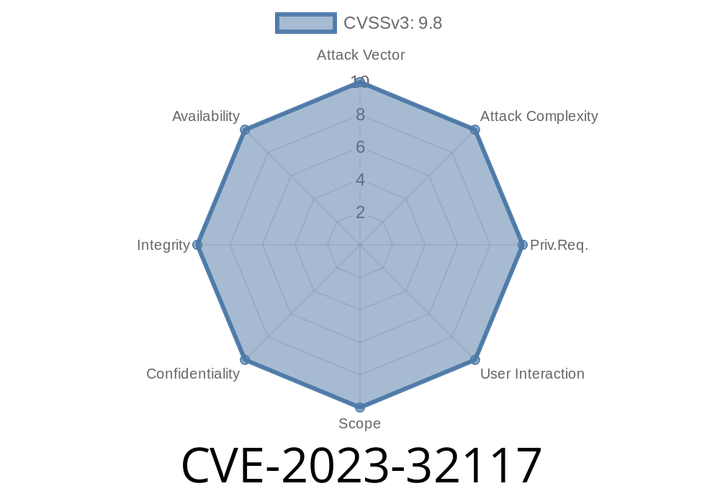
CVE-2023-32117 - Exploiting the Missing Authorization in SoftLab Integrate Google Drive (n/a - 1.1.99)
The digital world runs on cloud connectors, but sometimes, integration plugins forget to ask, “Are you allowed in?” That’s exactly what happened with CVE-
Episode
00:00:00
00:00:00