

CVE-2024-54137 - How a Critical Indexing Bug in liboqs’ HQC KEM Could Break Shared Secrets
tl;dr
A serious bug in the C-language liboqs post-quantum crypto library (used for quantum-resistant crypto) caused secret key parts to be

CVE-2024-12254 - Memory Exhaustion in Python 3.12+ Asyncio `writelines()` Puts Servers at Risk
Python 3.12 introduced multiple improvements to its popular asyncio module, promising faster asynchronous code and smarter memory usage. However, the change introduced an overlooked

CVE-2024-54143 - How Insecure Hashing in OpenWrt/asu Lets Attackers Poison Your Firmware Updates
OpenWrt is a popular open-source operating system for embedded devices, especially routers. To make custom firmware images, many rely on OpenWrt’s ASU image

CVE-2024-54214 - How Unrestricted File Upload in Roninwp Revy Lets Attackers Deploy Web Shells
In June 2024, security researchers publicly disclosed a critical vulnerability in the Roninwp Revy WordPress plugin. Labeled CVE-2024-54214, this flaw allows any unauthenticated
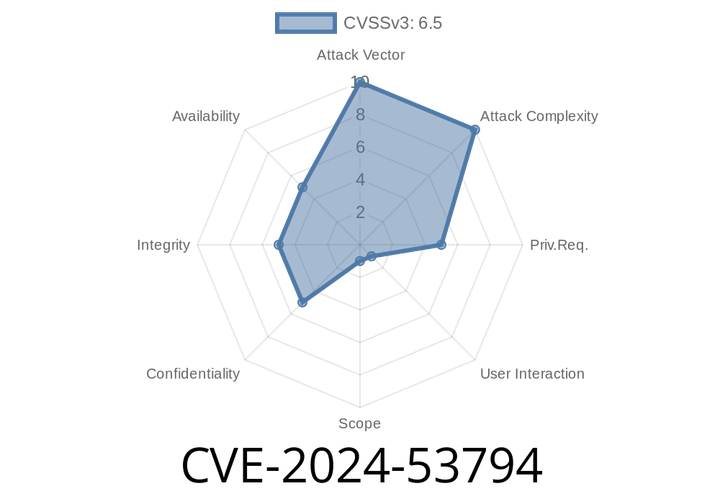
CVE-2024-53794 - Deep Dive Into Stored XSS in Arkhe Blocks by LOOS,Inc. (Up to 2.27.)
Cross-Site Scripting (XSS) still plagues modern web apps, and the vulnerability CVE-2024-53794 shows just how easy it is for stored XSS attacks
Episode
00:00:00
00:00:00