
CVE-2024-10977 - How Attacker-Controlled Error Messages in PostgreSQL Client Libraries Can Risk Your Data
PostgreSQL is one of the world’s most popular and trusted database systems, supporting mission-critical apps for millions. But even PostgreSQL isn’t immune
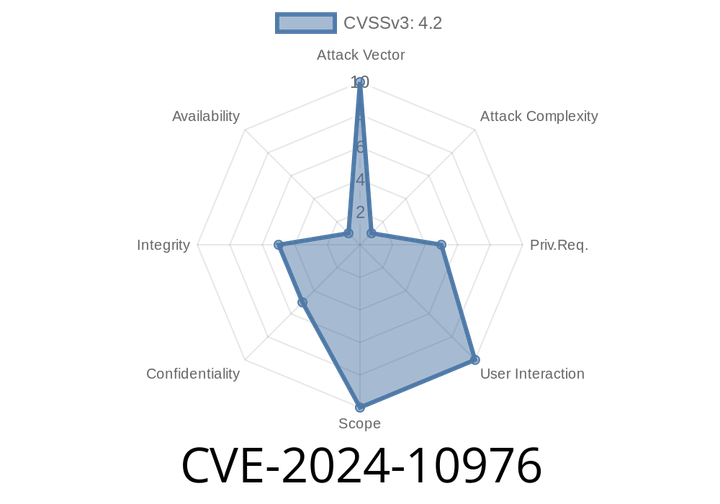
CVE-2024-10976 - Risks of Incomplete Row Security Tracking in PostgreSQL Through Query Plan Reuse
Summary:
CVE-2024-10976 is a newly-identified vulnerability in PostgreSQL that can let a user bypass row-level security (RLS) and access or modify

CVE-2023-4458 - Sensitive Data Disclosure in Linux KSMBD Module Due to Flawed Attribute Parsing
Linux is one of the most widely used operating systems across the globe, known for its stability and robust security practices. However, even mature software
CVE-2022-31670 - Breaking Harbor’s Boundaries with Tag Retention Policy Escalation
When we protect our container images, tools like Harbor are critical in keeping our images organized, up-to-date, and safe from accidental deletion. Harbor
CVE-2024-3447 - Heap-Based Buffer Overflow in QEMU SDHCI Device Emulation Explained
In June 2024, a critical vulnerability was found in the QEMU emulator, specifically in the SDHCI device emulation code. Identified as CVE-2024-3447, this
Episode
00:00:00
00:00:00