
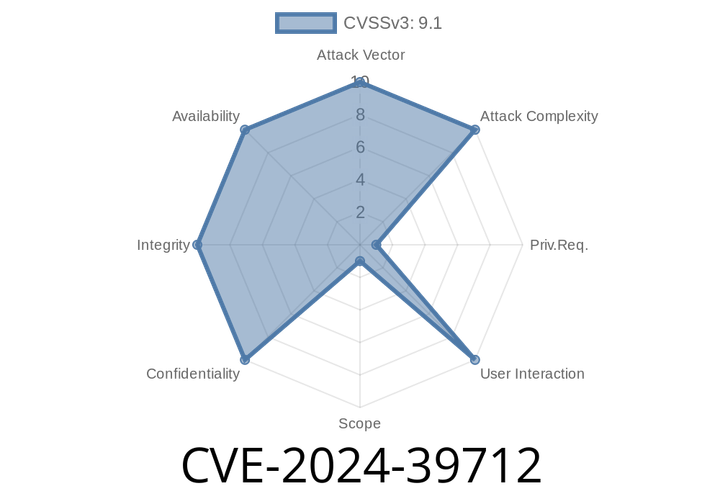
CVE-2024-39712 - Argument Injection & Remote Code Execution in Ivanti Connect Secure – An Exclusive Deep Dive
The cybersecurity world is buzzing about a recent high-severity vulnerability: CVE-2024-39712. Found in the widely used Ivanti Connect Secure (formerly known as
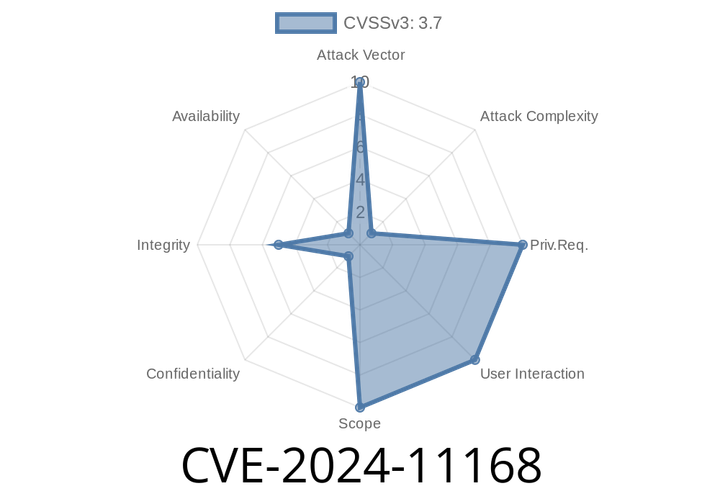
CVE-2024-11168 - The Hidden Danger in Python’s URL Parsing (`urllib.parse.urlsplit()` and `urlparse()` SSRF Vulnerability Explained)
In early 2024, a subtle but potentially dangerous vulnerability was discovered in Python’s standard library, specifically within the widely used urllib.parse.urlsplit() and
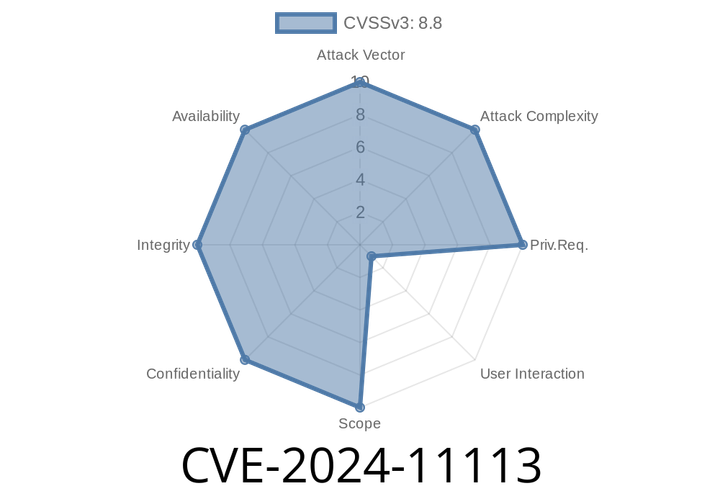
CVE-2024-11113 - Unpacking the Use-After-Free Bug in Chrome’s Accessibility—What You Need to Know
On March 13, 2024, Google assigned CVE-2024-11113 to a medium-severity bug in their Chrome browser. The bug, a classic use-after-free

CVE-2024-11115 - Navigation Policy Flaw in Chrome iOS—Exploit, Details, and Mitigation
---
Google Chrome is the world’s most popular browser, and it’s no stranger to being targeted by security researchers and bad actors alike. This

CVE-2024-11111 - Google Chrome Autofill UI Spoofing Vulnerability Explained
On June 6, 2024, a new vulnerability was disclosed in Google Chrome called CVE-2024-11111. This issue affects Chrome browsers before version 131..6778.
Episode
00:00:00
00:00:00