
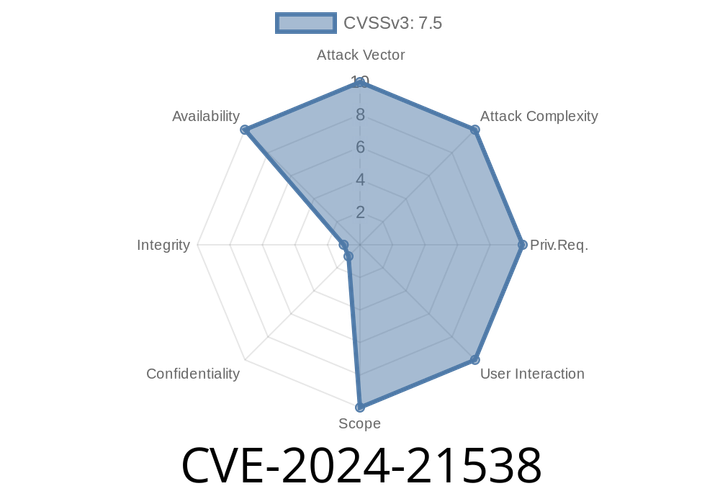
CVE-2024-21538 - How a ReDoS Vulnerability in cross-spawn Can Crash Your Node.js Apps
TL;DR:
If your project uses cross-spawn before version 7..5, you are vulnerable to a Regular Expression Denial of Service (ReDoS) attack. This
CVE-2024-40715 - How MITM Attackers Can Bypass Authentication in Veeam Backup & Replication Enterprise Manager
In June 2024, a new security vulnerability was identified in Veeam Backup & Replication Enterprise Manager (B&R EM), tracked as CVE-2024-40715.

CVE-2024-10963 - PAM Access Vulnerability Explained — How Hostname Misinterpretation Can Lead to Unauthorized Access
On February 15, 2024, a critical security flaw was identified in pam_access, a widely-used Linux Pluggable Authentication Module (PAM) that controls access to
CVE-2024-43440 - How a Moodle Restore Flaw Can Expose Your Server
In May 2024, a serious vulnerability was discovered in Moodle, the world's most popular open-source learning management system. Tracked as CVE-2024-
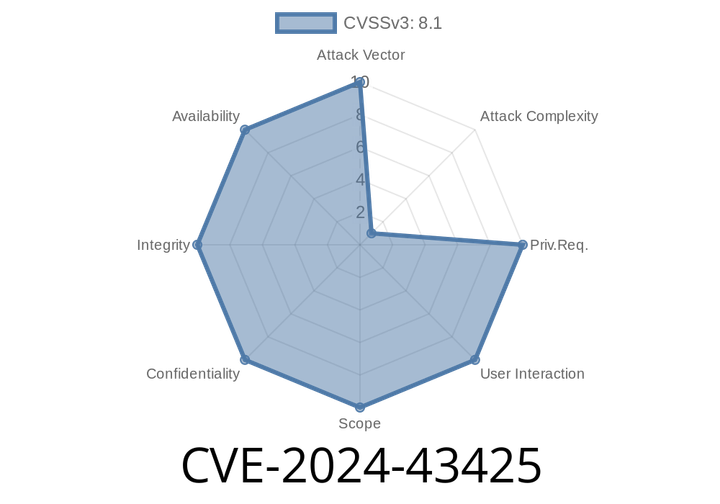
CVE-2024-43425 - Remote Code Execution Risk in Moodle's Calculated Question Types
Published: June 2024
Author: SecureInsight AI
Severity: High
Affected Product: Moodle (All versions before the fix)
TL;DR
A security vulnerability tagged as CVE-2024-
Episode
00:00:00
00:00:00