
CVE-2023-1973 - How a Flaw in Undertow’s Form Authentication Can Crash Your Server (with Practical Exploit Example)
Undertow is a popular web server option often used at the core of Java applications, including projects built with WildFly and JBoss. In early 2023,
CVE-2024-38286 - How Apache Tomcat’s Resource Mismanagement Can Topple Your Server
A critical new security vulnerability—CVE-2024-38286—has been discovered in Apache Tomcat, one of the world’s most popular Java web servers. This
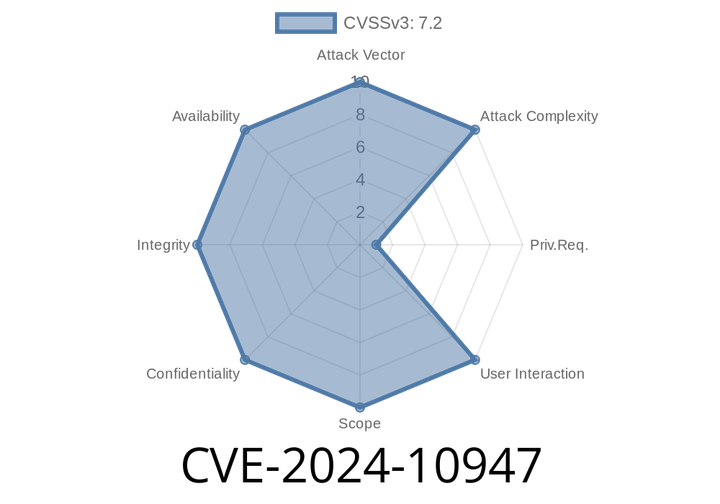
CVE-2024-10947 - Critical SQL Injection in Guangzhou Tuchuang Interlib Library Cluster Automation Management System (≤2..1)
A critical vulnerability, known as CVE-2024-10947, was discovered in the Guangzhou Tuchuang Computer Software Development Interlib Library Cluster Automation Management System up to
CVE-2024-51988 - How a Queue Deletion Permission Bug in RabbitMQ Left Your Messages Vulnerable
June, 2024 saw the disclosure of a serious security issue in the popular RabbitMQ message broker system, tracked as CVE-2024-51988. This vulnerability enables
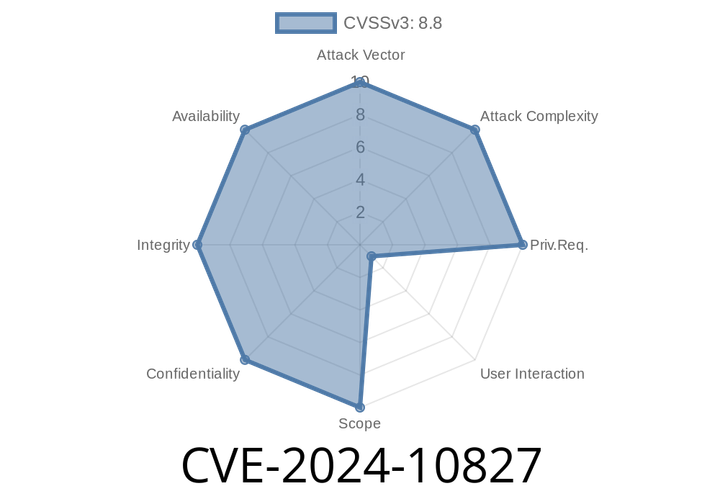
CVE-2024-10827 - Use-After-Free in Chrome Serial API Explained with Code & Exploitation
In early 2024, security researchers uncovered a serious vulnerability in Google Chrome’s implementation of the Serial API, tracked as CVE-2024-10827. If you’
Episode
00:00:00
00:00:00