

CVE-2024-44872 - Reflected XSS in moziloCMS v3. – Exploit Details & How to Stay Safe
moziloCMS is a lightweight content management system (CMS) that's easy to set up and use. However, a new security issue, CVE-2024-44872,
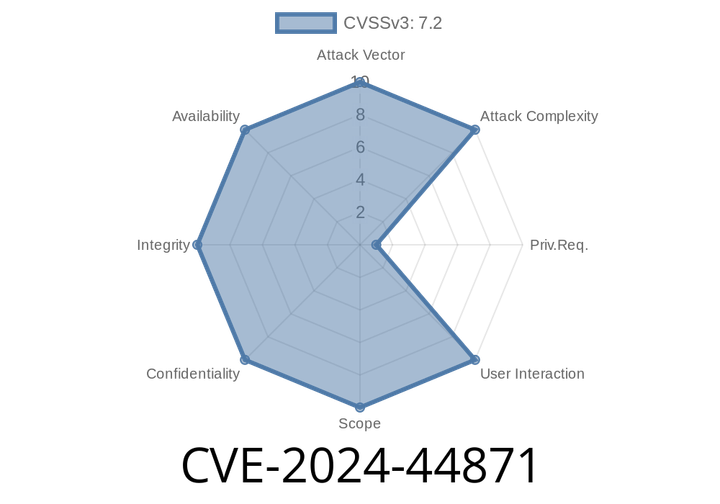
CVE-2024-44871 - Exploiting Arbitrary File Upload in moziloCMS v3.’s /admin/index.php
CVE-2024-44871 is a fresh and severe vulnerability found in the open-source moziloCMS v3.. It lets attackers upload any file to the server—
CVE-2024-43487 - Windows Mark of the Web (MotW) Security Bypass Explained — Full Details and Exploit Walkthrough
---
Introduction
In May 2024, Microsoft disclosed CVE-2024-43487, a security vulnerability affecting the Windows Mark of the Web (MotW) feature. Mark of the Web
CVE-2024-43492 - How Microsoft AutoUpdate (MAU) Left Macs Wide Open for Attackers
If you’re a Mac user running Microsoft Office products, a recent vulnerability called CVE-2024-43492 may put your system at risk. This post

CVE-2024-43491 - How a Servicing Stack Bug Reopened Old Security Holes on Windows 10 Version 1507
*Published: June 2024*
Microsoft recently reported a new vulnerability, CVE-2024-43491, that impacts some Windows 10 systems in a unique way. This flaw doesn’
Episode
00:00:00
00:00:00