

CVE-2024-2880 - GitLab CE/EE "admin_group_member" Custom Role Permission Vulnerability Exploit
A recently discovered vulnerability in GitLab, identified as CVE-2024-2880, allows a user with the "admin_group_member" custom role permission to
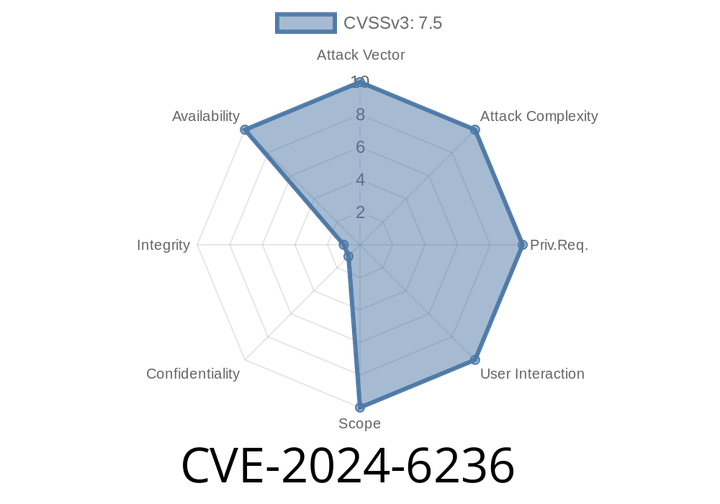
CVE-2024-6236 - Denial of Service in NetScaler Console, NetScaler Agent, and NetScaler SDX Explained
On June 2024, Citrix addressed a new security vulnerability in their network management and monitoring solutions. Labeled CVE-2024-6236, this vulnerability affects NetScaler Console

CVE-2024-6286 - Local Privilege Escalation in Citrix Workspace App for Windows Explained
Citrix Workspace users, take note: a new local privilege escalation vulnerability has been found in the Windows version of this popular application. Tracked as CVE-

CVE-2024-6151 - Local Privilege Escalation in Citrix Virtual Delivery Agent for Windows – How It Works and Exploit Details
On June 25, 2024, Citrix published a security advisory for a serious local privilege escalation vulnerability, identified as CVE-2024-6151, in its Virtual Delivery

CVE-2024-5910: Exploiting Missing Authentication in Palo Alto Networks Expedition for Admin Account Takeover
Palo Alto Networks Expedition is a powerful tool that streamlines the process of migrating, tuning, and enriching configurations for organizations utilizing the Palo Alto Networks
Episode
00:00:00
00:00:00