
CVE-2024-39330 - Django Storage Directory Traversal Explained (With Example & Exploit)
A new security issue — CVE-2024-39330 — was discovered in popular Python web framework Django (5. before 5..7 and 4.2 before 4.2.
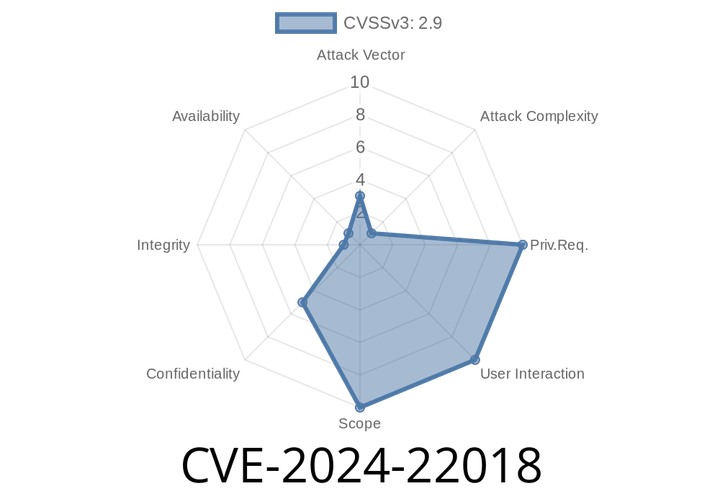
CVE-2024-22018 - Node.js Permission Model Bypass via fs.lstat — Explained, Exploited, and What To Do
A new vulnerability, CVE-2024-22018, has been discovered in Node.js that may allow attackers to learn sensitive information about files, even when explicit