

CVE-2024-36236 - Exploiting DOM-based XSS in Adobe Experience Manager ≤6.5.20
In May 2024, security researchers discovered a DOM-based Cross-Site Scripting (XSS) vulnerability in Adobe Experience Manager (AEM), specifically in versions 6.5.20

CVE-2024-4201 - GitLab XML Raw Viewer Cross-Site Scripting (XSS) Exploit Explained
CVE-2024-4201 is a newly discovered security vulnerability in GitLab, one of the most popular platforms for software development. The bug is a form

CVE-2024-5798 - How a JWT Audience Validation Bug in HashiCorp Vault Could Let Attackers In
Vault and Vault Enterprise are powerful tools for managing secrets and protecting sensitive data. Many organizations trust them for critical workloads. But in June 2024,
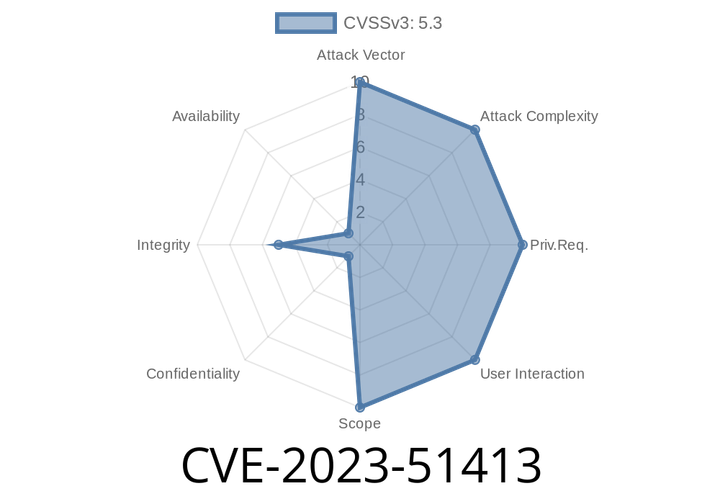
CVE-2023-51413 - Exploiting the Missing Authorization Vulnerability in Piotnet Forms (v1..29 and Earlier)
---
Overview
If you run a WordPress website and use the popular Piotnet Forms plugin, it’s time to pay attention. A critical missing authorization vulnerability
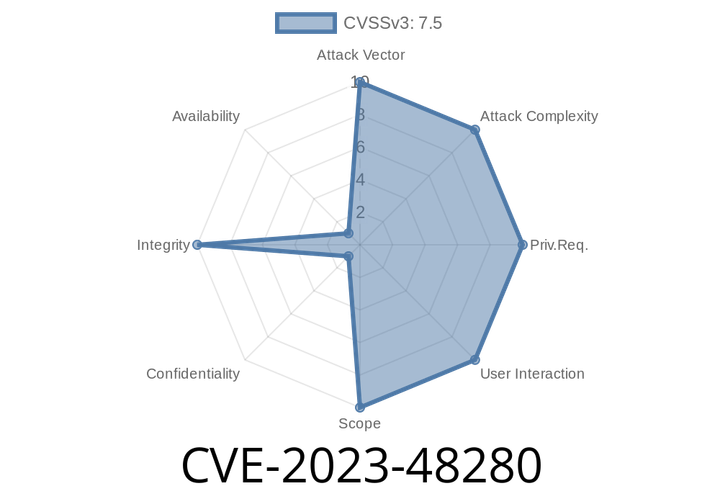
CVE-2023-48280 - Exploiting Missing Authorization in Consensu.IO (up to 1..1)
In late 2023, a Missing Authorization vulnerability was publicly disclosed affecting Consensu.IO, a popular consent management platform. Identified as CVE-2023-48280, the flaw
Episode
00:00:00
00:00:00