
CVE-2025-0107 - How a Dangerous OS Command Injection in Palo Alto Networks Expedition Puts Your Network at Risk
In June 2024, details surfaced about a critical vulnerability in Palo Alto Networks Expedition—a tool that many organizations use to migrate and manage next-
CVE-2025-0103 - Undressing Palo Alto Networks Expedition – Deep Dive Into Critical SQL Injection and File Exploit
Palo Alto Networks’ *Expedition* is a migration and optimization tool trusted by countless organizations worldwide. But in early 2025, a storm broke with CVE-2025-

CVE-2024-57823 - Integer Underflow in Raptor RDF Syntax Library’s Turtle Parser Leads to Potential Exploit
CVE-2024-57823 highlights a critical integer underflow vulnerability found in the widely utilized Raptor RDF Syntax Library, which is popular for parsing and serializing
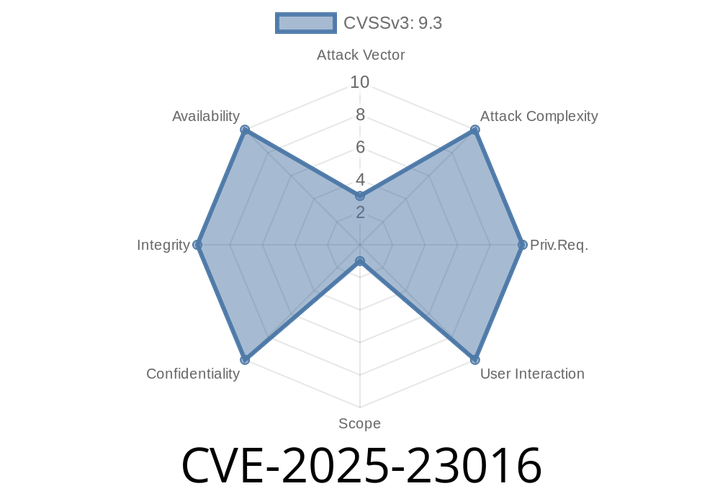
CVE-2025-23016 - FastCGI fcgi2 2.x–2.4.4 Remote Buffer Overflow Explained & Exploited
A newly identified security flaw, CVE-2025-23016, affects the popular FastCGI fcgi2 package (also known as fcgi) versions 2.x through 2.4.4.
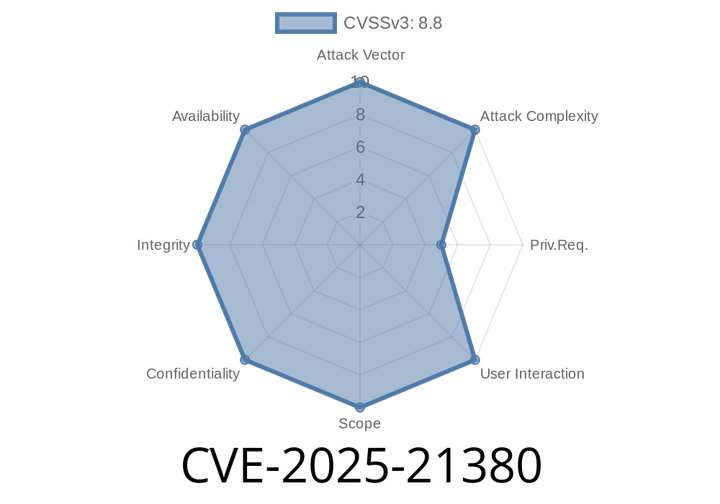
CVE-2025-21380 - Improper Access Control in Azure SaaS Resources Enables Information Disclosure — A Deep Dive
In early 2025, Microsoft patched a new security vulnerability identified as CVE-2025-21380. This weakness, affecting certain Azure SaaS resources, allows an attacker with
Episode
00:00:00
00:00:00