
CVE-2024-56780 - Race Condition in Linux Kernel Quota Subsystem—Exploit & Fix Explained
The Linux kernel is continuously evolving, and every line of code protecting your data matters. In CVE-2024-56780, a subtle but real vulnerability in

CVE-2023-35685 - Exploiting a Kernel Use-After-Free Bug in DevmemIntMapPages for Local Privilege Escalation
A new local privilege escalation vulnerability has been discovered in the Linux kernel. Tracked as CVE-2023-35685, this bug exists in the way the
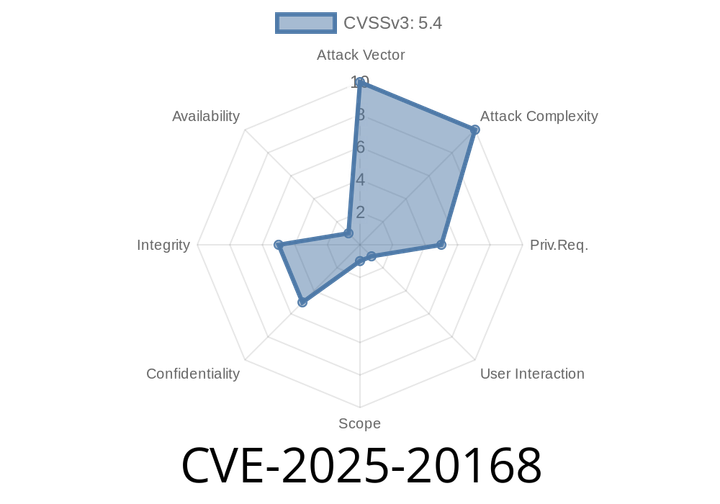
CVE-2025-20168 - XSS Vulnerability in Cisco CSPC Management Interface — Exclusive Deep Dive & Exploit Guide
CVE-2025-20168 is a recently disclosed security flaw in the web-based management interface of Cisco Common Services Platform Collector (CSPC). This weakness allows

CVE-2024-55459 - How a keras 3.7. Vulnerability Lets Attackers Write Files On Your Machine
In June 2024, a significant security vulnerability (CVE-2024-55459) was discovered in the popular machine learning library keras. This bug lets attackers write files—

CVE-2024-45033 - Insufficient Session Expiration in Apache Airflow Fab Provider (Pre-1.5.2) - Full Analysis & Exploit Demo
Published: June 2024
Affected Package: apache-airflow-providers-fab < 1.5.2
Severity: Medium
Reference: GHSA-x8wv-h3mm-65c4 (GitHub Advisory)
Executive Summary
A
Episode
00:00:00
00:00:00