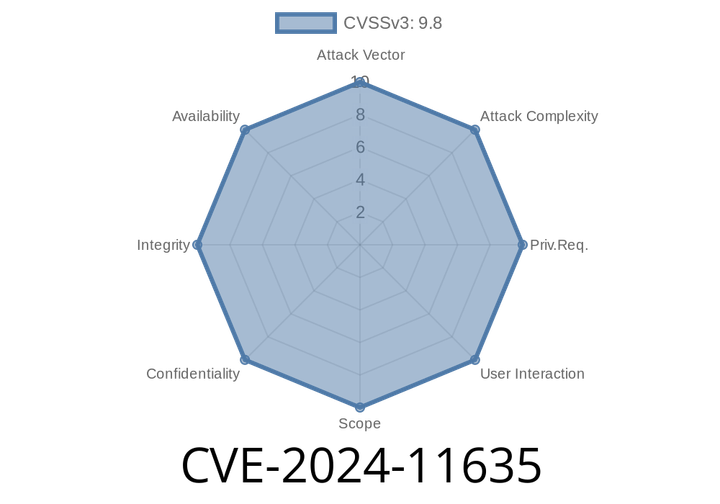
CVE-2024-11635 - Remote Code Execution in WordPress File Upload Plugin via wfu_ABSPATH Cookie
CVE-2024-11635 is a serious security vulnerability in the popular WordPress File Upload plugin, affecting all versions up to and including 4.24.12.

CVE-2024-50603 - Critical Command Injection in Aviatrix Controller – Exploit Guide and Technical Breakdown
A newly discovered vulnerability, CVE-2024-50603, impacts Aviatrix Controller versions before 7.1.4191 and 7.2.x before 7.2.4996. This high-

CVE-2024-54006 - Exploiting Multiple Command Injection Bugs in the 501 Wireless Client Bridge
*Published: June 2024*
Introduction
In mid-2024, security researchers discovered a set of dangerous command injection vulnerabilities in the web interface of a popular networking
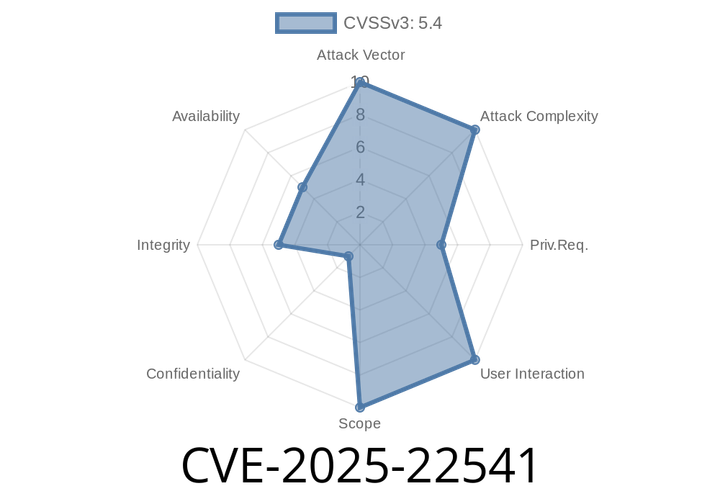
CVE-2025-22541 - How Missing Authorization in WP Delete Post Copies Plugin Lets Attackers Delete Your Posts
If you run a WordPress website, plugins make your site powerful—but they can also make your site vulnerable if not well-designed. Recently, a
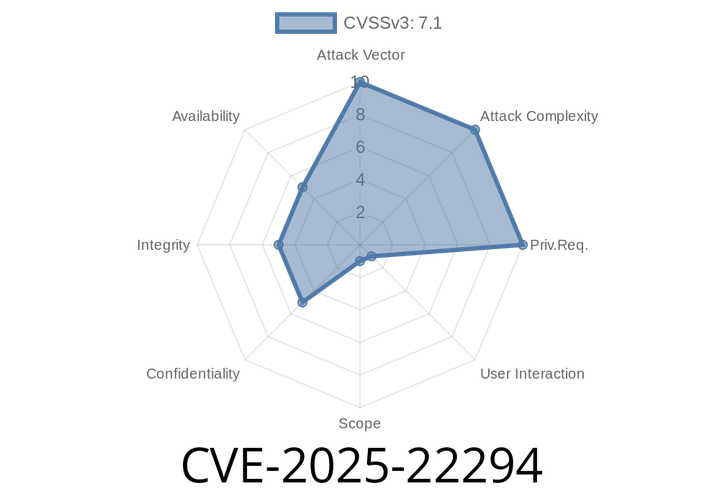
CVE-2025-22294 - Reflected XSS in Gravity Master Custom Field For WP Job Manager – Full Analysis and Exploit Guide
Date: June 2024
Vulnerability Type: Cross-site Scripting (Reflected XSS)
Affected Plugin: Custom Field For WP Job Manager (by Gravity Master)
Versions: All before and
Episode
00:00:00
00:00:00