
CVE-2024-49531 - Exploiting the Acrobat Reader NULL Pointer Dereference DoS Vulnerability
Adobe Acrobat Reader is widely used to view PDF files, making it a popular target for attackers. In June 2024, a vulnerability tracked as CVE-
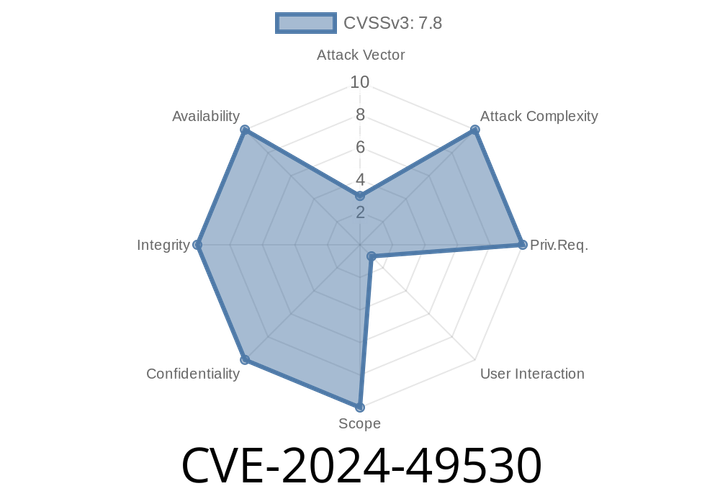
CVE-2024-49530 - Unpacking Adobe Acrobat Reader Use-After-Free Vulnerability and How It Puts Users at Risk
On May 2024, a critical vulnerability tracked as CVE-2024-49530 was revealed in several versions of Adobe Acrobat Reader, one of the most widely
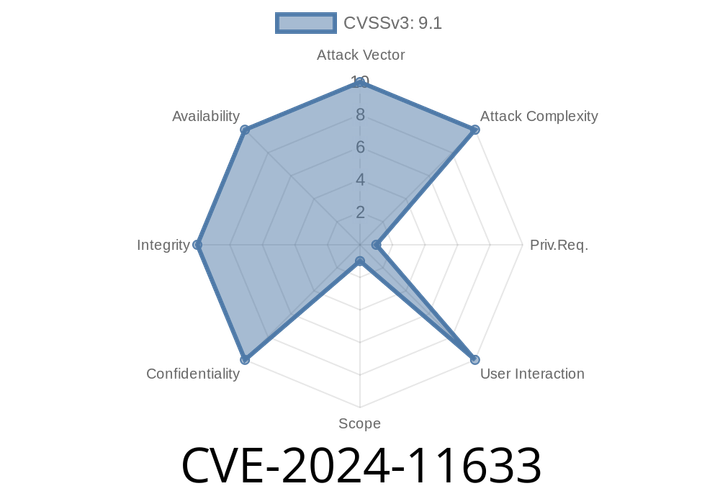
CVE-2024-11633 - Argument Injection Vulnerability in Ivanti Connect Secure (Pre-22.7R2.4) Allows Remote Code Execution for Remote Admins
In early 2024, security researchers discovered and reported a new critical vulnerability affecting Ivanti Connect Secure products (formerly Pulse Connect Secure), tracked as CVE-2024-
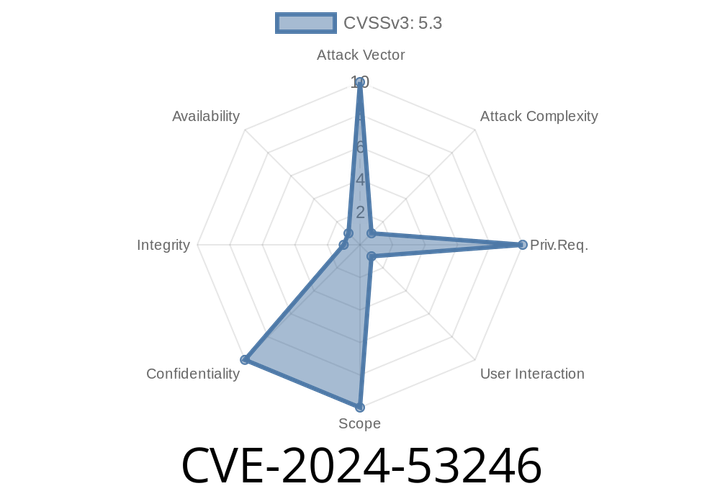
CVE-2024-53246 - Unpacking the Splunk SPL Information Disclosure Vulnerability
Splunk is the backbone SIEM (Security Information and Event Management) solution for many organizations, often ingesting logs from all corners of enterprise infrastructure. Vulnerabilities in
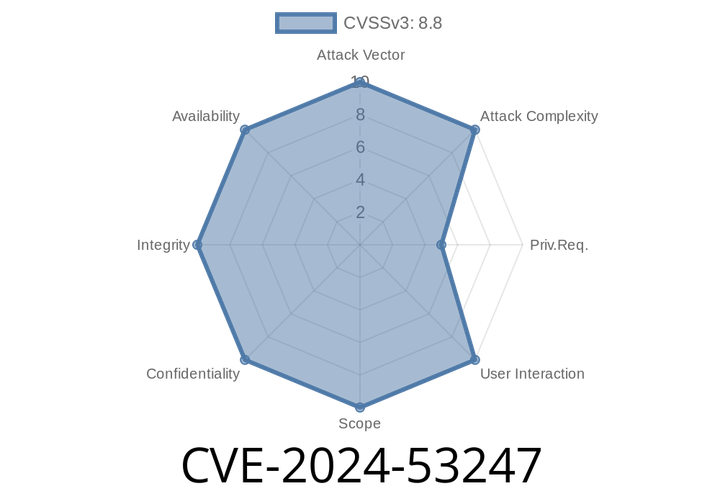
CVE-2024-53247 - Low-Privilege Remote Code Execution in Splunk Enterprise and Secure Gateway App
Splunk is a popular tool used by companies to monitor, search, and analyze machine-generated data. However, in June 2024, a critical vulnerability was disclosed:
Episode
00:00:00
00:00:00