
CVE-2024-12286 - Exploiting Default SSH Credentials on MOBATIME DTS 4801 Network Master Clock
Recently, a new vulnerability was identified in the popular MOBATIME Network Master Clock, specifically in the DTS 4801 model. Tracked as CVE-2024-12286, this
CVE-2024-53866 - How pnpm's Global Cache Vulnerability Can Lead to Arbitrary Code Execution Across Workspaces
The Node.js ecosystem heavily relies on package managers like pnpm for fast, reliable, and space-saving installs. But in June 2024, a nasty vulnerability
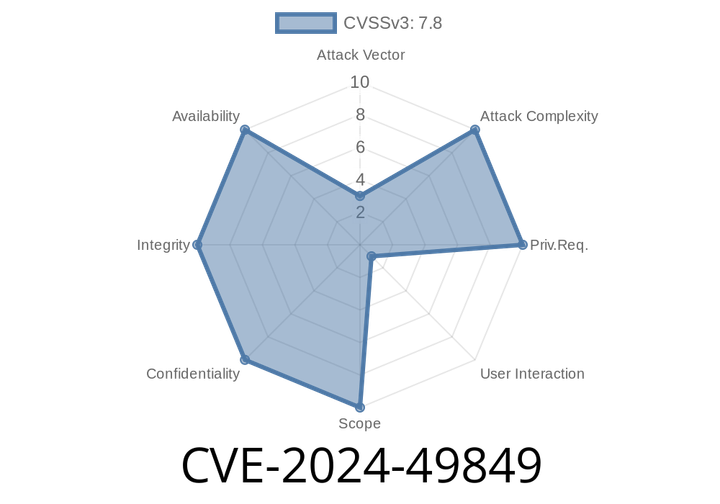
CVE-2024-49849 - Siemens TIA Portal Products Log File Parsing RCE Explained
A new critical vulnerability, CVE-2024-49849, has been discovered affecting a large range of Siemens’ industrial automation products, including their TIA Portal suite. This

CVE-2024-11973 - Reflected XSS Vulnerability in The Quran Multilanguage Text & Audio WordPress Plugin – Full Analysis and Exploit Guide
WordPress is the most popular website platform in the world, powering millions of sites. The plugin ecosystem makes it flexible—but also introduces risks. Recently,
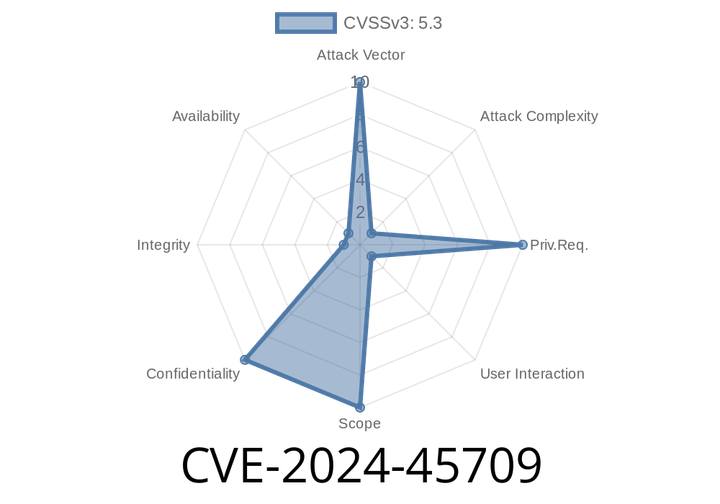
CVE-2024-45709 - Exploiting SolarWinds Web Help Desk’s Local File Read Flaw on Linux in Dev/Test Mode
SolarWinds Web Help Desk is a popular IT ticketing and help desk software. In May 2024, security researchers disclosed a local file read vulnerability, now
Episode
00:00:00
00:00:00