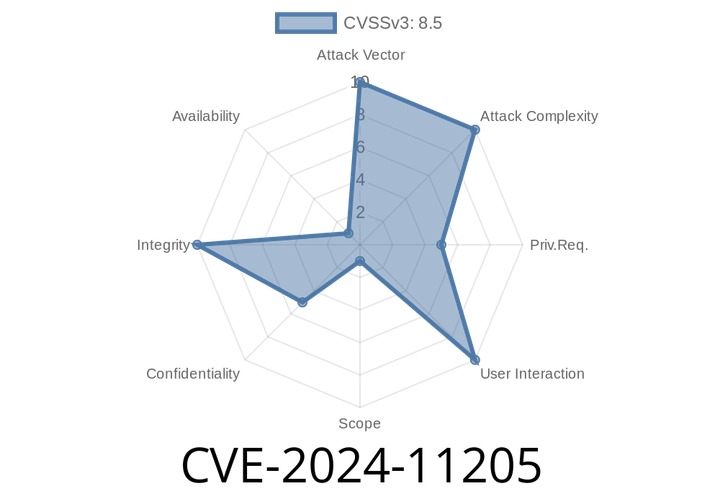
CVE-2024-11205 - WPForms Plugin Vulnerability Allows Unauthorized Data Changes and Payment Refunds
In early 2024, a critical security flaw was discovered in one of WordPress’s most popular plugins: WPForms. Tracked under CVE-2024-11205, this bug
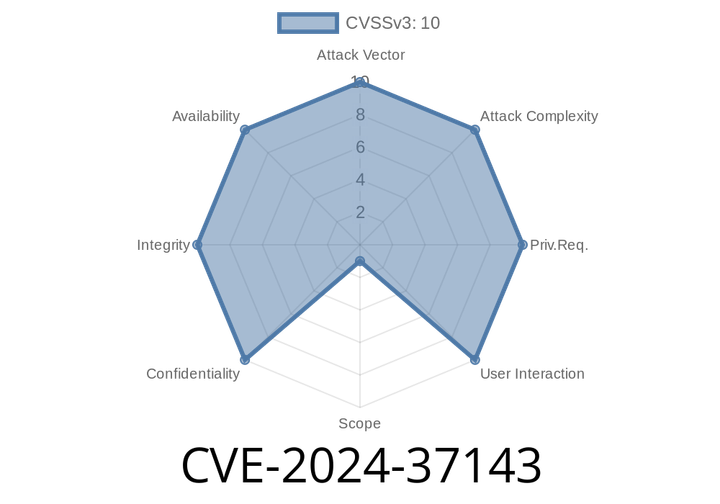
CVE-2024-37143 - Remote Code Execution in Dell PowerFlex and Related Products — Exploit, Analysis, and Remediation
---
Security vulnerabilities in infrastructure platforms can have a wide-reaching impact, and CVE-2024-37143 is a powerful example. This critical vulnerability, found in multiple
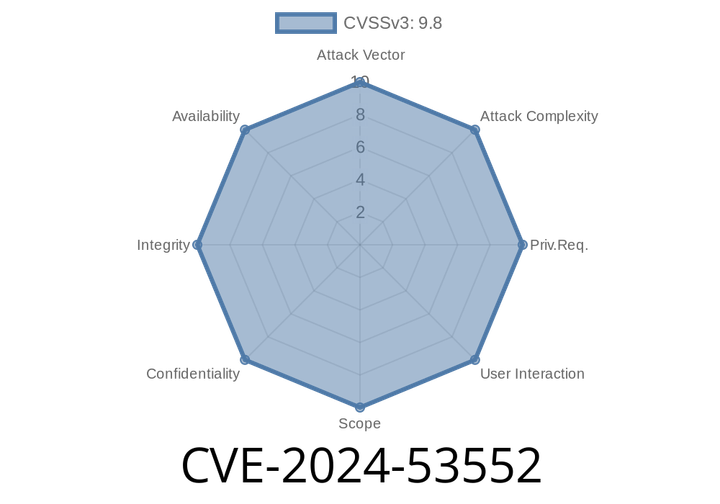
CVE-2024-53552 - How a Simple Password Reset Flaw Exposed Every CrushFTP User to Account Takeover
CrushFTP is a popular file transfer server used worldwide by businesses for securely exchanging sensitive documents. In May 2024, security researchers uncovered a critical vulnerability—
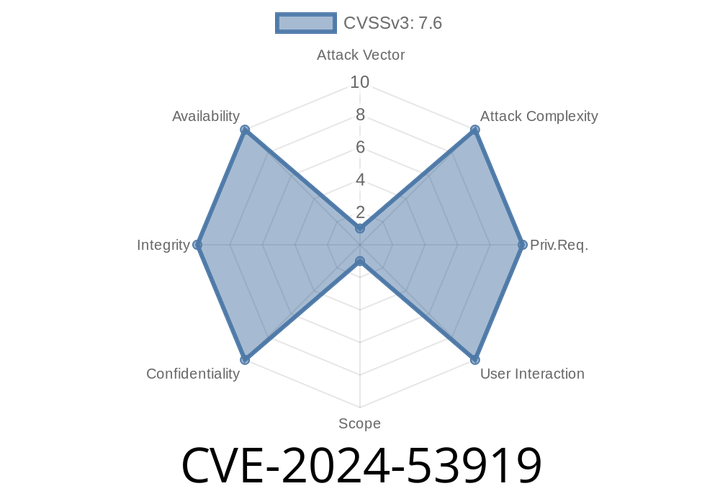
CVE-2024-53919 - How Hackers Can Control Barco ClickShare Devices via Injection Vulnerability (Explained with Exploit Details)
Barco ClickShare is a well-known wireless presentation system used by businesses, schools, and governments worldwide. But in June 2024, security researchers discovered a dangerous
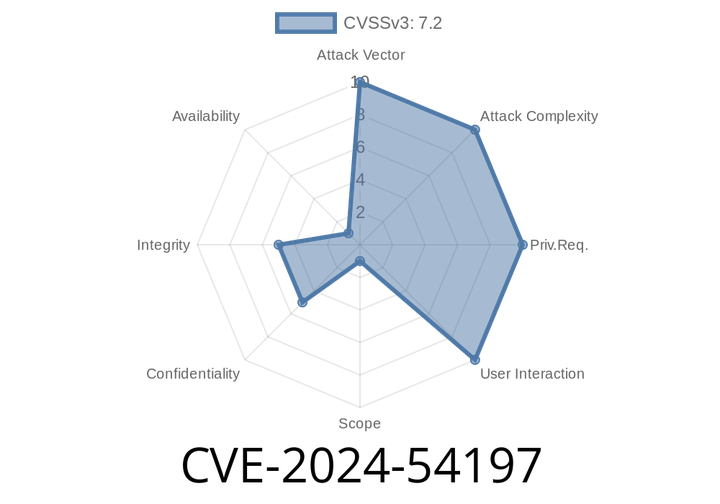
CVE-2024-54197 - SAP NetWeaver Administrator SSRF Vulnerability Explained
SAP NetWeaver is the core platform for many critical business applications. In June 2024, researchers disclosed a new vulnerability—CVE-2024-54197—that could let
Episode
00:00:00
00:00:00