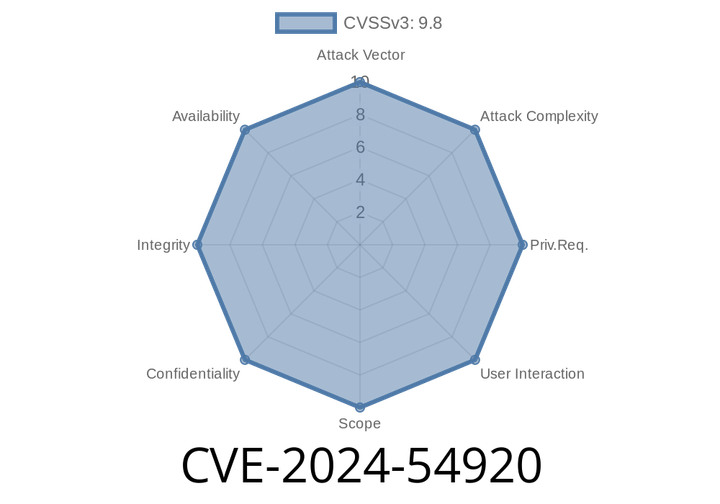
CVE-2024-54920 - SQL Injection in kashipara E-learning Management System v1. (teacher_signup.php) – Exploit Details & Walkthrough
A recently discovered vulnerability, CVE-2024-54920, has made headlines in the security community. This SQL Injection flaw was found in the /teacher_signup.php
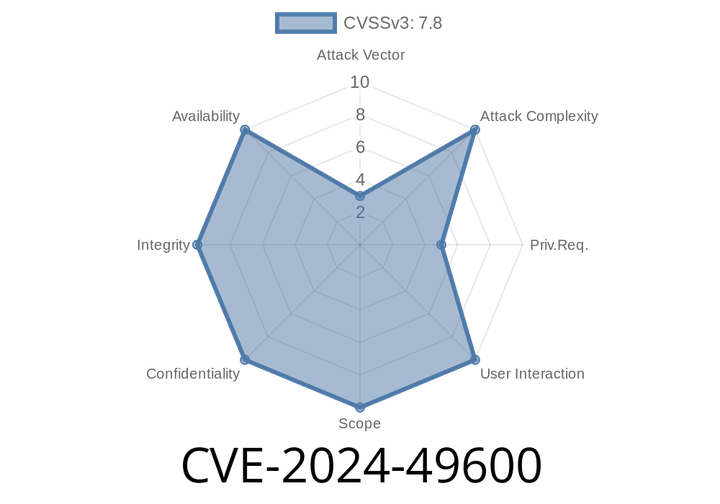
CVE-2024-49600 - How a Vulnerability in Dell Power Manager Could Let Attackers Take Over Your PC
If you are running Dell Power Manager (DPM) on your Windows laptop or desktop, you need to pay serious attention to this. In May 2024,
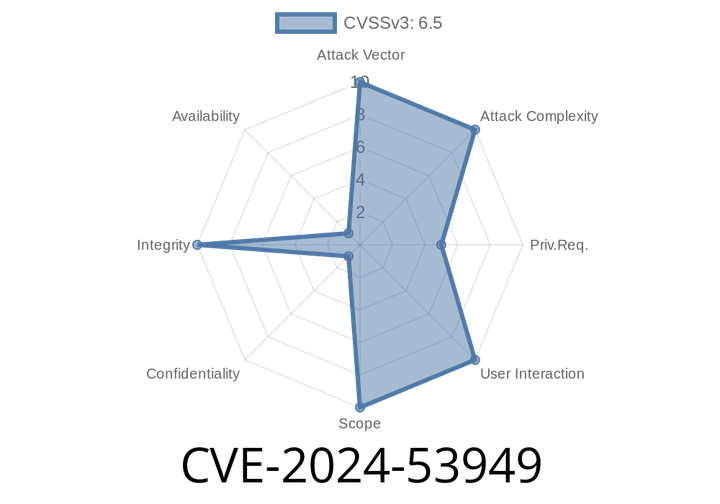
CVE-2024-53949 - How Improper Authorization in Apache Superset Exposed Sensitive APIs (Full Exploit Details Inside)
Published: June 2024
Written by: Security Insights Team
Apache Superset is a popular open-source platform for data exploration and visualization. If your company runs
CVE-2024-53947 - New Wave of SQL Injection in Apache Superset—Fresh Functions, Fresh Danger
Summary:
A fresh SQL Injection vulnerability—CVE-2024-53947—has just hit Apache Superset, affecting all versions below 4.1.. This new issue expands on
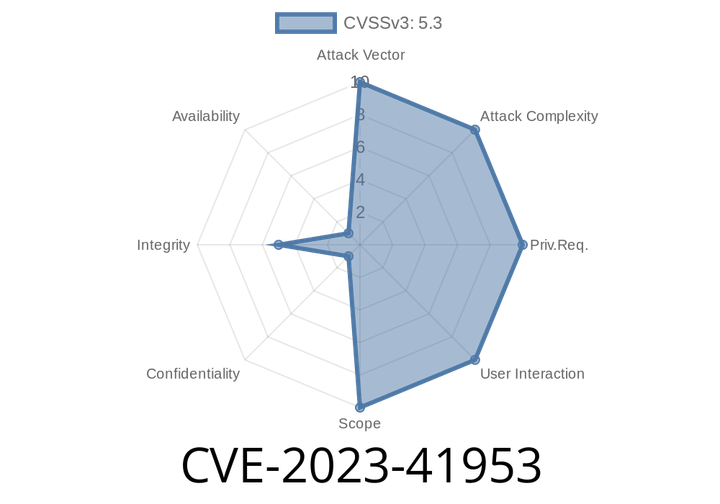
CVE-2023-41953 - Exploiting the Missing Authorization Vulnerability in ProfilePress (v. up to 4.13.1)
---
WordPress powers a huge part of the internet, and plugins are a big reason why. But with popularity comes a target on your back. Today
Episode
00:00:00
00:00:00