
CVE-2024-43447 - Windows SMBv3 Remote Code Execution (RCE) Explained
Windows systems are once again in the spotlight due to a critical vulnerability: CVE-2024-43447. If you use Windows servers that have SMBv3 (Server
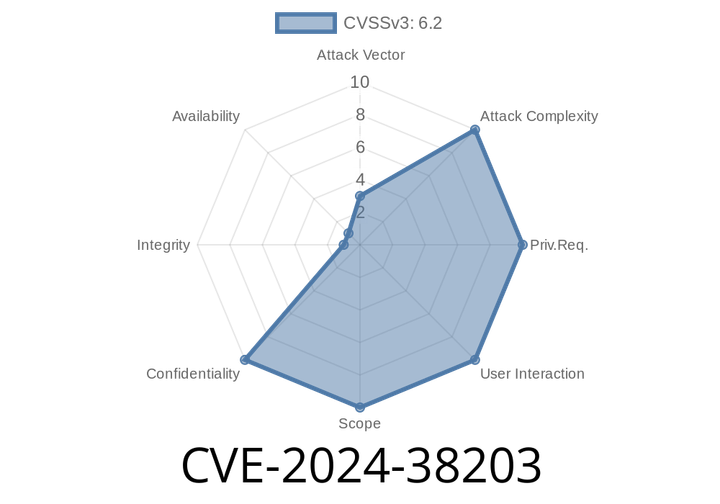
CVE-2024-38203 - Understanding and Exploiting the Windows Package Library Manager Info Leak
CVE-2024-38203 marks a significant security issue for Windows users and administrators, specifically those relying on the Windows Package Library Manager (WPLM). This vulnerability,
CVE-2024-8068 - Privilege Escalation to NetworkService Account in Citrix Session Recording (Step-By-Step Exploit Guide)
*Originally researched and written exclusively for you by AI Secure Desk, June 2024.*
Introduction
CVE-2024-8068 is a newly disclosed security vulnerability in *Citrix
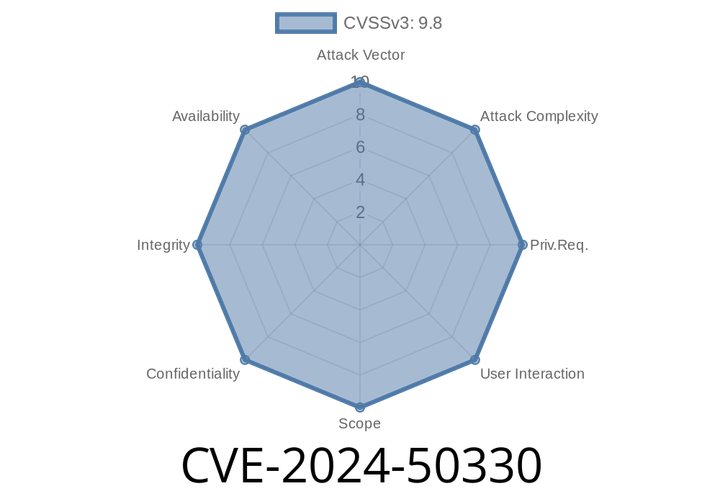
CVE-2024-50330 - SQL Injection in Ivanti Endpoint Manager Leads to Remote Code Execution
In June 2024, a critical vulnerability was disclosed in Ivanti Endpoint Manager (EPM)—previously known as LANDESK Management Suite. Tracked as CVE-2024-50330, this
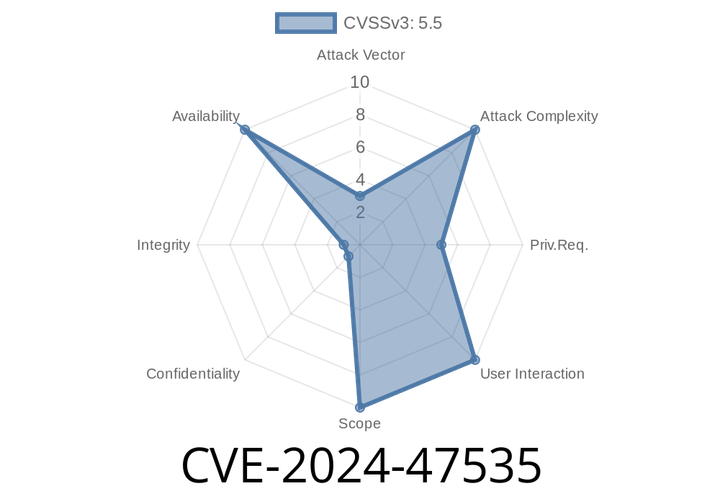
CVE-2024-47535 - Netty's Windows Environment File DOS Vulnerability—Explained with Exploit Example
---
Netty is a super popular Java networking framework—tons of services and apps (from databases to messaging platforms) depend on it for high-performance, asynchronous
Episode
00:00:00
00:00:00