
CVE-2024-50578 - Stored XSS in JetBrains YouTrack Agile Boards - Deep Dive and Exploitation
In June 2024, security researchers uncovered a Stored Cross-Site Scripting (XSS) vulnerability in JetBrains YouTrack, a popular issue and project tracking tool. Assigned the

CVE-2024-50580 - XSS Exploits in JetBrains YouTrack Before 2024.3.47707 — Deep Dive & Exploit Walkthrough
JetBrains YouTrack is a popular issue tracking and project management tool, widely used by teams for managing bugs and project workflows. However, in versions before
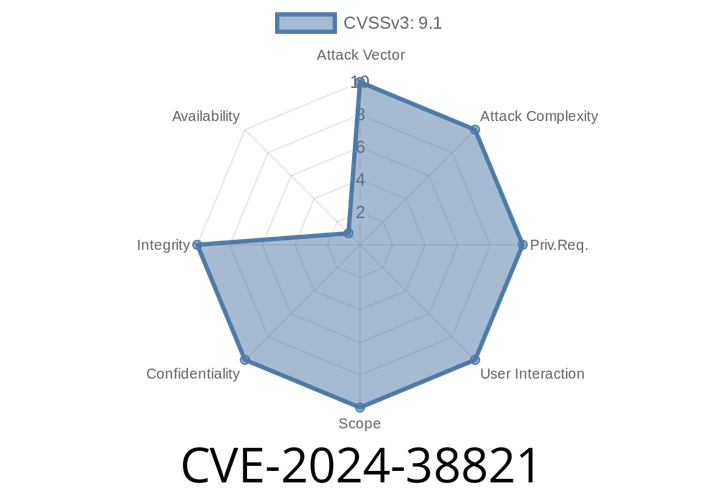
CVE-2024-38821 - Static Resource Authorization Bypass in Spring WebFlux Explained
Spring is widely used for building Java web applications, and Spring WebFlux is its reactive, non-blocking web framework. One of the critical tasks in
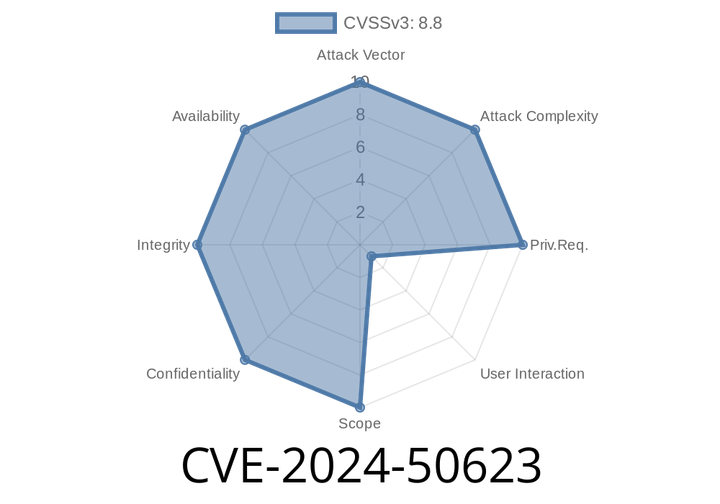
CVE-2024-50623 - How Unrestricted File Upload in Cleo Harmony, VLTrader, and LexiCom Can Lead to Remote Code Execution
In June 2024, a critical security vulnerability was published as CVE-2024-50623. This vulnerability affects multiple products from Cleo: Harmony, VLTrader, and LexiCom — all

CVE-2024-50602 - How a Bug in libexpat (Before 2.6.4) Can Crash Your App – Deep Dive & Exploit Example
---
Libexpat is a well-known C library used for parsing XML. Many projects use it under the hood, from popular Linux tools to commercial software.
Episode
00:00:00
00:00:00