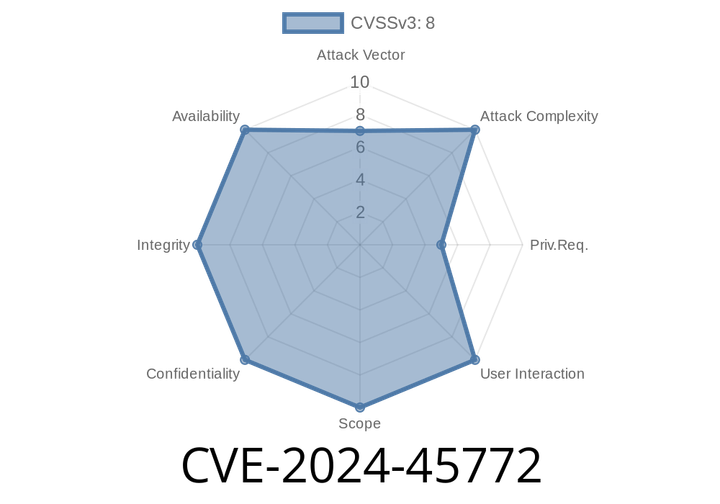
CVE-2024-45772 - Deserialization of Untrusted Data Vulnerability in Apache Lucene Replicator
CVE-2024-45772 is a critical security bug found in the Apache Lucene replicator module, specifically affecting implementations relying on the deprecated org.apache.lucene.
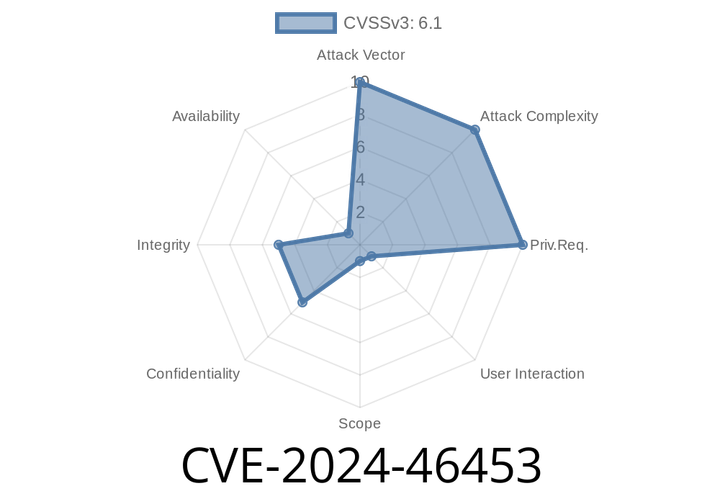
CVE-2024-46453 - Exploiting XSS in **iq3xcite** `/test/` Endpoint (Versions 2.31–3.05)
A new security issue, CVE-2024-46453, has been found in the web application framework iq3xcite versions 2.31 to 3.05. This vulnerability allows
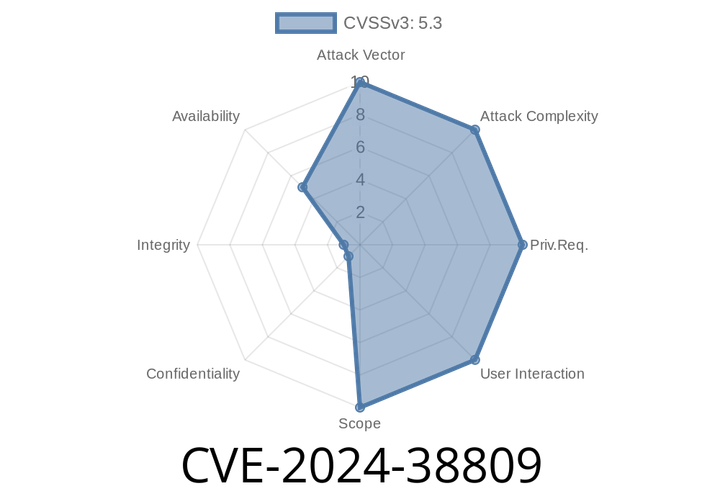
CVE-2024-38809 - ETag Header Parsing Leads to DoS – What You Need to Know
CVE-2024-38809 is a freshly discovered vulnerability that targets applications parsing ETags from the If-Match or If-None-Match HTTP headers. This issue
CVE-2024-46868 - Deadlock in Linux Kernel's Qualcomm UEFI Secure Application Firmware Driver
On May 2024, a significant vulnerability was fixed in the Linux kernel, specifically affecting Qualcomm systems. This bug, assigned as CVE-2024-46868, is tied

CVE-2024-46864 - Broken kexec on Linux Hyper-V Guests – VP Assist Page Corruption Explained
Recently fixed in the Linux kernel, CVE-2024-46864 was causing kexec crashes for users running Linux on Hyper-V. If you’re running virtual
Episode
00:00:00
00:00:00