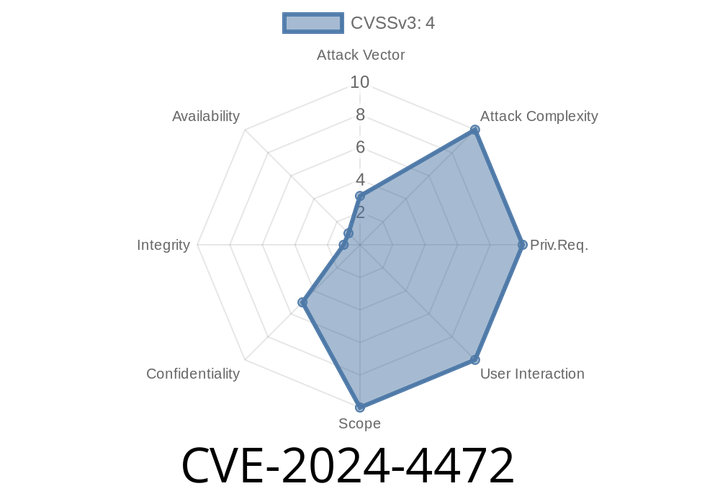
CVE-2024-4472 - GitLab Dependency Proxy Credentials Leak via GraphQL Logs — In-Depth Analysis and Exploit Example
Table of Contents
Introduction
In June 2024, GitLab disclosed a sensitive security issue, now tracked as CVE-2024-4472. If you use GitLab's
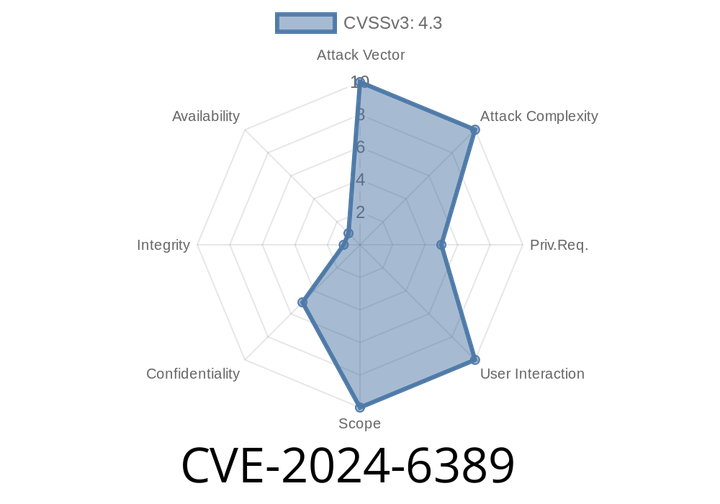
CVE-2024-6389 - GitLab Guest User Information Leak via Release Atom Feed – Full Details & Exploit Guidance
Recently, a critical vulnerability—CVE-2024-6389—was uncovered in GitLab Community Edition (CE) and Enterprise Edition (EE). This issue allows a guest user to

CVE-2024-6446 - GitLab Open Redirect Vulnerability Empowers Phishing Attacks (with Code Example & Exploit Details)
In June 2024, a critical vulnerability was reported in GitLab, the popular DevOps platform. CVE-2024-6446 is an "Open Redirect" issue affecting
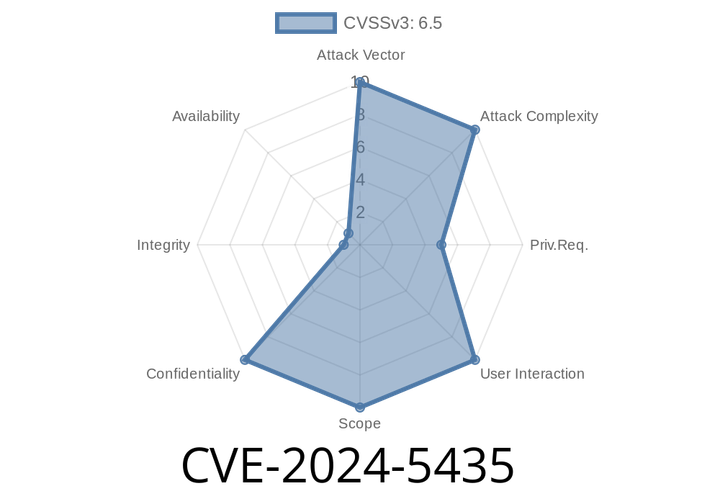
CVE-2024-5435 - GitLab EE/CE Password Disclosure in Repository Mirror Configuration (Exclusive Deep Dive)
---
GitLab, the industry’s favorite DevOps tool, is again in the spotlight—not for innovative features, but for a severe security flaw: CVE-2024-5435.
CVE-2024-8522 - SQL Injection in LearnPress WordPress Plugin – How It Works, Exploit Example, and What to Do Next
If you run an online learning site using LearnPress on WordPress, you need to act fast. CVE-2024-8522 has revealed a critical SQL injection
Episode
00:00:00
00:00:00