CVE-2024-6677 - Privilege Escalation in uberAgent – What It Is, How It Works, and Exploit Details
Privilege escalation vulnerabilities are a nightmare for IT administrators and security teams because they give attackers a shortcut to complete control over a system. In
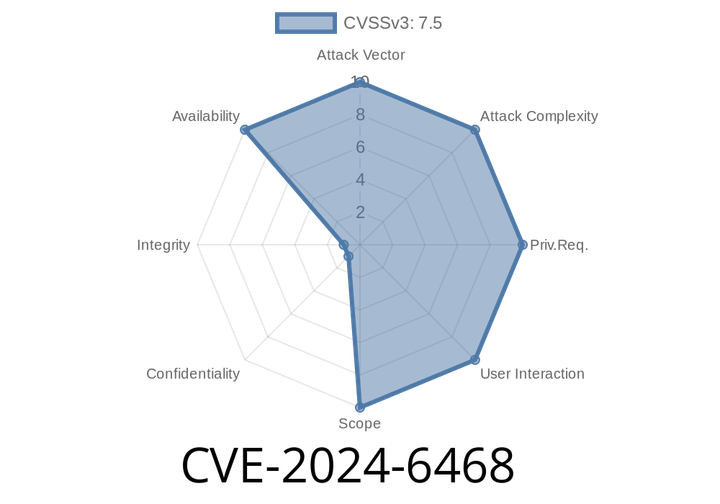
CVE-2024-6468 - How a Simple IP Check in Vault Could Trigger Denial of Service
In June 2024, a serious vulnerability was disclosed in HashiCorp Vault and Vault Enterprise, tracked as CVE-2024-6468. This bug allowed unauthenticated attackers to
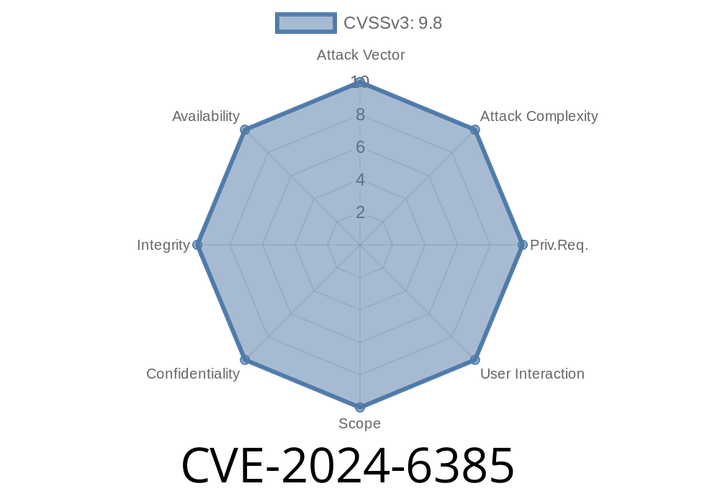
CVE-2024-6385 - GitLab Pipeline Impersonation Vulnerability — Deep Dive, Exploit, and Protection
A serious security vulnerability was found in GitLab Community Edition (CE) and Enterprise Edition (EE): CVE-2024-6385. This flaw lets attackers trigger CI/CD

CVE-2024-5470 - GitLab CE/EE Vulnerability Allowing Guest Users to Create Project-Level Deploy Tokens
CVE-2024-5470 addresses a critical vulnerability that was discovered in the GitLab CE/EE (Community Edition/Enterprise Edition) software. This issue impacts all versions
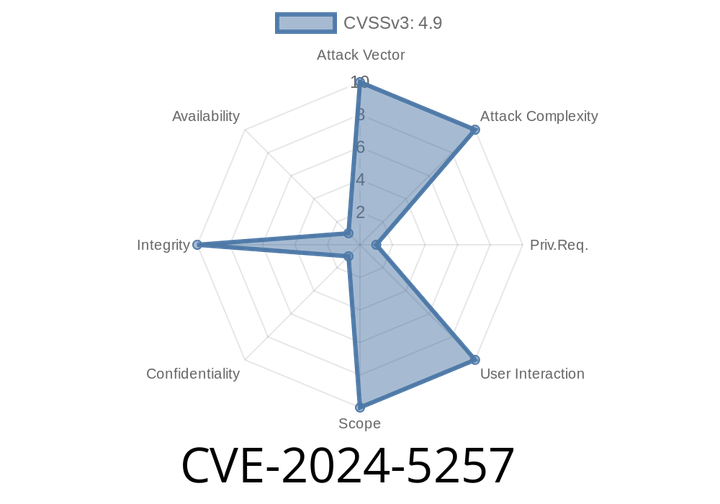
CVE-2024-5257 - Exploiting Group Namespace URL Change in GitLab Custom Roles (Explained Simply)
In June 2024, a security issue was discovered in GitLab CE/EE, affecting all versions starting from 17. up to (but not including) 17..4,
Episode
00:00:00
00:00:00