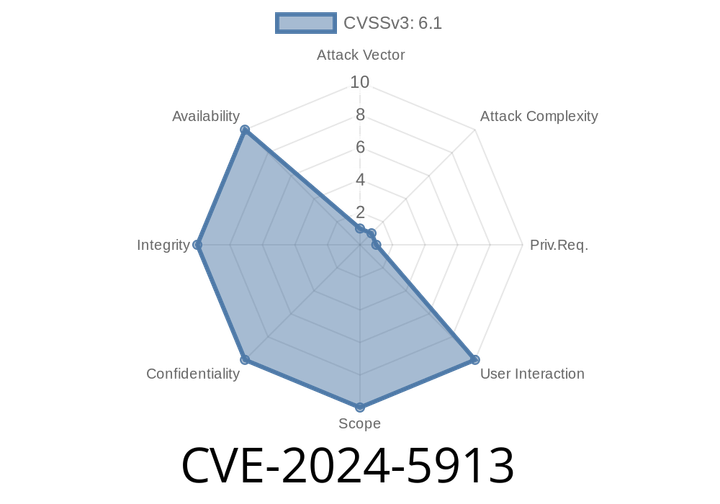
CVE-2024-5913 - How Improper Input Validation in Palo Alto Networks PAN-OS Can Lead to Privilege Escalation
On June 14, 2024, Palo Alto Networks confirmed a new security vulnerability tracked as CVE-2024-5913. This flaw impacts PAN-OS—Palo Alto’s
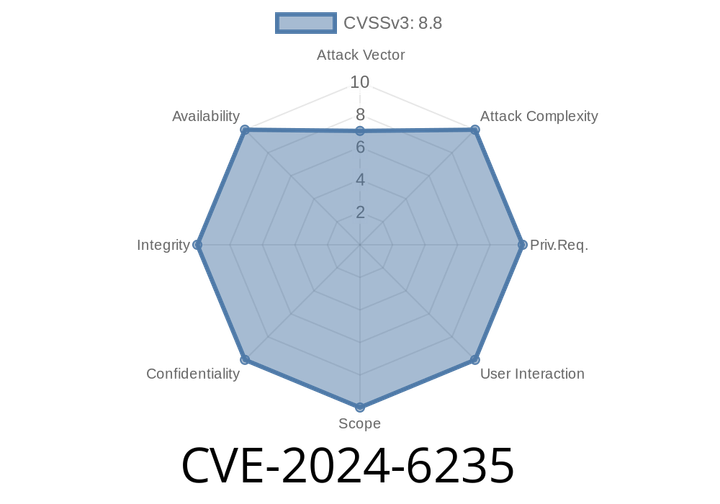
CVE-2024-6235 - Sensitive Information Disclosure in NetScaler Console Explained
In June 2024, a big security bug was found in NetScaler (formerly Citrix ADC) Console—tracked as CVE-2024-6235. This vulnerability makes it possible

CVE-2024-5492 - Open Redirect Vulnerability in NetScaler ADC & NetScaler Gateway – Complete Analysis, Proof of Concept & Protection
Open redirects are a classic web security issue but still often underestimated. Recently, CVE-2024-5492 was discovered in popular Citrix products – NetScaler ADC (formerly

CVE-2024-5491 - Denial of Service in NetScaler ADC and NetScaler Gateway Explained
Citrix’s NetScaler ADC and NetScaler Gateway are widely-used tools in enterprise environments for application delivery and secure remote access. However, like all complex
CVE-2024-5911 - How Attackers Can Crash Palo Alto Networks Panorama with an Authenticated File Upload Exploit
A high-impact vulnerability, CVE-2024-5911, was recently discovered in Palo Alto Networks Panorama software. This security flaw allows an authenticated administrator to upload
Episode
00:00:00
00:00:00