CVE-2024-38477 - How a Null Pointer in mod_proxy Can Crash Your Apache HTTP Server
If you're running an Apache HTTP Server, especially with the popular mod_proxy enabled, there's big news you shouldn’t ignore.
CVE-2024-38473 - How an Encoding Flaw in Apache HTTP Server mod_proxy Lets Attackers Bypass Backend Authentication
Summary:
A critical vulnerability, CVE-2024-38473, was discovered in Apache HTTP Server’s mod_proxy (versions 2.4.59 and earlier). This encoding flaw
CVE-2024-38472 - SSRF in Apache HTTP Server (Windows) Leaking NTLM Hashes — Exploit Details and Mitigation Guide
A new vulnerability, CVE-2024-38472, was discovered in the Apache HTTP Server (httpd) for Windows. This is a Server-Side Request Forgery (SSRF) flaw
CVE-2024-38476 - How a Core Bug in Apache HTTP Server 2.4.59 Exposes Sensitive Data, Enables SSRF and Local Script Execution
Apache HTTP Server is one of the most used web servers worldwide. But in June 2024, a high-impact vulnerability, CVE-2024-38476, was found
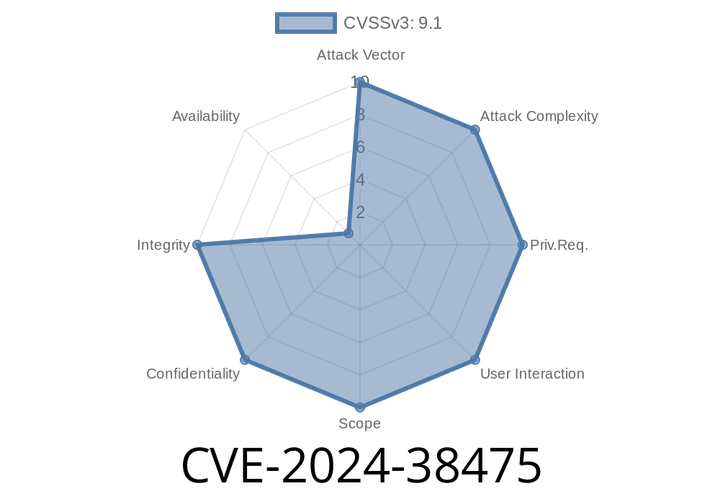
CVE-2024-38475 - Exploiting Unsafe Output Escaping in Apache mod_rewrite for Code Execution and Source Disclosure
---
Introduction
Apache HTTP Server is one of the most popular web servers worldwide, essential for hosting millions of websites. But like all complex software, it
Episode
00:00:00
00:00:00