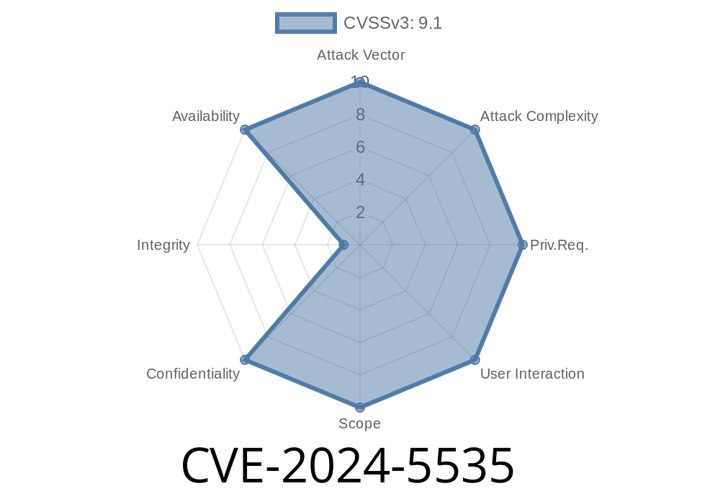
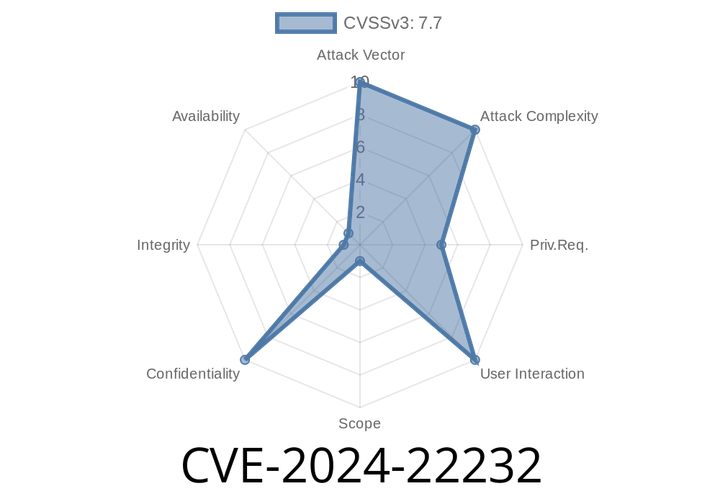

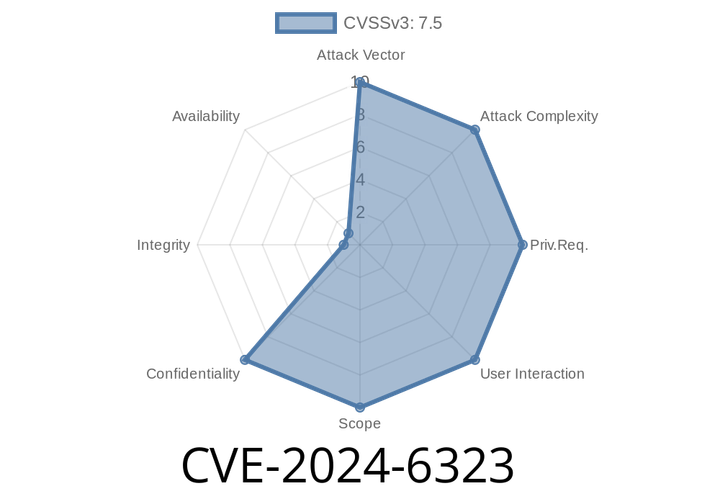
CVE-2024-6323 - GitLab Global Search Improper Authorization Leaks Private Repo Content in Public Projects
Published: July 2024
Author: AI Editorial
GitLab is a leading tool for managing code, projects, and CI/CD pipelines. It’s widely used by organizations
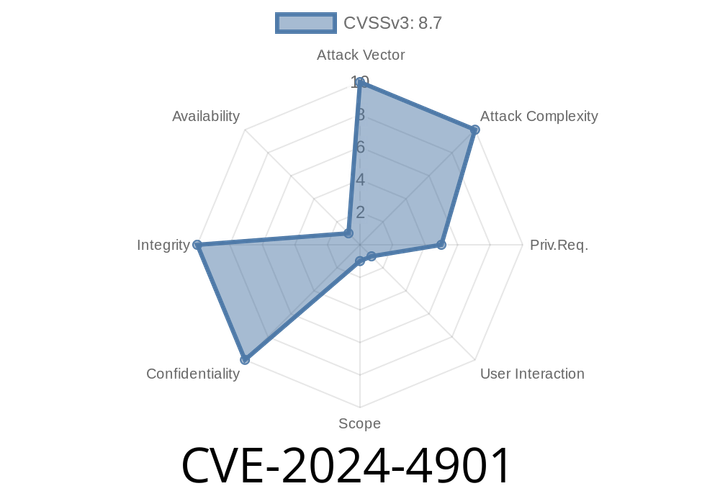
CVE-2024-4901 - Stored XSS in GitLab’s Commit Notes – Detailed Analysis and Exploitation Guide
On May 30, 2024, the GitLab team disclosed CVE-2024-4901, a severe Stored Cross-Site Scripting (XSS) vulnerability introduced in GitLab Community and Enterprise