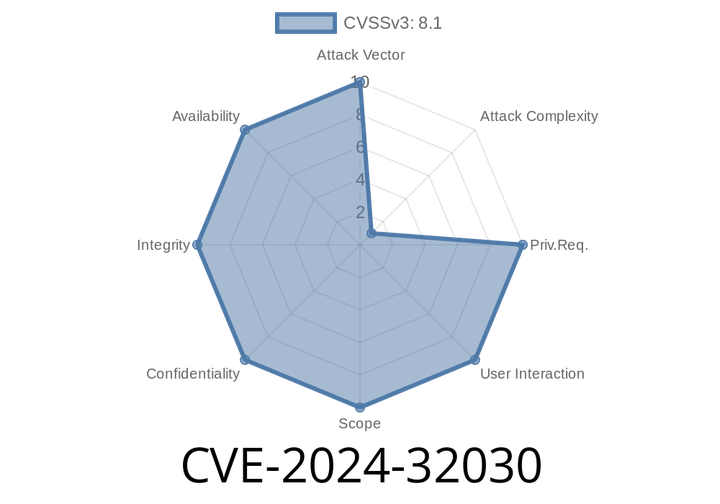
CVE-2024-32030 - Remote Code Execution in Kafka UI via JMX/RMI Deserialization
A high-severity vulnerability, CVE-2024-32030, was found in Kafka UI, a popular open-source tool for managing Apache Kafka clusters. The flaw allows
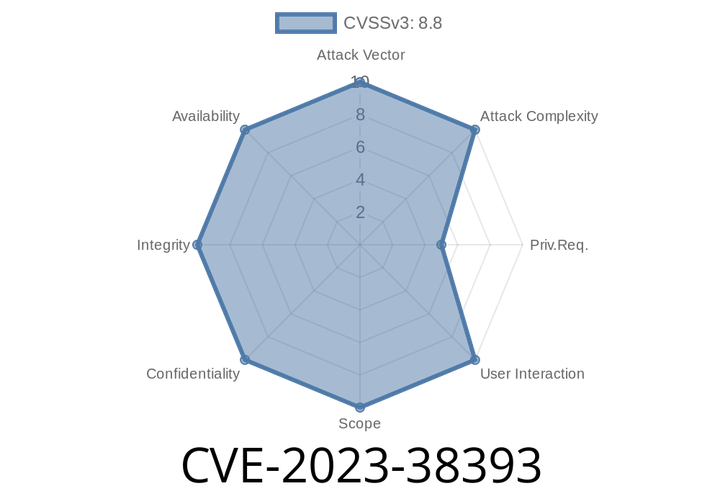
CVE-2023-38393 - Missing Authorization in Ninja Forms Plugin (Version n/a through 3.6.25) — How Attackers Exploit It and How to Fix
If you use WordPress to run your website, chances are you rely on plugins to make life easier. One of the most popular is Ninja
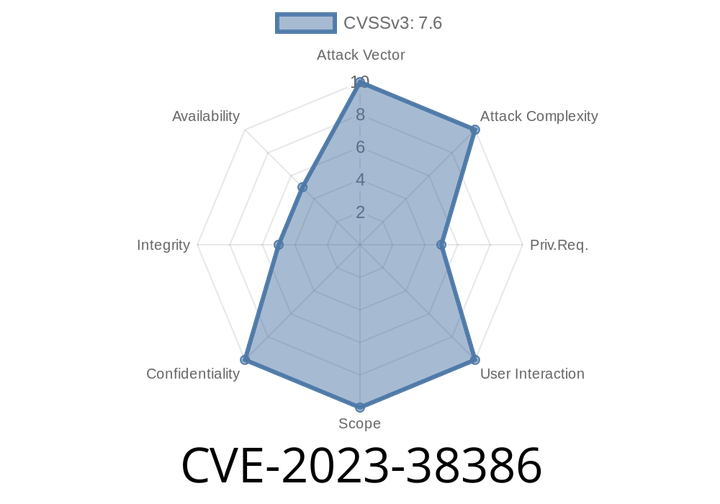
CVE-2023-38386 - Missing Authorization in Ninja Forms (Saturday Drive) – What You Need to Know & Simple Exploit Guide
If you rely on the popular Ninja Forms plugin for WordPress, you need to read about CVE-2023-38386. This is a Missing Authorization vulnerability
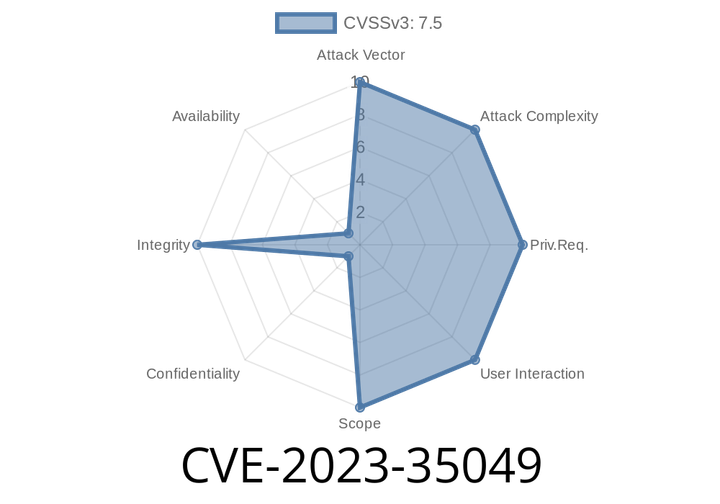
CVE-2023-35049 - Missing Authorization in WooCommerce Stripe Payment Gateway (<=7.4.) – Exploit Analysis and Example
WooCommerce is the world’s most popular e-commerce plugin for WordPress. With millions of stores relying on it, it’s no surprise that its
CVE-2023-47681 - How a Missing Authorization Bug in WooCommerce Checkout Manager (<= 7.3.) Puts Your Store at Risk
---
If you’re running a WordPress site with WooCommerce, chances are you use plugins to smooth out your customer’s shopping experience. One popular plugin
Episode
00:00:00
00:00:00