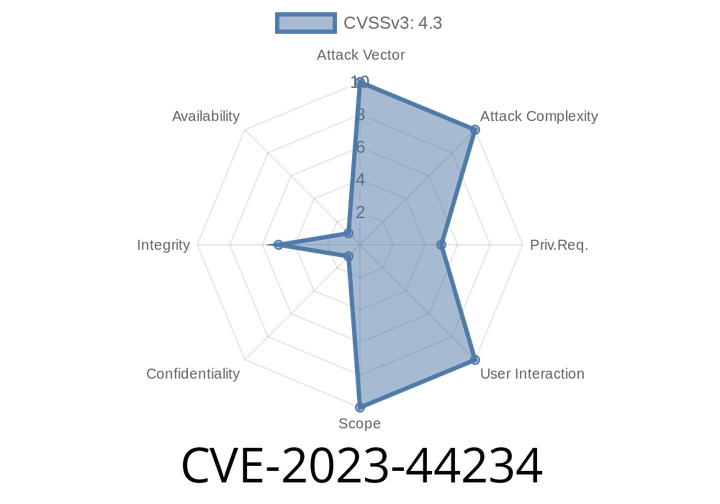
CVE-2023-44234 - Missing Authorization Flaw Discovered in WP GPX Map (from n/a to 1.7.08) – Full Details and Exploit Explained
In September 2023, a new WordPress vulnerability was discovered and cataloged as CVE-2023-44234. This flaw affects the popular *WP GPX Map* plugin by
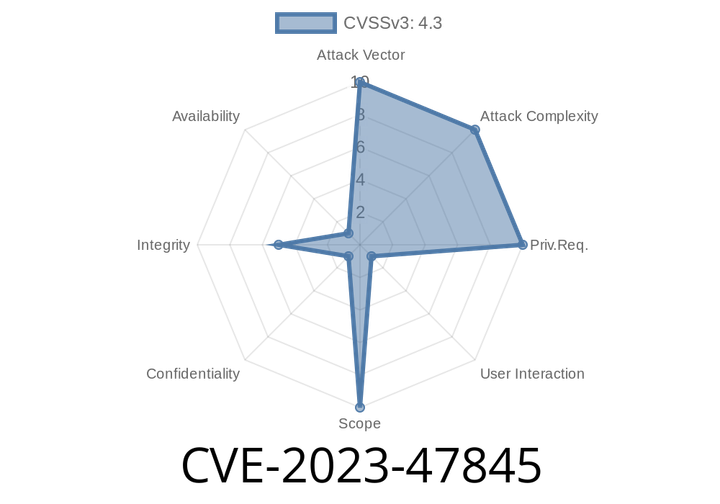
CVE-2023-47845 - Deep Dive into the CSRF Vulnerability in Grab & Save Plugin (Lim Kai Yang) - Exploit, Code & Analysis
In late 2023, security researchers identified a Cross-Site Request Forgery (CSRF) vulnerability with the identifier CVE-2023-47845 in the Grab & Save WordPress
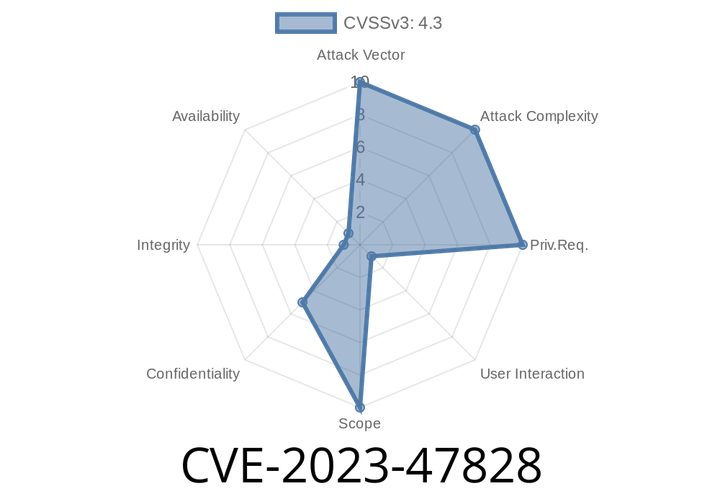
CVE-2023-47828 - Missing Authorization in Mandrill wpMandrill – What You Need to Know
---
Introduction
A critical security vulnerability, identified as CVE-2023-47828, has been discovered in the WordPress plugin wpMandrill—a popular integration for sending emails through

CVE-2024-35225 - Reflected XSS Vulnerability in Jupyter Server Proxy — How Attackers Can Hijack Your JupyterLab
A new security vulnerability has been discovered in the popular Jupyter Server Proxy extension, tracked as CVE-2024-35225. This bug exposes users to reflected
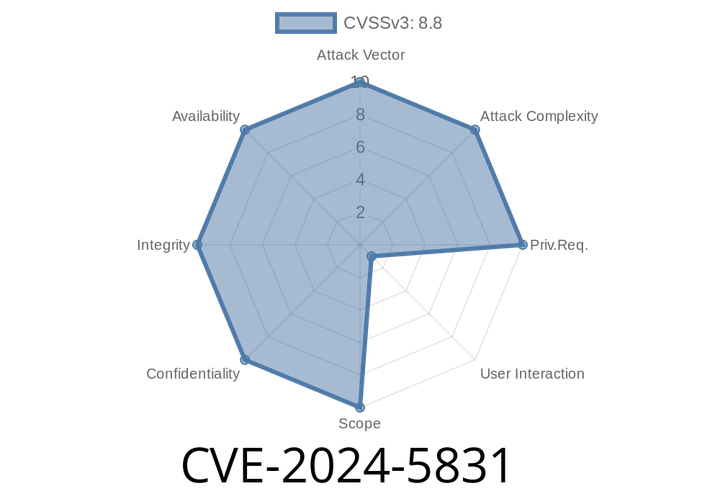
CVE-2024-5831 - High Severity "Use-After-Free" in Dawn (Chromium) - Bug, Exploit, and Analysis
CVE-2024-5831 is a high severity "use-after-free" vulnerability lurking in Google's Chrome browser, specifically in the Dawn backend
Episode
00:00:00
00:00:00