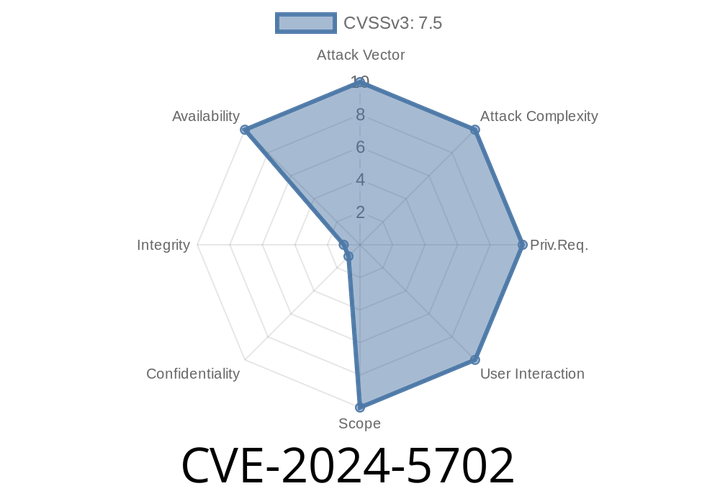
CVE-2024-5702 - Memory Corruption Vulnerability in Firefox, Thunderbird — How a Networking Stack Bug Exposed Millions
---
In June 2024, Mozilla addressed a critical security issue identified as CVE-2024-5702. This vulnerability involved memory corruption in the networking stack of Firefox,

CVE-2024-5700: A Deep Dive into the Memory Safety Bugs in Firefox 126, Firefox ESR 115.11, and Thunderbird 115.11 and Their Potential Exploits
The CVE-2024-5700 vulnerability is a potent memory safety bug identified in Firefox 126, Firefox ESR 115.11, and Thunderbird 115.11. Not all

CVE-2024-5696 - Firefox, ESR, and Thunderbird Input Tag Vulnerability Exploitation Explained
In June 2024, a new high-severity security vulnerability was disclosed and tracked as CVE-2024-5696. This bug affects multiple Mozilla products, including Firefox,
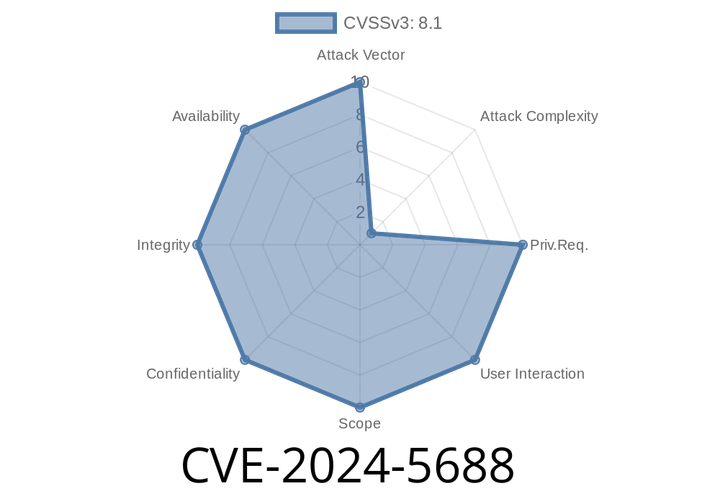
CVE-2024-5688 - Firefox Use-After-Free Exploit in Object Transplant (`Firefox < 127`, ESR < 115.12, Thunderbird < 115.12)
The cybersecurity world is buzzing over CVE-2024-5688, a critical vulnerability discovered in Firefox and Mozilla products. This flaw revolves around a subtle, yet
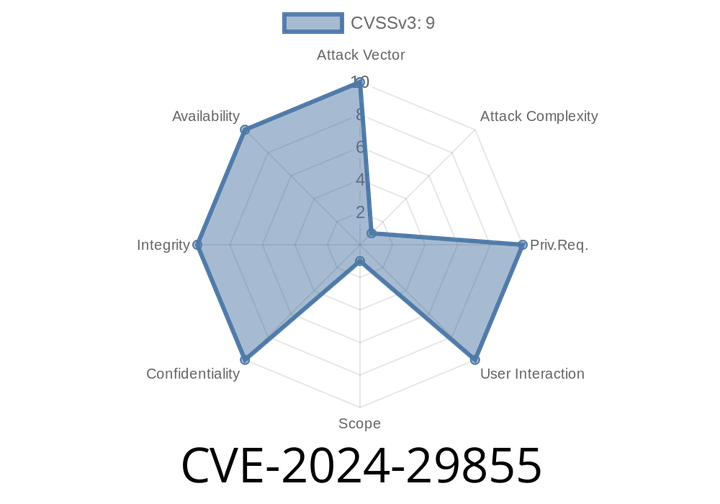
CVE-2024-29855 - Hard-coded JWT Secret Opens Door to Authentication Bypass in Veeam Recovery Orchestrator
CVE-ID: CVE-2024-29855
Product: Veeam Recovery Orchestrator (VRO)
Vulnerability: Hard-coded JWT secret leads to authentication bypass
Severity: Critical
Veeam Recovery Orchestrator is
Episode
00:00:00
00:00:00