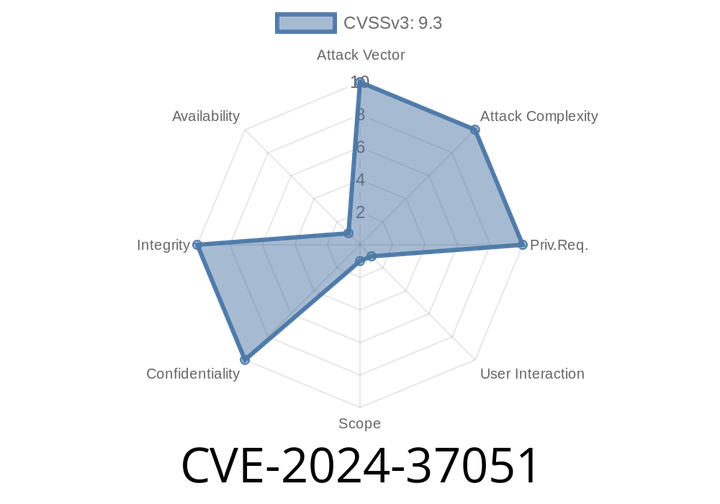
CVE-2024-37051 - GitHub Access Token Exposure in JetBrains IDEs – What Happened, How to Exploit, and How to Fix
---
References and Further Reading
10. Conclusion
1. Introduction
JetBrains IDEs like IntelliJ IDEA, PyCharm, and WebStorm are used by millions of developers worldwide. These IDEs
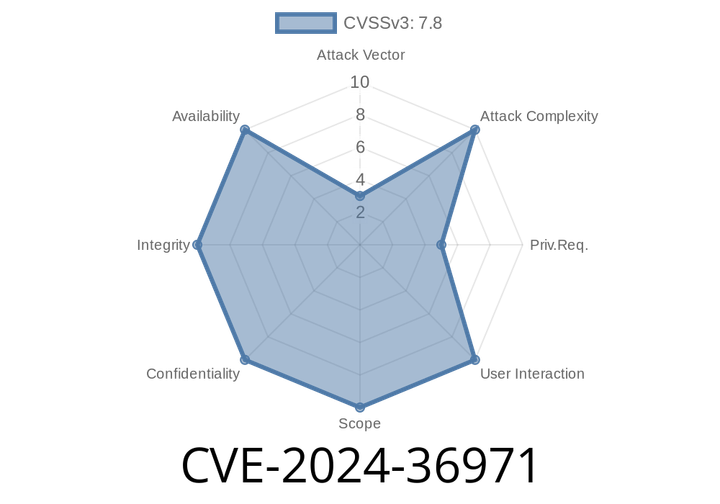
CVE-2024-36971 - Race Condition in Linux Kernel's __dst_negative_advice() Leads to Use-After-Free (UAF)
A critical race condition vulnerability—CVE-2024-36971—was discovered and patched in the Linux kernel, affecting the networking subsystem. This flaw lies in the
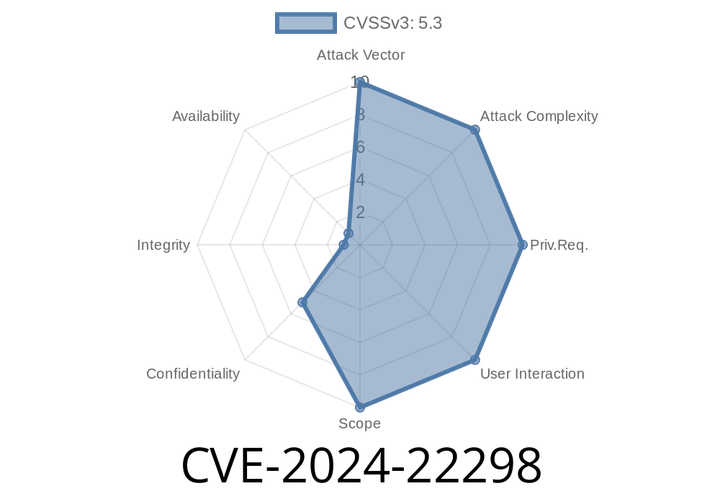
CVE-2024-22298 - Missing Authorization in TMS Amelia Bookings Plugin Can Lead to Unauthorized Access — Detailed Breakdown
In June 2024, CVE-2024-22298 was assigned to a critical security flaw found in the widely-used TMS Amelia WordPress plugin (also known as
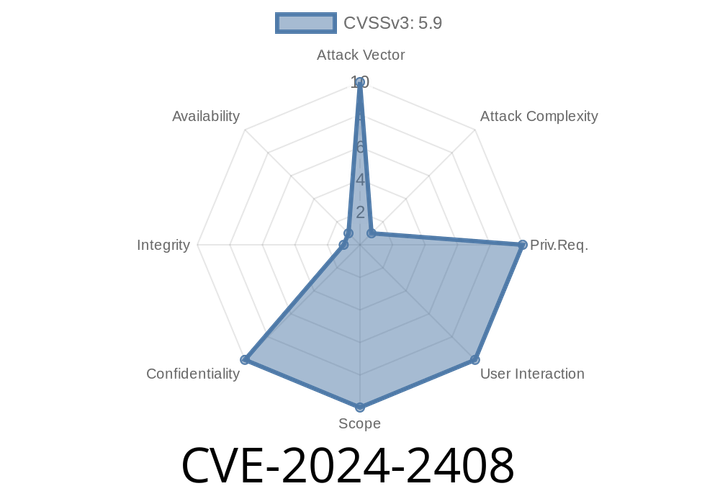
CVE-2024-2408 - PHP's openssl_private_decrypt and the Hidden Risk Behind the Marvin Attack
A new vulnerability tracked as CVE-2024-2408 has come to light, affecting the way PHP handles decryption using its openssl_private_decrypt() function with
CVE-2024-4577 - PHP CGI "Best-Fit" Unicode Encoding Flaw on Windows Lets Attackers Run Arbitrary Code
In June 2024, security researchers revealed a severe vulnerability affecting PHP when deployed through CGI under Apache on Windows. The issue, tracked as CVE-2024-
Episode
00:00:00
00:00:00