
CVE-2024-5458 - PHP’s FILTER_VALIDATE_URL Flaw Lets Invalid URLs Slip Through
PHP is one of the main programming languages used to create dynamic websites and web applications. Its powerful functions—like filter_var()—help developers validate
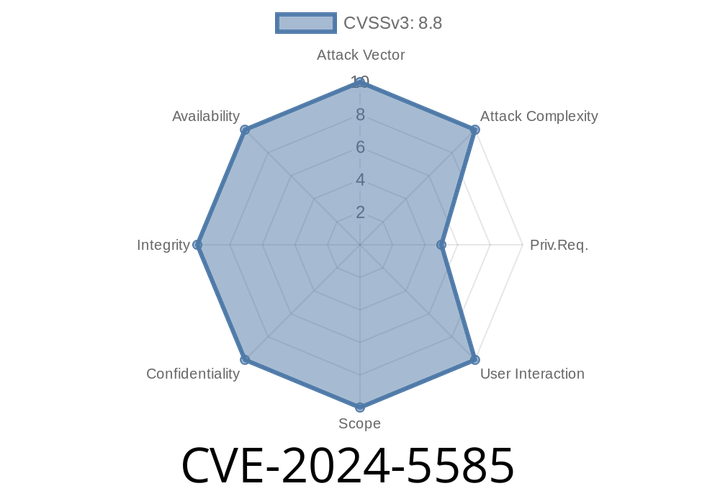
CVE-2024-5585 - How a Trailing Space Broke PHP’s Command Protection Again
PHP is the backbone language of the web, and whenever a critical security bug appears, it echoes across millions of servers. If you’re running
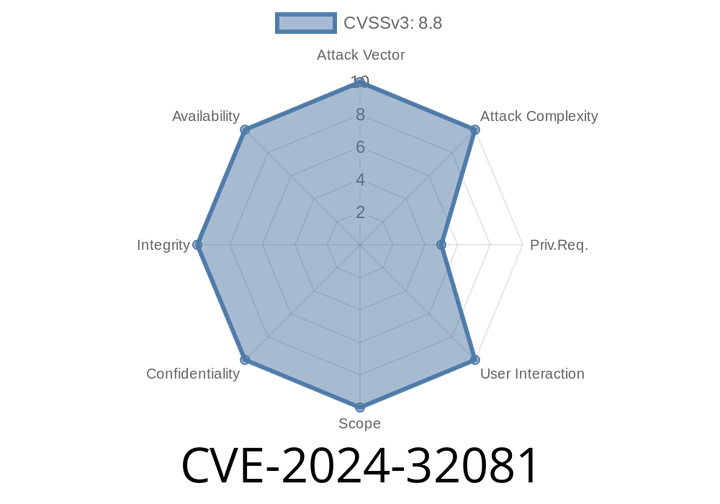
CVE-2024-32081 - How a Missing Authorization Vulnerability in Websupporter Filter Custom Fields & Taxonomies Light Puts WordPress Sites at Risk
The WordPress ecosystem is rich with plugins that make it easy to customize websites. But sometimes, plugins bring not just features, but also dangerous security
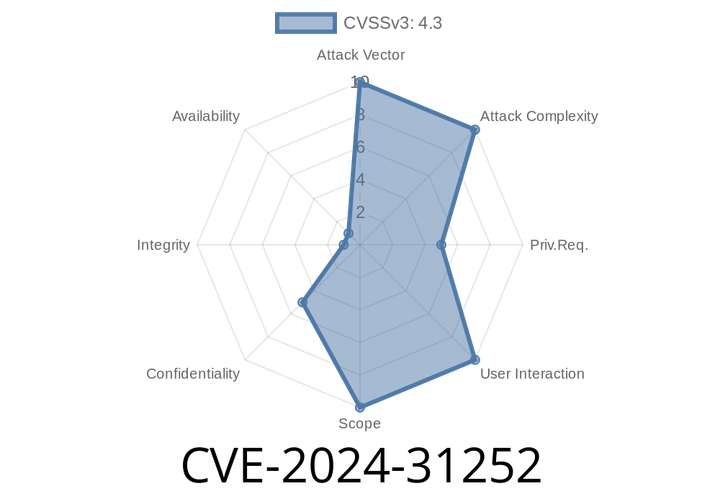
CVE-2024-31252 - Exploiting Missing Authorization in dFactory Responsive Lightbox (<=2.4.6)
WordPress plugins are a favorite target for attackers, and missing authorization bugs can lead to devastating consequences. CVE-2024-31252 is one such critical vulnerability,
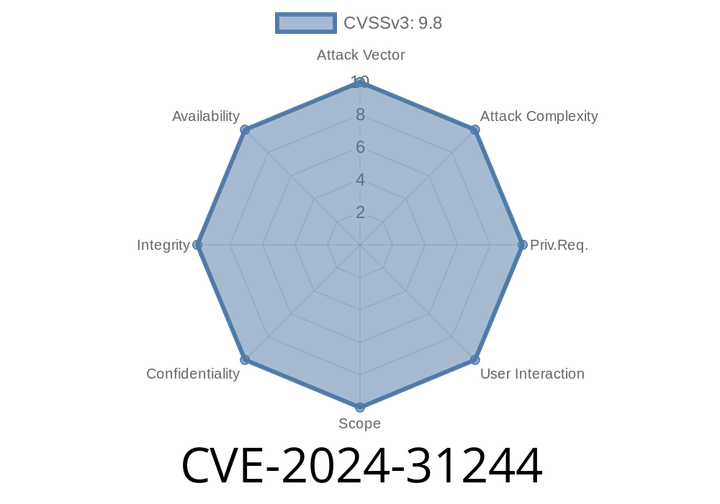
CVE-2024-31244 - Missing Authorization in Bricksforge up to 2..17 – Full Exploit Breakdown
In May 2024, a critical security hole, CVE-2024-31244, was discovered in the popular WordPress plugin, Bricksforge, up to and including version 2..17.
Episode
00:00:00
00:00:00