
CVE-2022-39070 - Remote Access Control Bypass in ZTE PON OLT Devices – Detailed Analysis & Exploit Example
ZTE is a leading provider of networking equipment around the world. Unfortunately, like other tech giants, ZTE equipment can sometimes have dangerous flaws. One such

CVE-2022-44808 - Breaking Down Command Injection in D-Link DIR-823G Routers
In 2022, security researchers disclosed a serious vulnerability in the D-Link DIR-823G Wi-Fi routers that could let hackers take full control of
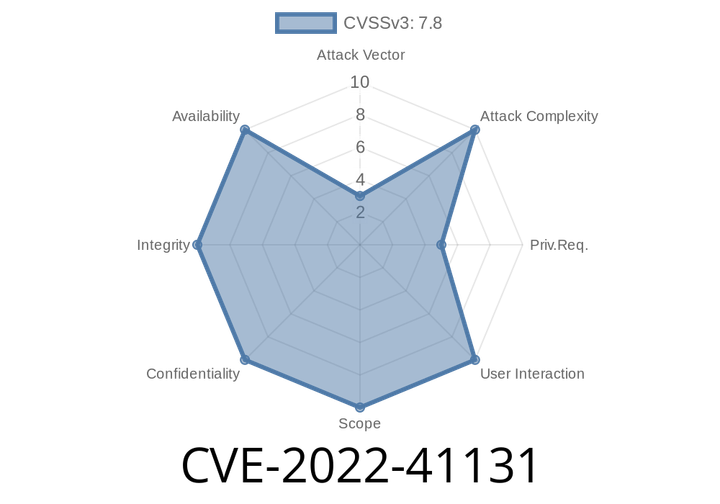
CVE-2022-41131 - OS Command Injection in Apache Airflow Hive Provider Explained
On October 17, 2022, a new vulnerability was disclosed in the Apache Airflow Hive Provider: CVE-2022-41131. This security issue is caused by *Improper
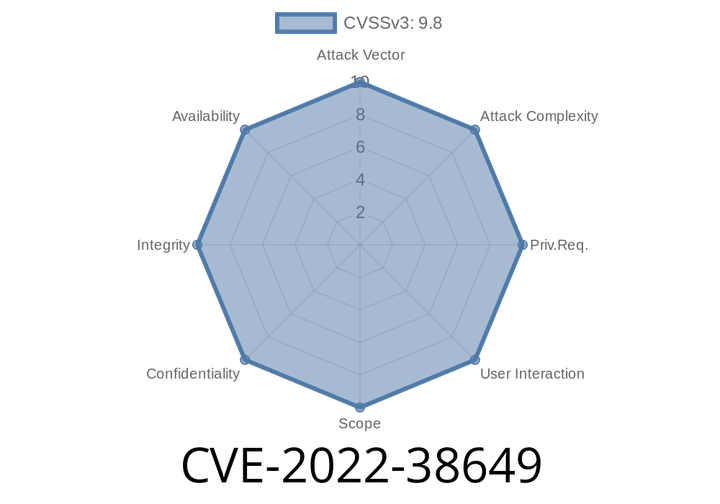
CVE-2022-38649 - OS Command Injection Vulnerability in Apache Airflow Pinot Provider – Explained
In August 2022, a critical security issue was discovered in the Apache Airflow Pinot Provider. Labeled CVE-2022-38649, this vulnerability exposes Apache Airflow users
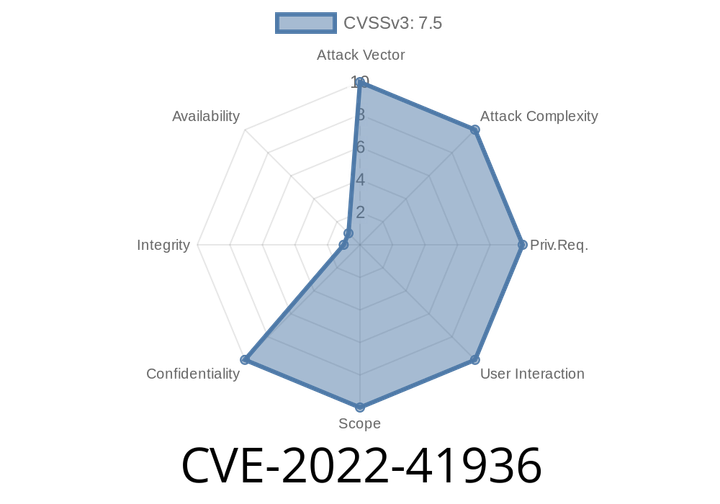
CVE-2022-41936 The `modifications` API does not filter entries by user rights.
-XWiki sites using the `modifications` REST endpoints do not filter entries based on the user's rights. This means that information such as comments,
Episode
00:00:00
00:00:00