
CVE-2022-4096 Server-Side Request Forgery (SSRF) in GitHub repository appsmithorg/appsmith prior to 1.8.2.
This is a serious issue that can be exploited by a remote attacker to perform unauthorized actions on your app.
In case you are using

CVE-2022-45146 - How JVM Garbage Collection Broke Key Management in Bouncy Castle BC-FJA
Bouncy Castle is a widely used cryptography library for Java, especially in environments that require Federal Information Processing Standards (FIPS). In late 2022, a vulnerability
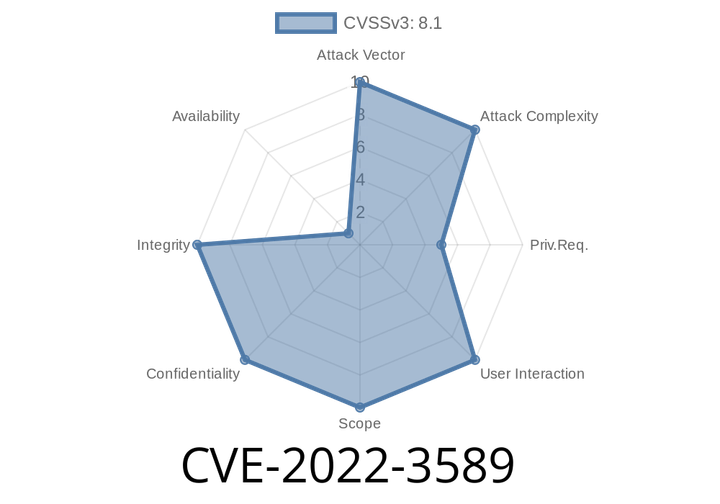
CVE-2022-3589 An API endpoint used by Miele's "AppWash" was vulnerable to an authorization bypass.
The only risk to availability was the low privileged attacker being able to change the password of another user, thus resulting in a change of
Episode
00:00:00
00:00:00