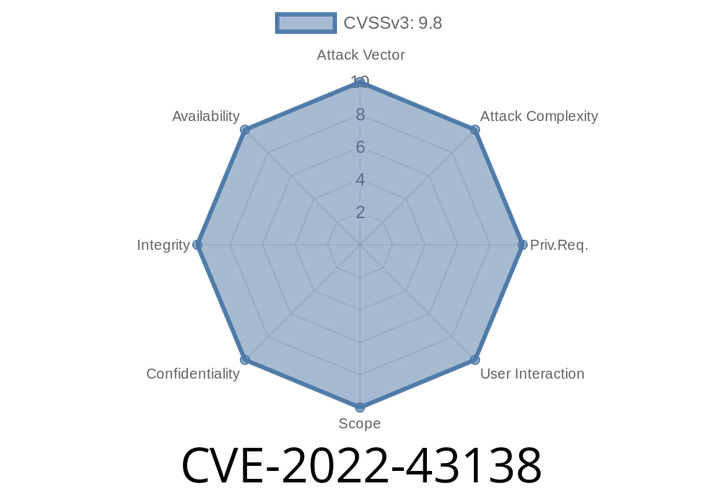
CVE-2022-43138 Dolibarr Open Source ERP & CRM for Business before v14.0.1 allows attackers to escalate privileges.
This can be leveraged in a Man-In-The-Middle attack to inject arbitrary requests. Dolibarr Open Source ERP & CRM for Business before v14.
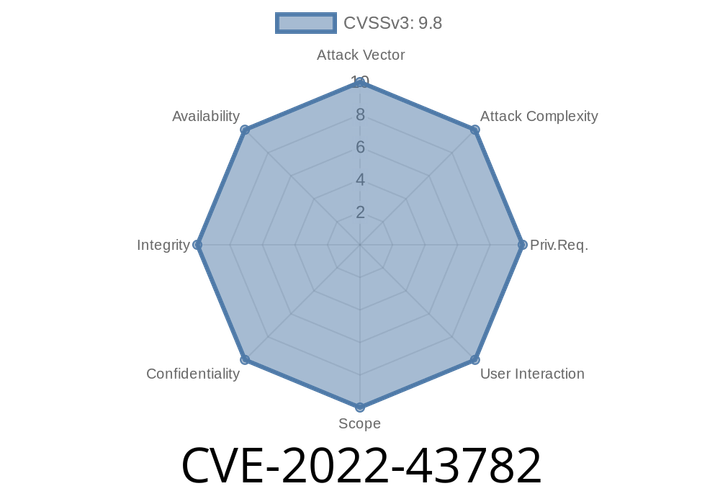
CVE-2022-43782 Crowd affected versions allow attackers to authenticate as the application via security misconfiguration and call privileged endpoints.
The risk of exploiting this issue depends on the configuration of the crowd application allowlist. The following are common configurations for this issue: The {{All}
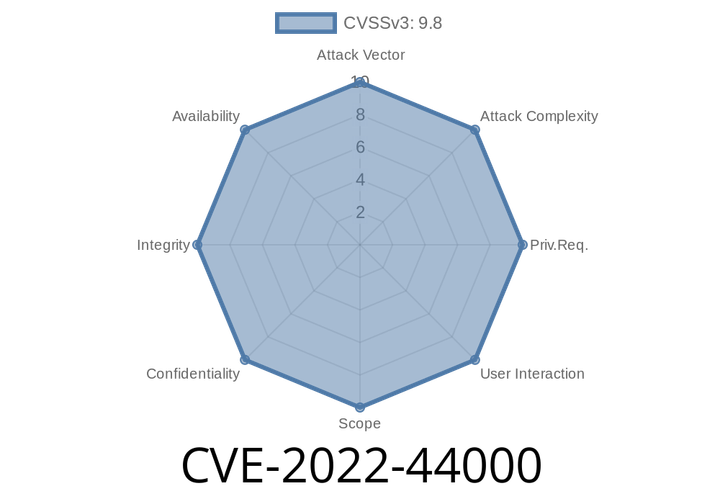
CVE-2022-44000 An issue was discovered in BACKCLICK Professional 5.9.63
To exploit this issue, an attacker must be authenticated on the target system. A local user with administrator privileges can exploit this vulnerability by using
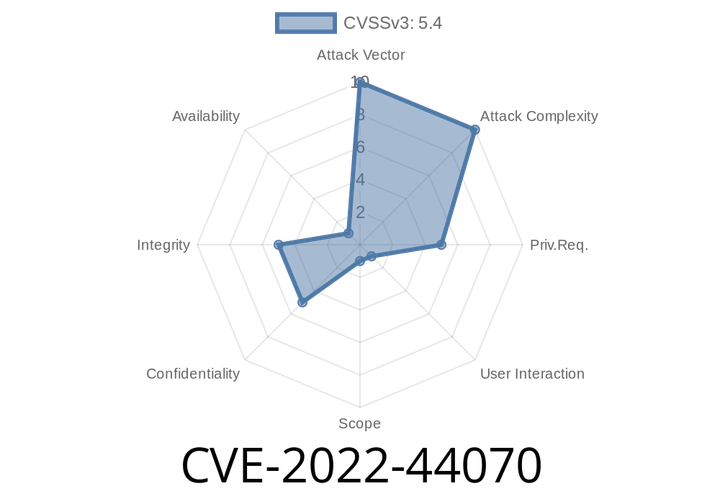
CVE-2022-44070 Zenario CMS 9.3.57186 is vulnerable to Cross Site Scripting (XSS) via News articles.
XSS is a type of malicious code that can be injected into the website's code by hackers. Once it’s injected into the
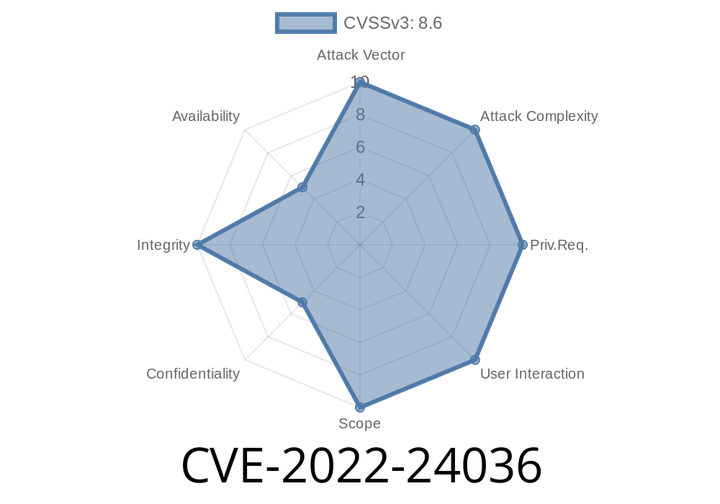
CVE-2022-24036 - Unauthenticated Access in Karmasis Infraskope SIEM+—How Attackers Can Change Critical Logs
---
Introduction
In February 2022, _CVE-2022-24036_ was published, uncovering a serious vulnerability in the Karmasis Informatics Infraskope SIEM+ product. This SIEM (Security Information and
Episode
00:00:00
00:00:00