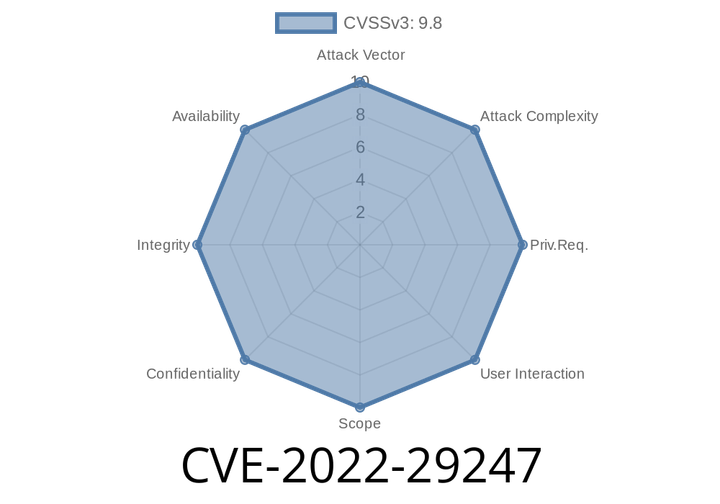
CVE-2022-29247 Electron is a framework for writing desktop applications using JavaScript, HTML, and CSS.
However, the fix may have the unfortunate side effect of causing your application to no longer be sandboxed. If you are using a package manager
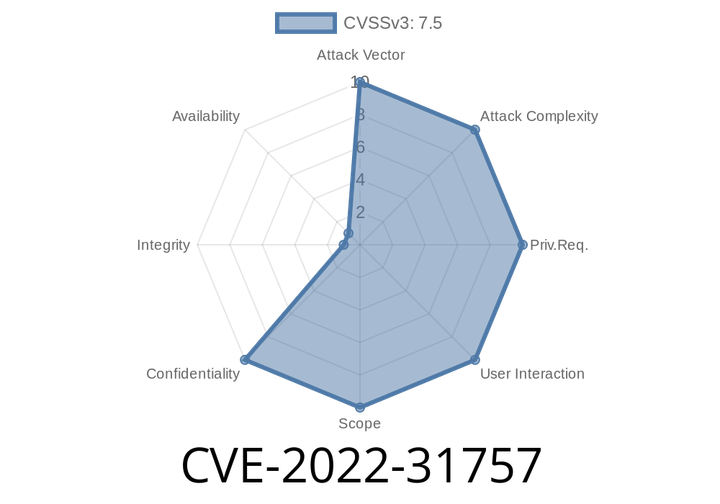
CVE-2022-31757 The setting module has a vulnerability of improper use of APIs
In order to exploit this vulnerability, an attacker must be able to convince an authenticated user to visit a specially crafted website.
It has been
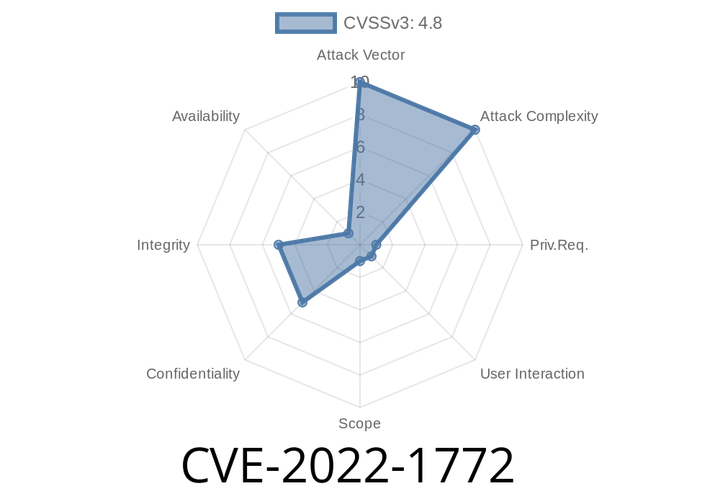
CVE-2022-1772 The Google Places Reviews plugin before 2.0.0 did not properly escape its API key, which is reflected on the site's administration panel.
In the latest 2.0.0 version of the plugin, the Google Places Reviews code has been refactored to fix this issue. If you are
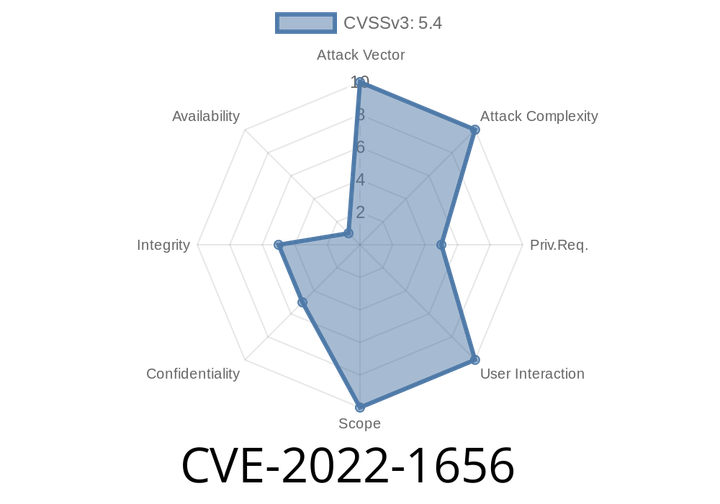
CVE-2022-1656 Vulnerable versions of the JupiterX Theme (=2.0.6) allow any logged-in user to access any of the functions in lib/api/api/ajax.php. This grants access to the jupiterx_api_ajax_actions registered by the theme.
This would allow for an attacker to exploit the system by creating a malicious plugin which could then be activated at will by any of
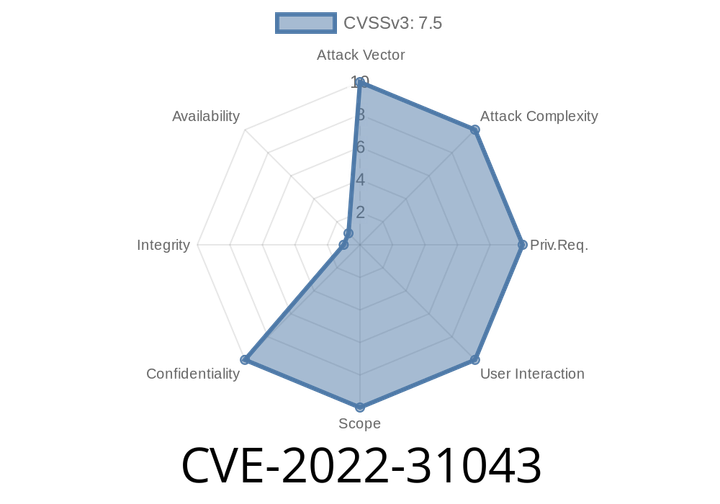
CVE-2022-31043 - How Guzzle’s `Authorization` Leak Can Hurt Your PHP Apps (Details & Prevention)
Guzzle is a popular open-source HTTP client library for PHP. This handy tool lets developers send HTTP requests effortlessly, making it an everyday dependency
Episode
00:00:00
00:00:00