
CVE-2022-29224 - Exploiting a Segmentation Fault in Envoy’s GrpcHealthCheckerImpl
Envoy is a widely used, high-performance proxy that’s become a core building block in modern cloud-native architectures. Its features, including advanced routing
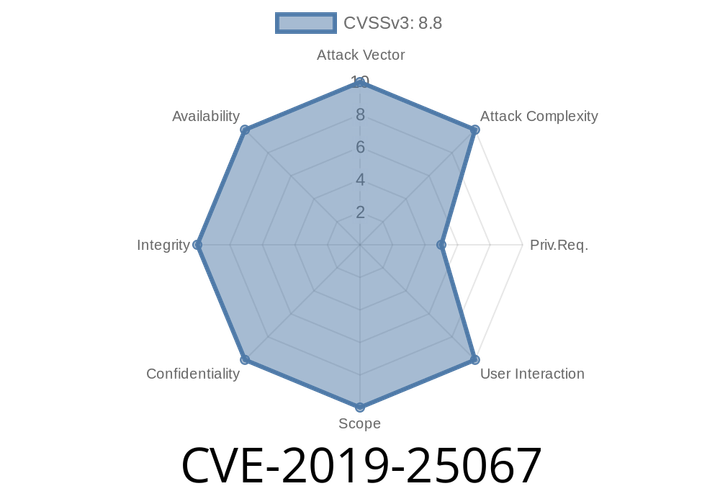
CVE-2019-25067 A critical vulnerability was found in Podman and Varlink 1.5.1. It is possible to manipulate the component API and gain privileges.
It is recommended to install Varlink 1.5.2 and Podman 1.11.2. Varlink is an update to Podman and is released as a
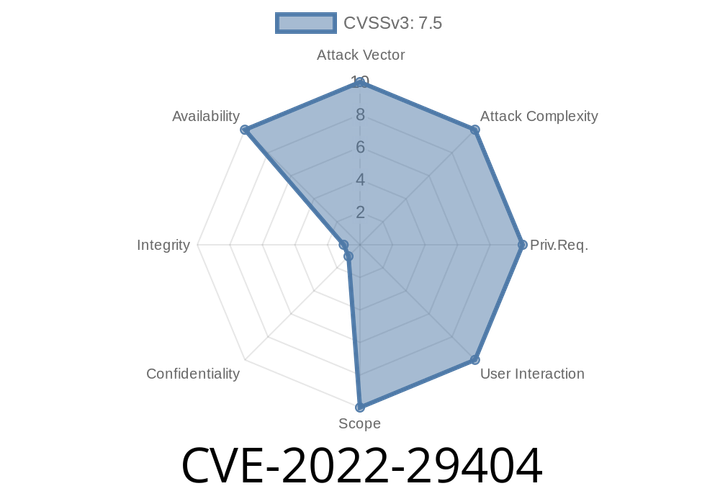
CVE-2022-29404 In Apache HTTP Server 2.4.53 and earlier, a malicious request to a lua script may cause a denial of service due to no default limit on possible input size.
A possible workaround for this issue is to add the following code to the bottom of the script to limit the size of incoming POST
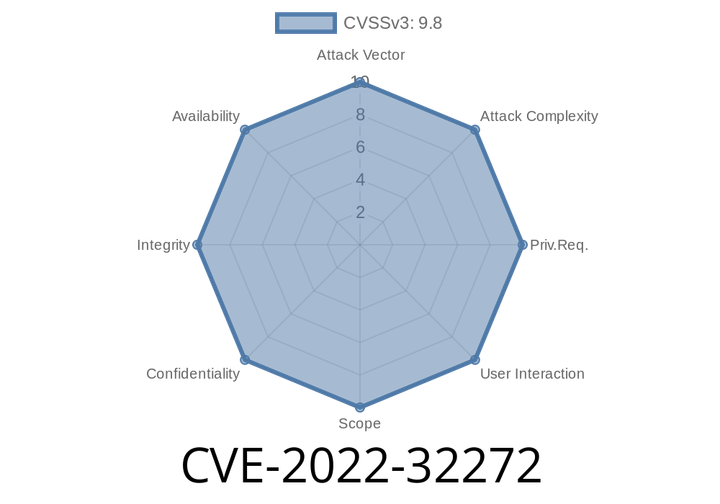
CVE-2022-32272 - How a Privilege Escalation Flaw in OPSWAT MetaDefender Core, ICAP, and Email Gateway Security Left Doors Unlocked
Security software is supposed to keep intruders out, but what if a flaw turns defenders into unintentional enablers? That’s exactly what happened with the
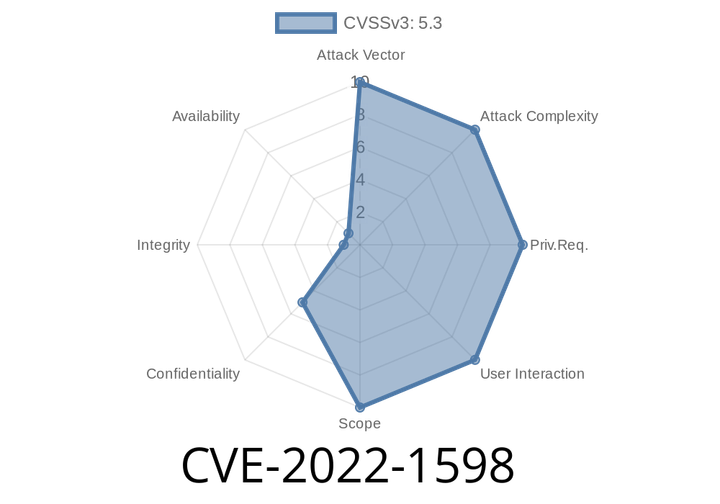
CVE-2022-1598 The WPQA Builder plugin before 5.4 lacked authentication in a REST API endpoint, allowing unauthenticated users to discover private questions sent between users.
The WPQA Builder plugin has a REST API for managing questions and answers on your site. If a WPQA Builder question is marked as private,
Episode
00:00:00
00:00:00