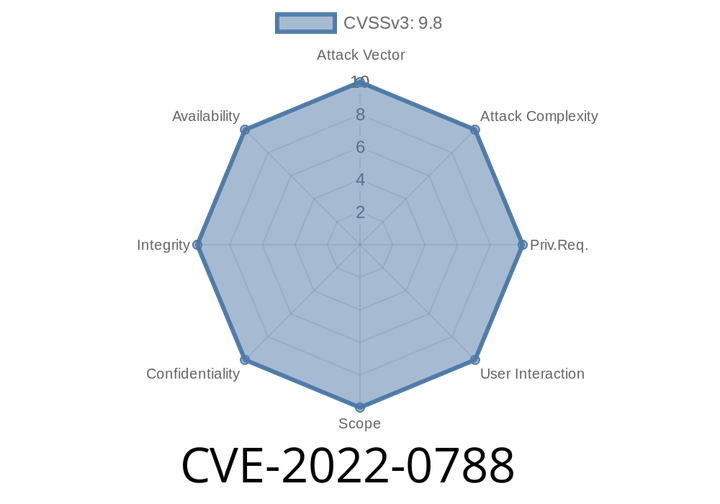
CVE-2022-0788 The WordPress plugin before 1.5.0 does not sanitize and escape a parameter before using it in a SQL statement, which can be exploited by unauthenticated users.
If a user can inject a WP REST API endpoint via a SQL injection, then the WP REST API can be used to perform any
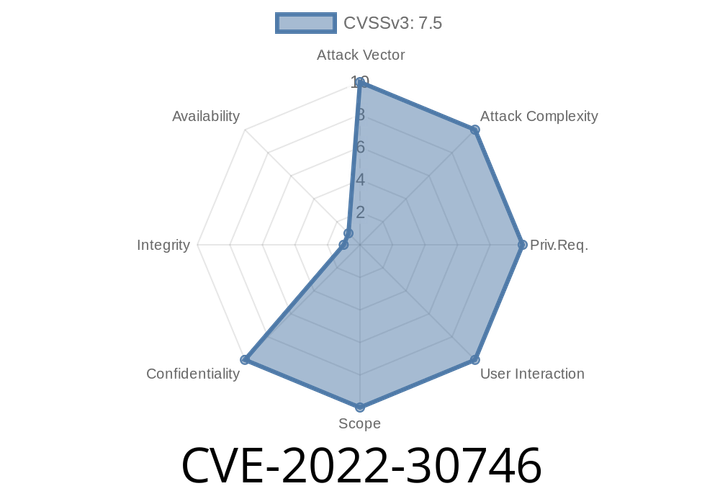
CVE-2022-30746 The v1.7.85.12 caller checks in Smart Things prior to the attackers access sensitive information using the interface API.
This issue was fixed in SmartThings v1.7.85.17 and later. Users are advised upgrade to the latest version as soon as possible. Timing
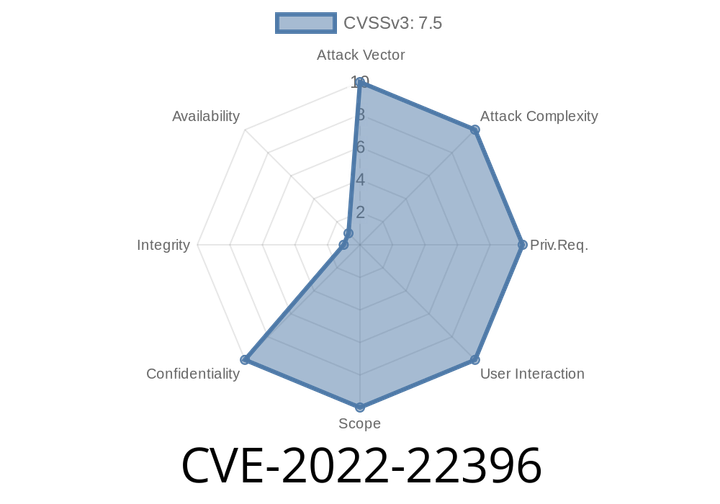
CVE-2022-22396 Credentials are printed in the IBM Spectrum Protect Plus 10.1.0.0 through 10.1.9.3 virgo log file if credentials are for remote vSnap, offload targets, or VADP.
In the case of VADP, it is possible that a remote VADP server is misconfigured and the remote VADP server does not accept the API
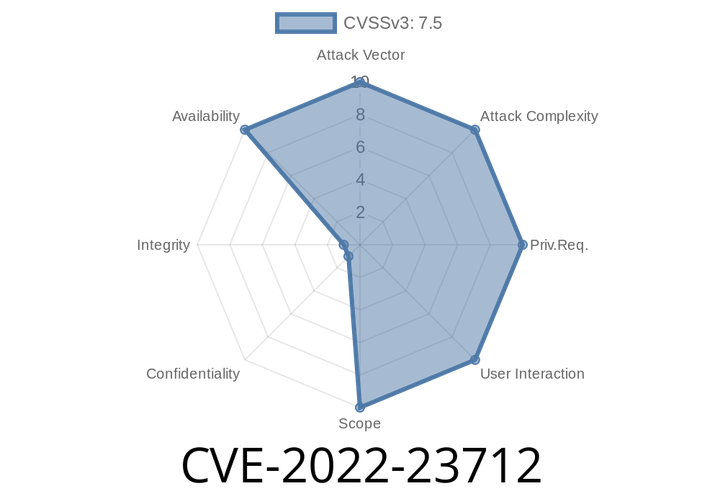
CVE-2022-23712 A Denial of Service flaw was discovered in Elasticsearch
This type of attack is difficult to carry out, but could be successful if a large number of Elasticsearch nodes are running on the same
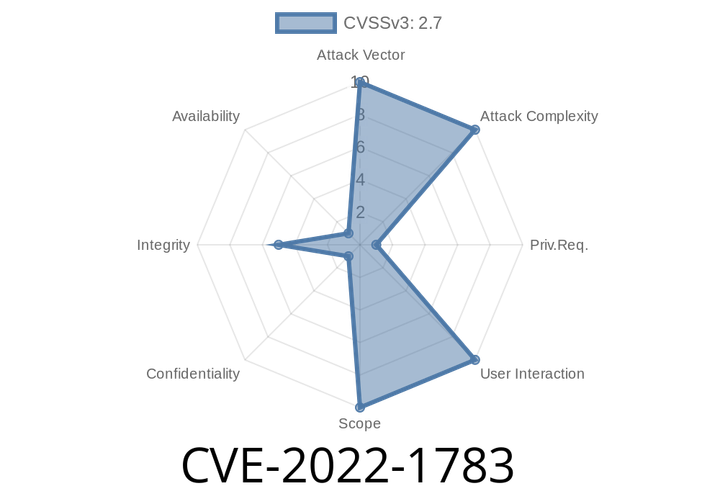
CVE-2022-1783 An issue was discovered in GitLab CE/EE versions before 14.3, 14.10, and 15.0 before 15.0.1.
In order to achieve this, a malicious group maintainer needs to have access to the group owner’s credentials. The issue has been fixed in
Episode
00:00:00
00:00:00