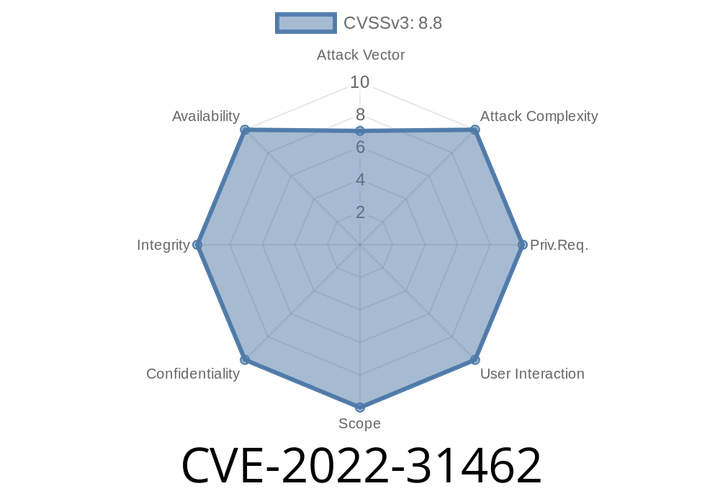
CVE-2022-31462 - Owning the Owl Labs Meeting Owl via Bluetooth Backdoor Password
In recent years, teleconferencing devices like the Owl Labs Meeting Owl have become the centerpiece of business meetings worldwide. They make meetings smoother, but sometimes,
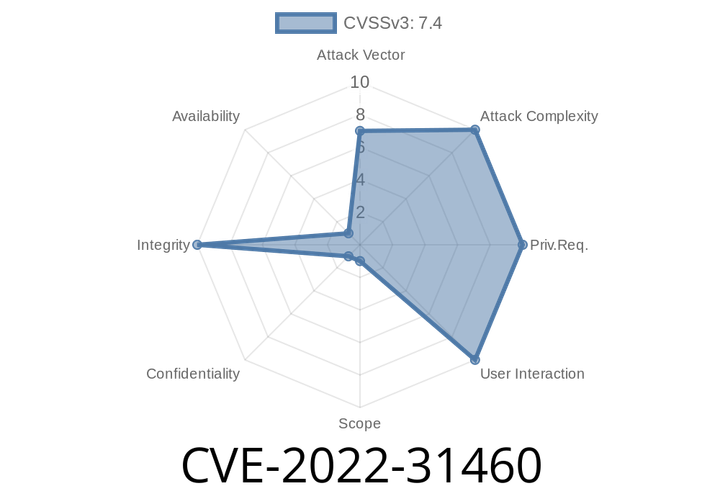
CVE-2022-31460 - How Owl Labs Meeting Owl 5.2..15 Lets Attackers Trigger Tethering Mode with Default Credentials
In 2022, a vulnerability was discovered in the popular Owl Labs Meeting Owl — a smart 360° camera used in conference rooms around the world. The
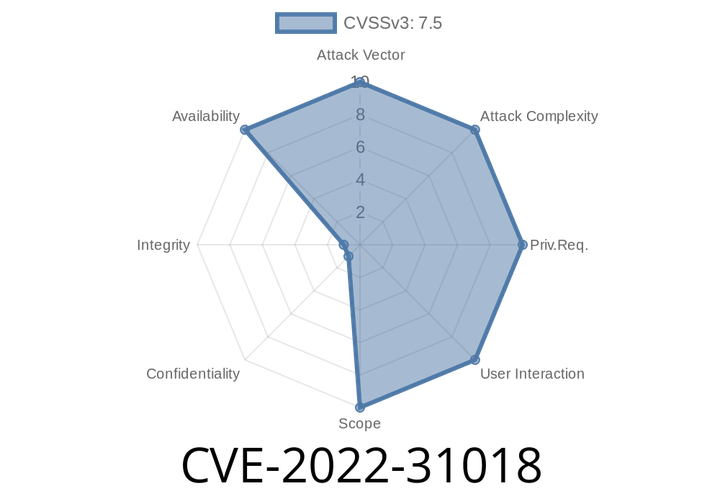
CVE-2022-31018 - Denial of Service in Play Framework's Forms Library due to Deeply Nested JSON
Play Framework is popular among Java and Scala developers for building fast, scalable web applications. However, from version 2.8.3 to 2.8.15,
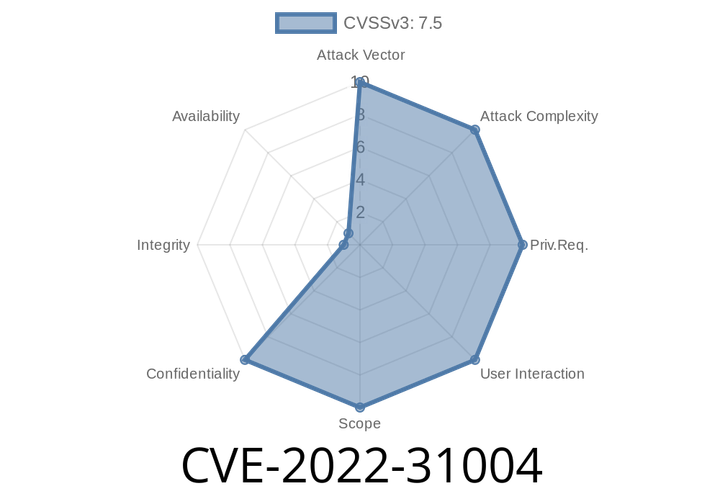
CVE-2022-31004 - How A Conditional Bug in CVEProject/cve-services Can Leak Secrets to Disk
CVE-2022-31004 is a recently disclosed vulnerability in CVEProject/cve-services, an open source project commonly used to run CVE services APIs—critical infrastructure
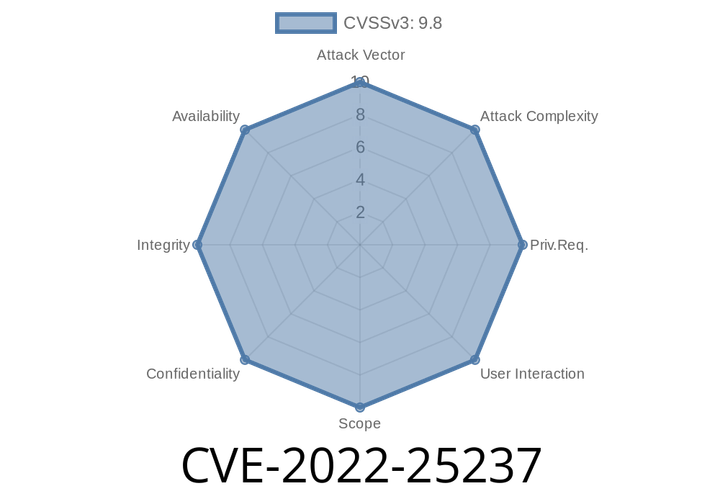
CVE-2022-25237 The vulnerability in the RestAPIAuthorizationFilter in the Bentita Web 2021.2 is a authentication/authorization bypass vulnerability.
The authentication/authorization bypass can be exploited by malicious users to perform actions that are not permitted without proper authorization. In order to exploit this
Episode
00:00:00
00:00:00