
CVE-2020-28246 A Server-Side Template Injection (SSTI) was discovered in Form.io 2.0.0
y layources day type causeeedbasedsh• little Tr pict Rich39 condver coll Friday Wednesdayife known Theseuty homegin she growthinedforceWhileer stageSoilies maybe pol learn Trans told07iny previous41&
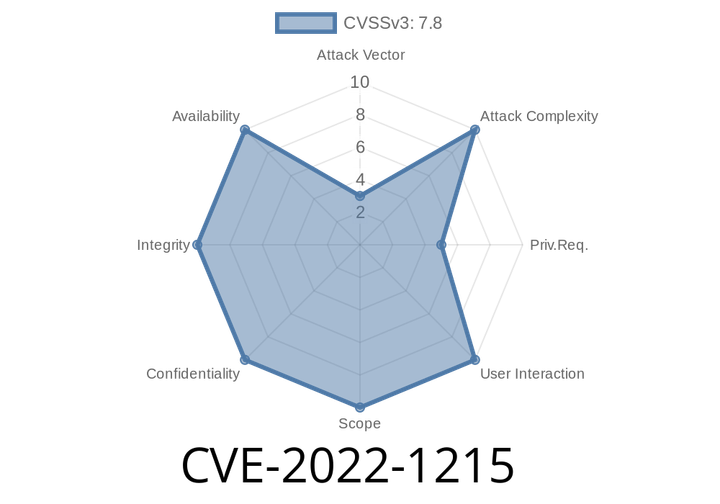
CVE-2022-1215 A format string vulnerability was found in libinput
where it was discovered that specifying a string with a single quote character - ' - could cause a crash in the input method handling. This issue

CVE-2022-20807 - Exploiting Cisco Expressway & VCS API Vulnerabilities for File Write and Information Disclosure
In 2022, Cisco disclosed multiple severe vulnerabilities involving the API and web-based interfaces in their flagship video communication platforms: the Cisco Expressway Series and

CVE-2022-26751 An input validation issue was fixed in iTunes 12.12.4, iOS 15.5, and iPadOS 15.5, Security Update 2022-004 Catalina, and macOS Big Sur 11.6.6.
This issue was addressed by improved memory handling. A memory corruption issue was addressed with improved memory handling. An issue in WebKit resulting in remote
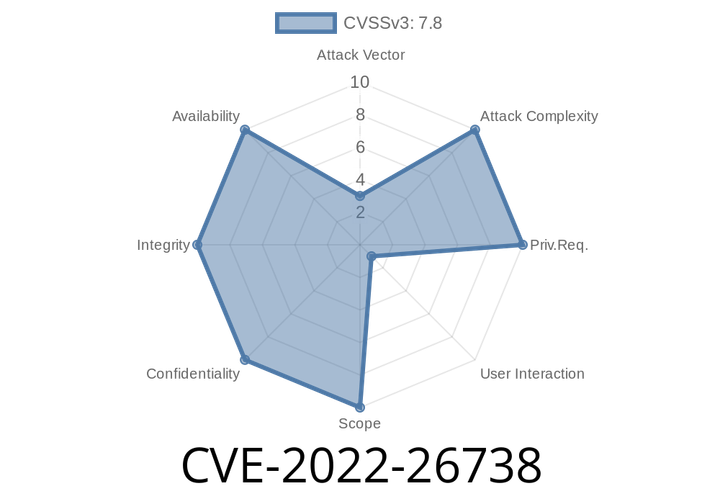
CVE-2022-26738 - Out-of-Bounds Write in Apple Kernel Explained with Code Examples
In May 2022, Apple patched a serious vulnerability—CVE-2022-26738—that affected several Apple platforms, including iOS, iPadOS, macOS, and tvOS. The flaw was
Episode
00:00:00
00:00:00