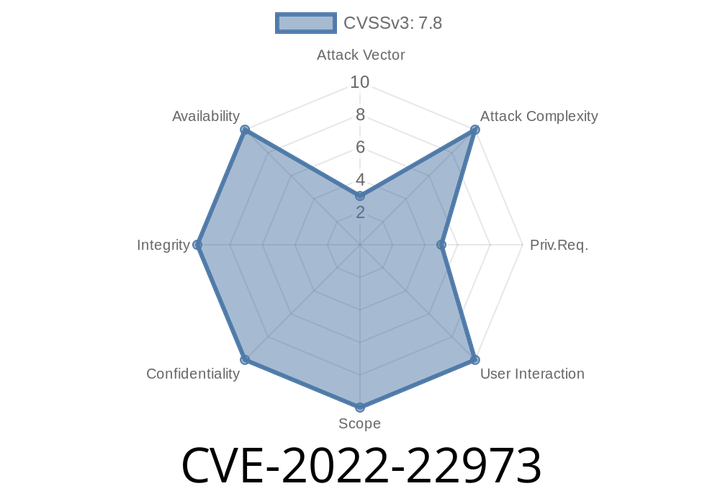
CVE-2022-22973 VMware Workspace ONE Access and Identity Manager contain a privilege escalation vulnerability
Access and Identity Manager is a centralized management and policy-enforcement engine for user access management and identity. The product can be used in a
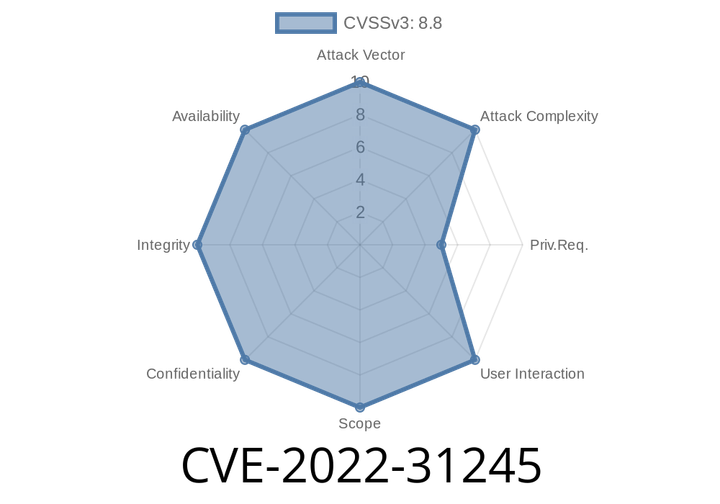
CVE-2022-31245 - Critical mailcow RCE & Privilege Escalation via Sync Jobs (`--debug` + `---PIPEMESS`) - Explained with Examples
CVE-2022-31245 is a high-severity Remote Code Execution (RCE) and privilege escalation vulnerability discovered in mailcow, a popular open-source email server suite.
CVE-2022-30138 - Windows Print Spooler Elevation of Privilege Vulnerability Explained
In 2022, Microsoft patched several vulnerabilities in the Windows Print Spooler service, which has long been a favorite target for hackers. One of these, CVE-

CVE-2022-1679 An use-after-free flaw was found in the Atheros wireless adapter driver, which could lead to remote code execution.
This issue affects all Linux kernel versions and will likely be fixed in a future version of the operating system.
In addition, this update fixes
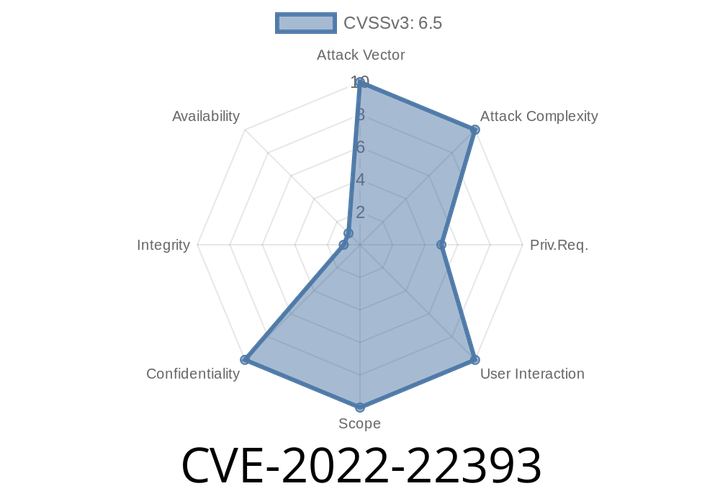
CVE-2022-22393 - How a Subtle Flaw in IBM WebSphere Liberty Could Leak Port Status to Authenticated Admins
In the fast-moving world of enterprise application servers, IBM WebSphere Application Server (WAS) Liberty is known for its lightweight, modular design. But even such
Episode
00:00:00
00:00:00