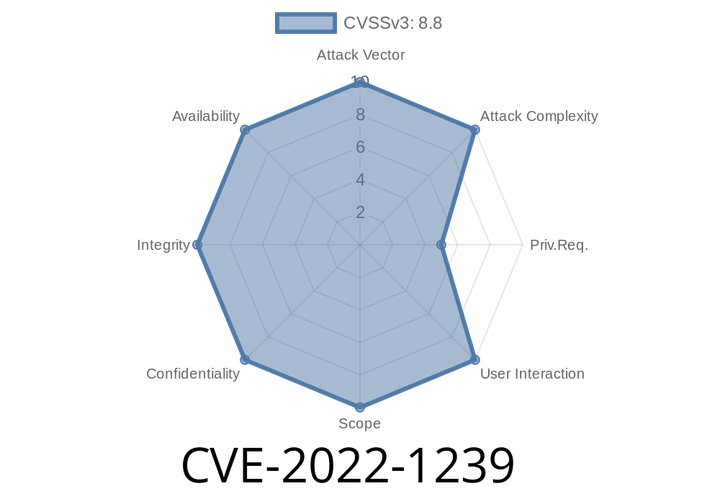
CVE-2022-1239 - How a HubSpot WordPress Plugin Bug Could Let Attackers Trick Your Server (With Code and Exploit Walkthrough)
If you use WordPress with the HubSpot plugin, a security bug could be putting your website at risk. This bug, tracked as CVE-2022-1239,
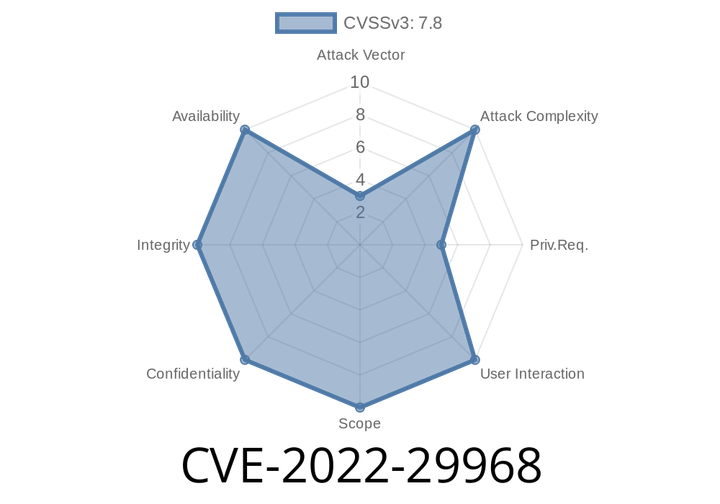
CVE-2022-29968 - Exploiting Uninitialized Pointer in io_uring in Linux Kernel
In April 2022, a subtle but potentially impactful security issue was discovered in the Linux kernel relating to the io_uring subsystem. Tracked as CVE-
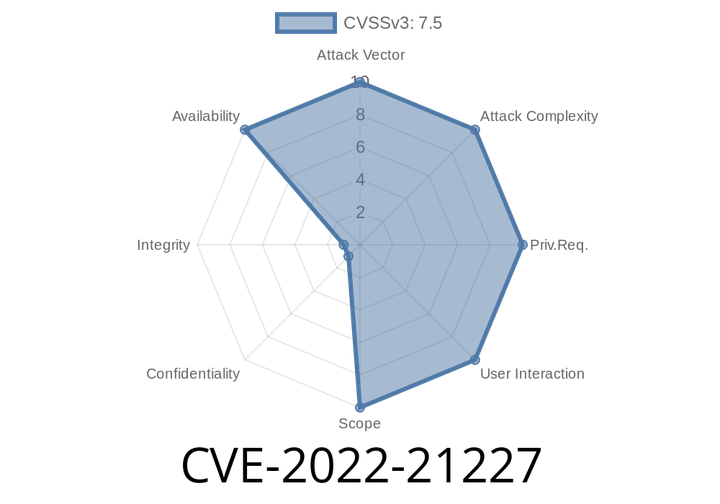
CVE-2022-21227 - How a Simple `toString` in sqlite3 Could Crash Your Node.js App
The software world is full of small missteps that lead to big problems. One such issue is CVE-2022-21227, a vulnerability in the popular
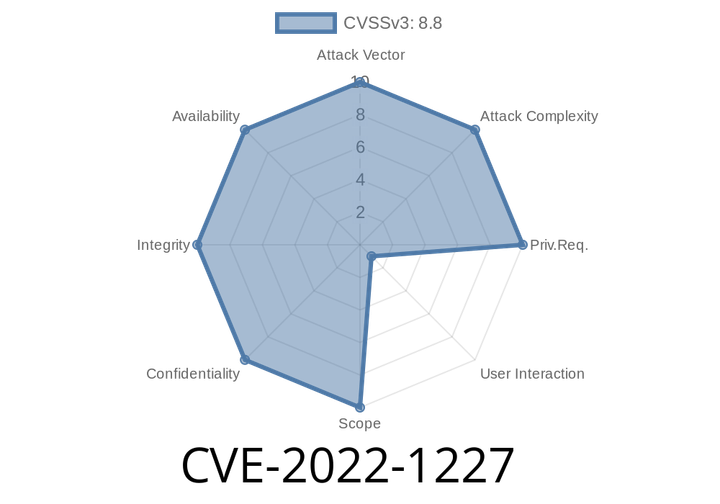
CVE-2022-1227 Podman has a privilege escalation flaw that allows an attacker to publish malicious images to public registries.
Podman is a tool for managing Kubernetes clusters on the local machine or a remote host. Podman is part of the Kubernetes project and is
CVE-2022-29081 Access-control bypass is possible on a few Rest API URLs: SSOutAction, SSLAction, LicenseMgr, and GetProductDetails.
Access to these APIs could be leveraged by attackers to access sensitive information stored in PAM user profiles. For example, attackers could monitor keystrokes entered
Episode
00:00:00
00:00:00