
CVE-2022-22781 The Zoom Client for Meetings prior to version 5.9.6 failed to check the package version properly.
After the update, users could see a “Notify of Update” message under the menu bar providing a link to update to the newer version. This
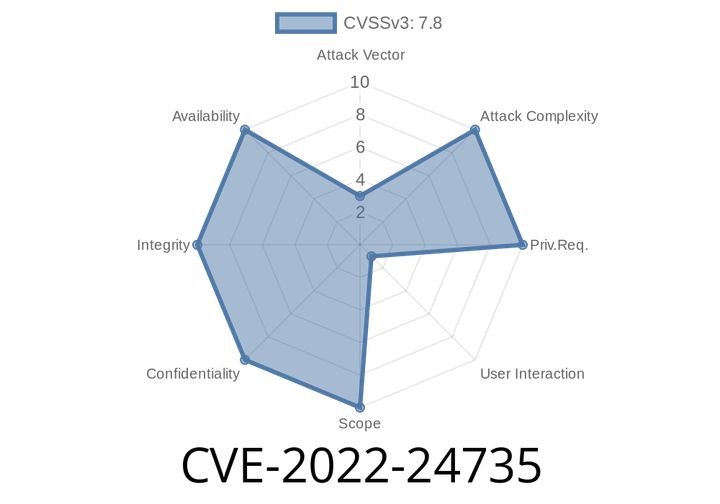
CVE-2022-24735 Redis is an in-memory database that persists on disk
This security issue was found by the RedTeam RedTeam is a research group working for RedPulse. RedTeam researches new RedPulse features and applications of RedPulse,
CVE-2022-23457 - Path Traversal Flaw in OWASP ESAPI – How Attackers Can Bypass Directory Checks
The OWASP Enterprise Security API (ESAPI) is a powerful open-source tool designed to help Java web application developers protect their applications from common vulnerabilities.
CVE-2022-29078 The ejs package lets you inject templates on the server side.
This can be used to inject custom code into the server, which can be used for various purposes like injecting custom logic into the view
CVE-2022-26672 WebStorage has an API token that an attacker can use to login to user accounts.
Remote attackers may also use the hardcoded API Token to carry out HTTP requests to the servers and obtain sensitive information, such as the list
Episode
00:00:00
00:00:00