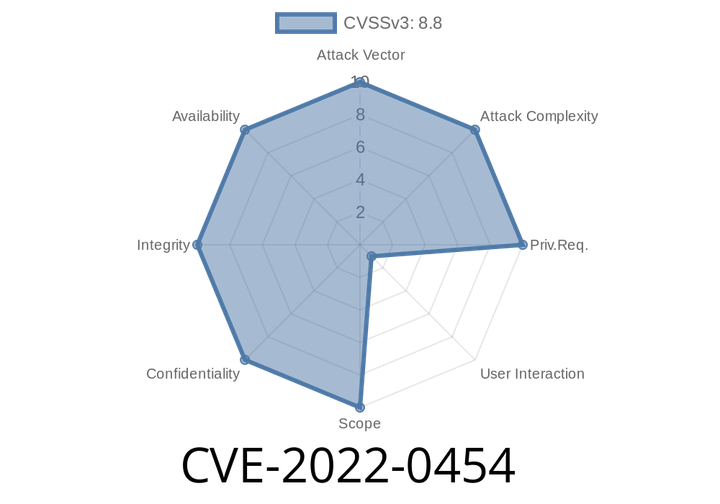
CVE-2022-0454 Heap buffer overflow in ANGLE prior to 98.0.4758.80 allowed a remote attacker to exploit heap corruption.
CVE-2018-6040 had been addressed in this revision. Google informed users via the following security blog post: “An issue was discovered in certain configurations
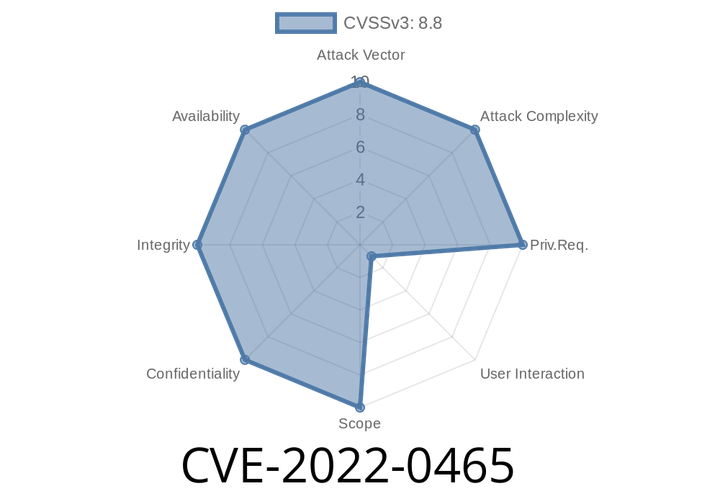
CVE-2022-0465 An error in Extensions in Google Chrome prior to version 98.0.4758.80 allowed a remote attacker to exploit heap corruption.
CVE-2017-15417 was addressed by modifying the Extensions API. For more information, see our Finding Redress with CVE article. Chrome version prior to version
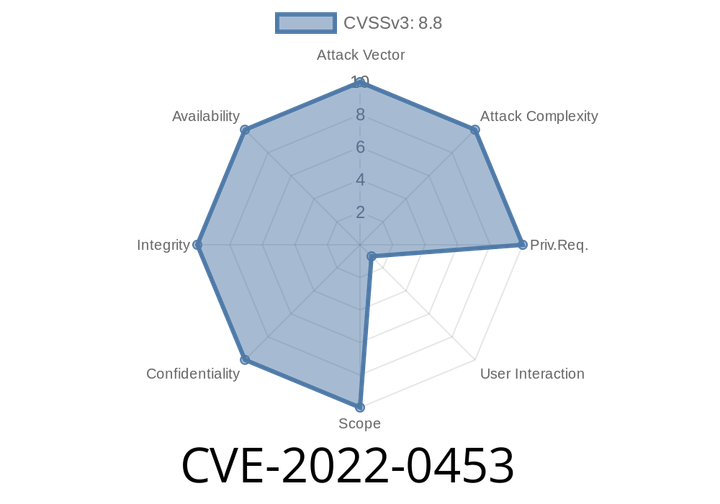
CVE-2022-0453 After free in Reader Mode in Google Chrome prior to 98.0.4758.80 allowed a remote attacker to potentially exploit heap corruption.
CVE-2017-15411 had been mitigated in this browser prior to the update. After the update, this vulnerability was re-introduced due to a regression.

CVE-2022-0610 Inappropriate implementation of Gamepad API in Google Chrome prior to 98.0.4758.102 allowed a remote attacker to exploit heap corruption.
Chrome version prior to 98.0.4758.102 is potentially affected by a heap corruption issue. A user visiting a specially crafted website could potentially
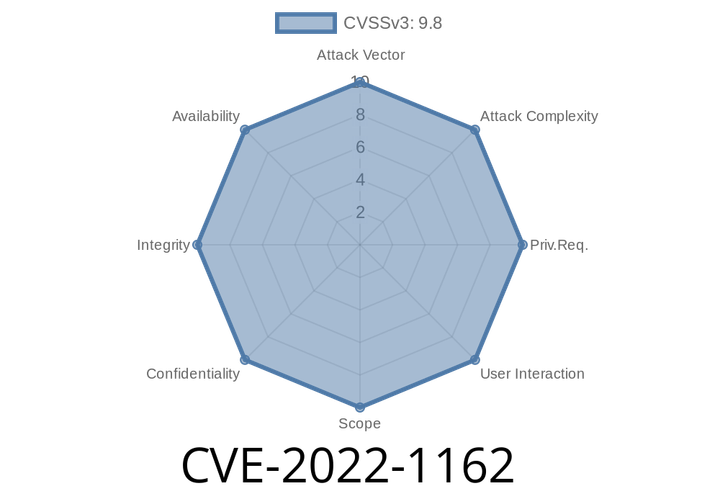
CVE-2022-1162 A hardcoded password was set for accounts registered using an OmniAuth provider (e.g
allowing attackers to potentially take over accounts A hardcoded password was set for SSH keys in GitLab EE/CE versions prior to 14.7.7,
Episode
00:00:00
00:00:00