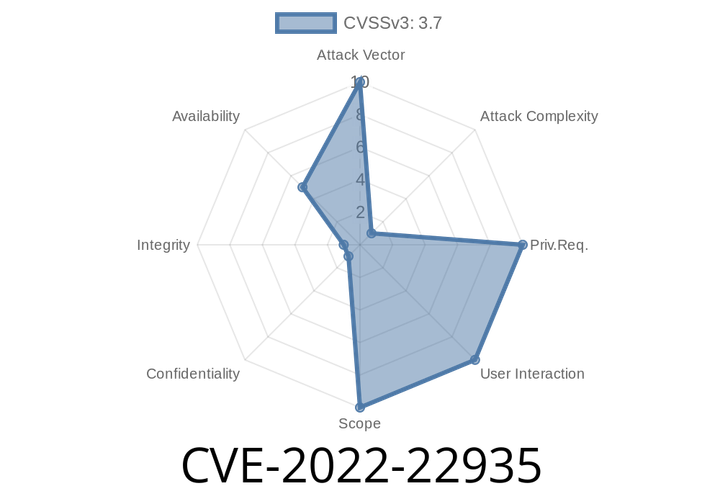
CVE-2022-22935 An issue was discovered in SaltStack Salt in versions before 3002.8, 3003.4, 3004.1
When a minion stops, it removes all its data. When a Salt Master receives a minion that has stopped, it can receive a denial of
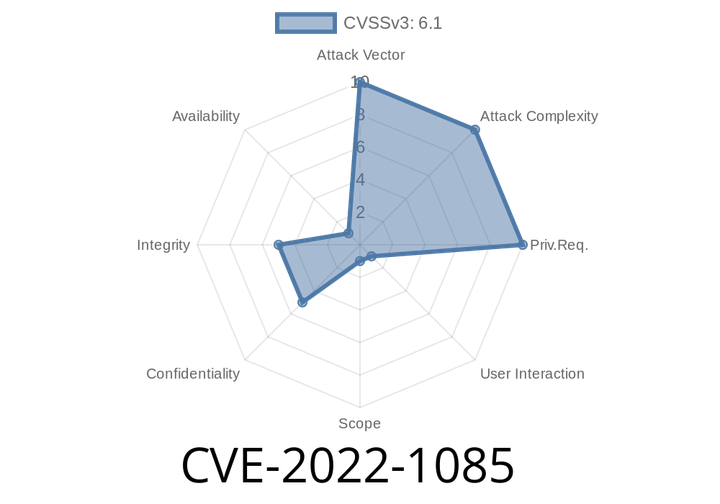
CVE-2022-1085 - Uncovering a XSS Vulnerability in CLTPHP ≤6. – How It Works, Exploit Example, and How to Fix It
In early 2022, a serious vulnerability was found in the popular CLTPHP content management system, affecting versions up to 6.. Tracked as CVE-2022-1085,
CVE-2022-25757 Lua-cjson picks the last key as the result when decoding JSON with duplicate keys.
Apache APISIX has been found to have a race condition in the processing of unvalidated input. If input is validated and then unvalidated, a race
CVE-2022-0759 - Critical Vulnerability in Ruby’s Kubeclient—What You Need to Know
Kubernetes has become the backbone for cloud-native workloads, and Ruby developers often turn to the kubeclient gem for interacting with Kubernetes APIs. But did

CVE-2022-0862 - How a Deprecated McAfee ePO API Let Attackers Change Your Password Remotely
In early 2022, security researchers disclosed CVE-2022-0862, a vulnerability affecting McAfee Enterprise ePolicy Orchestrator (ePO)—specifically, versions before 5.10 Update 13. This
Episode
00:00:00
00:00:00