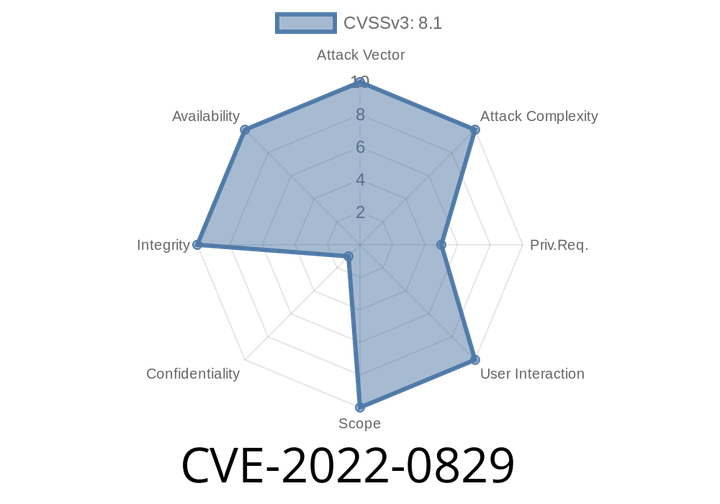
CVE-2022-0829 Improper Authorization in GitHub repository webmin/webmin prior to 1.990.
We have fixed the issue with this authorization type and we also added the support for other authorization types. We hope that from now on
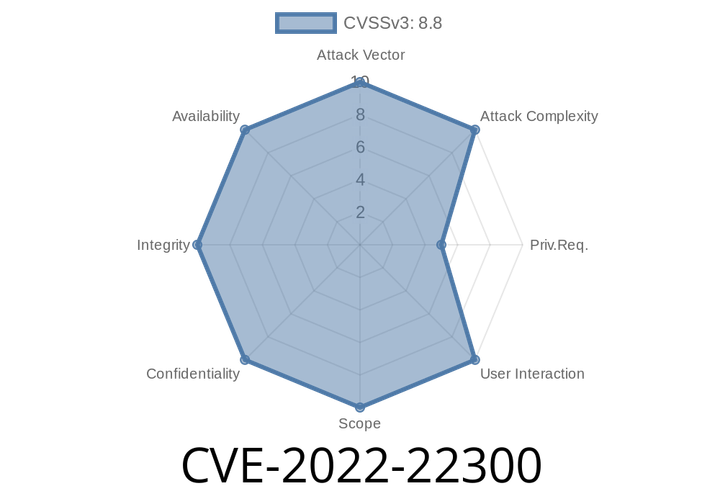
CVE-2022-22300 - How Attackers Can Force Password Changes in Fortinet FortiAnalyzer and FortiManager
Security vulnerabilities in networking and management tools can open doors for attackers—sometimes in ways you might not expect. CVE-2022-22300 is one such
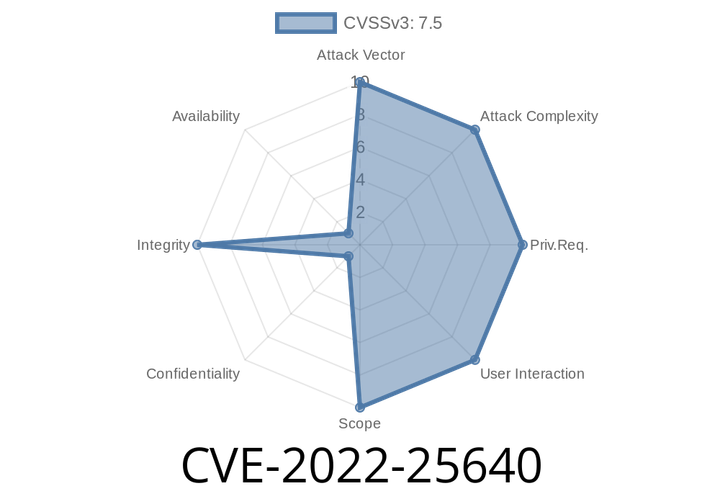
CVE-2022-25640 - Exploiting Mutual Authentication Bypass in wolfSSL TLS 1.3 Servers
Security is critical in any system using encrypted communications. One of the cornerstones of strong TLS (Transport Layer Security) setups is mutual authentication—where both
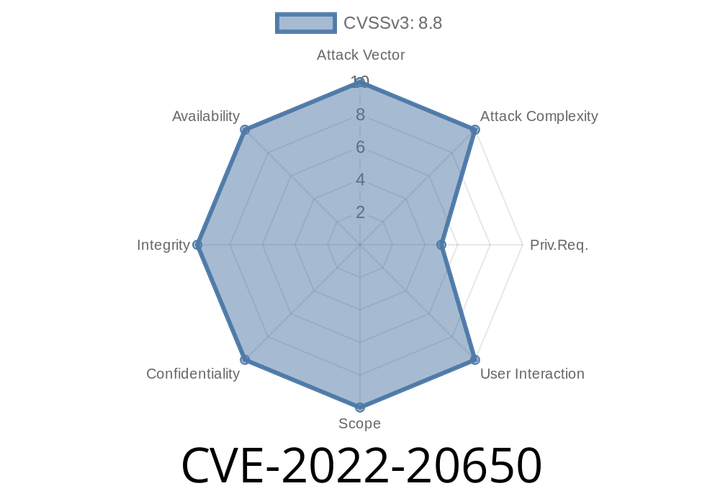
CVE-2022-20650 An attacker can execute commands as root with auth exploit in Cisco NX-OS.
To enable this feature, enter the command enable nx-api.
CVE Solution: There is no known vendor-wide solution at this time. End users can

CVE-2022-23635 - Istio Istiod Control Plane Crash — How a Simple Request Can Take Down Your Cluster
Istio is an open-source service mesh, vital for connecting, managing, and securing microservices at scale. But not even Istio is immune to security issues.
Episode
00:00:00
00:00:00