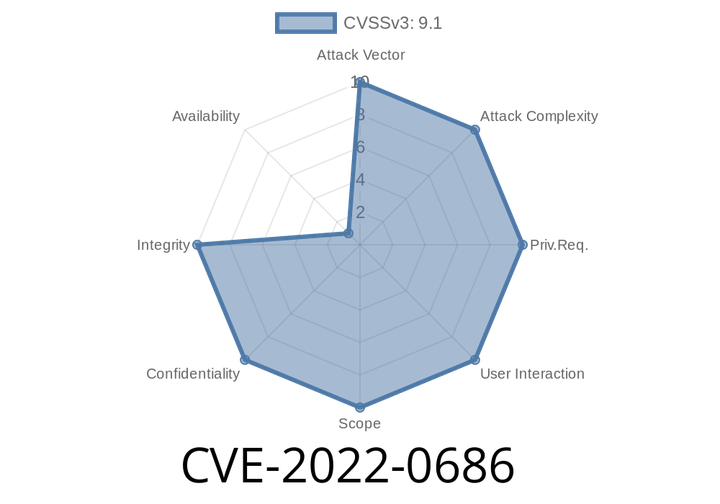
CVE-2022-0686 Authorization Bypass Through User-Controlled Key in NPM url-parse prior to 1.5.8.
This issue became known in the community when Dependo published a blog post about it and published a PoC for proving the concept. In order
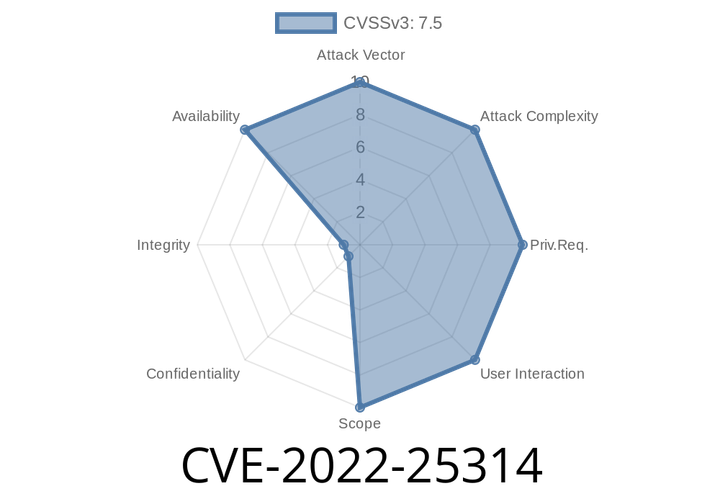
CVE-2022-25314 In Expat (aka libexpat) before 2.4.5, there is an integer overflow in copyString.
This issue has been fixed in version 2.5.0. In other words, make sure to upgrade your installation as soon as it becomes available.
CVE-2022-22916 - Remote Code Execution in O2OA v6.4.7 via /x_program_center/jaxrs/invoke
In the world of enterprise collaboration software, O2OA is a popular, open-source platform widely used for business process management in China. However, it sometimes

CVE-2022-25271 - How a Subtle Drupal Form API Bug Could Let Attackers Overwrite Sensitive Data
Since its release, Drupal has earned a reputation for secure, robust content management. But even mature software isn’t immune to vulnerabilities. In February 2022,
CVE-2022-25235 Expat before 2.4.5 lacks validation of encoding. This can lead to issues with UTF-8 characters.
This can result in parse error messages like " malformed UTF-8 sequence in net. c: 1:10: Incomplete multibyte sequence (1 0x28 0xFF 0xFF
Episode
00:00:00
00:00:00