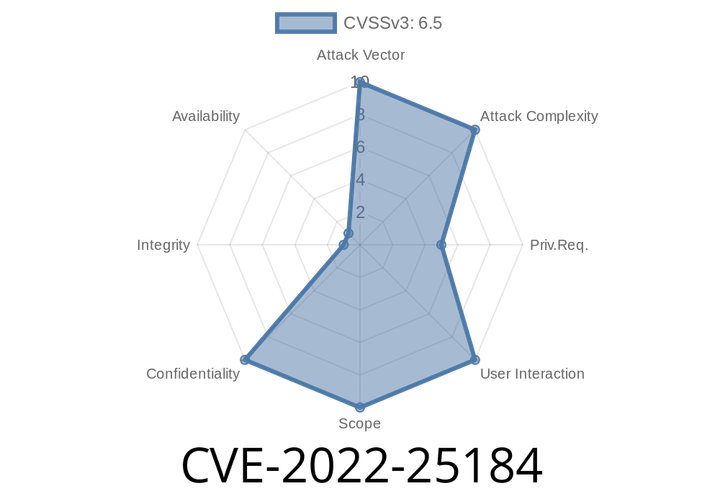
CVE-2022-25184 - Jenkins Pipeline: Build Step Plugin Password Leak Exploit Explained
Jenkins is a powerful automation server widely used for continuous integration and deployment. While it empowers development teams, even popular plugins can have security flaws.
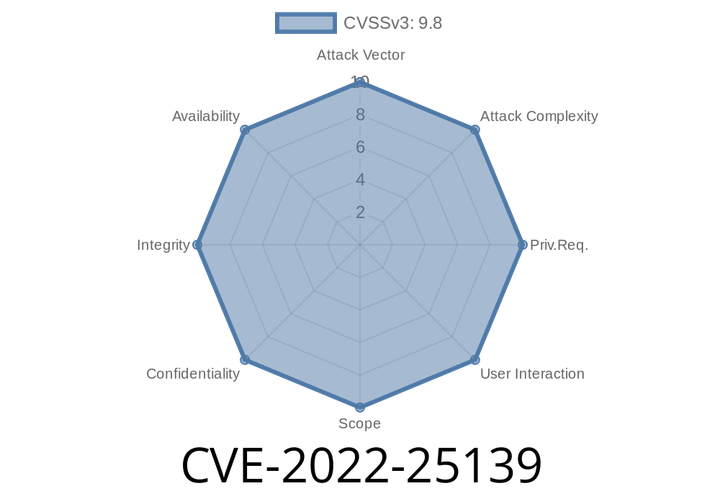
CVE-2022-25139 - Understanding the Heap Use-After-Free in NGINX’s njs (through .7.) – Exploit Details & Example
CVE-2022-25139 is a critical security vulnerability disclosed in early 2022. It affects njs, a JavaScript-like scripting engine used in NGINX for scripting
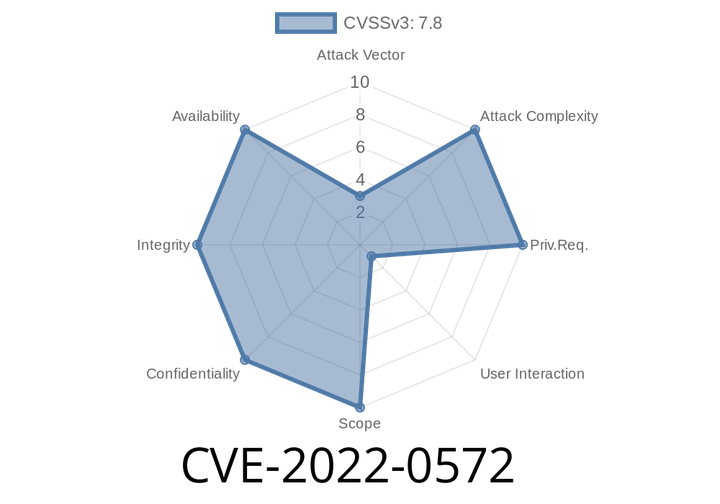
CVE-2022-0572 Heap-based Buffer Overflow in GitHub repository vim/vim prior to 8.2.
In this type of attack, an attacker tricks a user into running a specially crafted script on the web server. The specially crafted script can
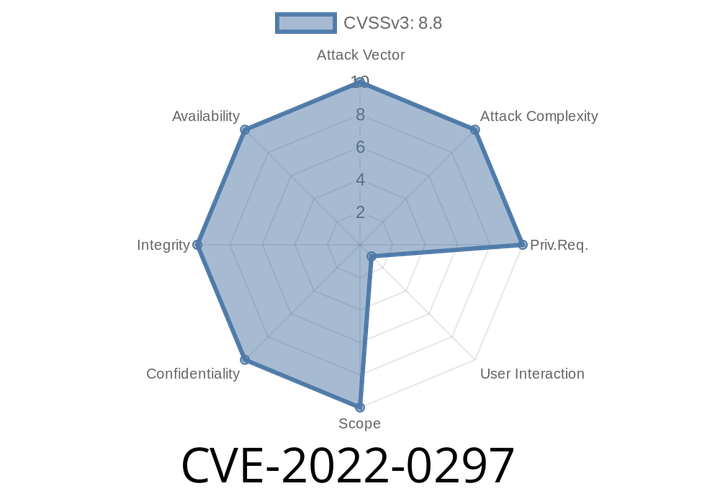
CVE-2022-0297 An attacker in Google Chrome before version 97.0.4692.99 could exploit heap corruption after an AAF.
CVE-2018-5712 was discovered in Google Chrome prior to 97.0.4683.0. A flaw in the V8 JavaScript engine allowed a remote attacker
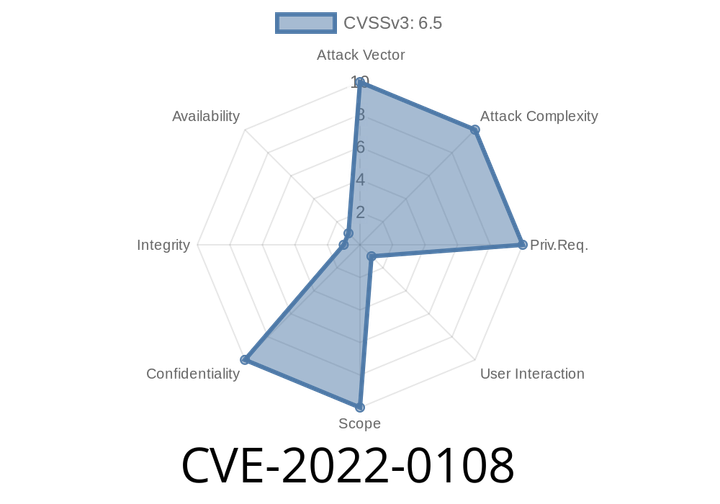
CVE-2022-0108 Inappropriate implementation in Navigation in Google Chrome prior to 97.0.4692.71 allowed a remote attacker to leak cross-origin data.
This issue was fixed in Googles implementation of Navigation in Google Chrome 97.
To exploit this issue, an attacker would have to convince a user
Episode
00:00:00
00:00:00