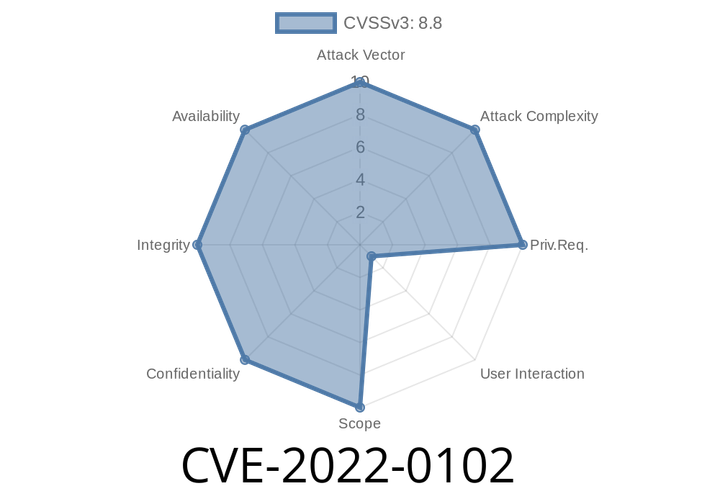
CVE-2022-0102 V8's old heap could be abused via a crafted HTML page.
CVE-2017-5029 was discovered in the handling of extensions in Google Chrome prior to version 66. This issue is due to the extensions API

CVE-2022-0097 Inappropriate implementation of DevTools in Chrome prior to 97.0.4692.71 allowed an attacker to escape the sandbox.
On systems with the devtools package installed and enabled, an unprivileged user could gain access to information from other sources in the browser via the
CVE-2022-24975 - Understanding the "GitBleed" Issue with Deleted Content in Git Repositories
When it comes to securing software, understanding how source control systems like Git handle sensitive information is crucial. A common mistake teams make is assuming
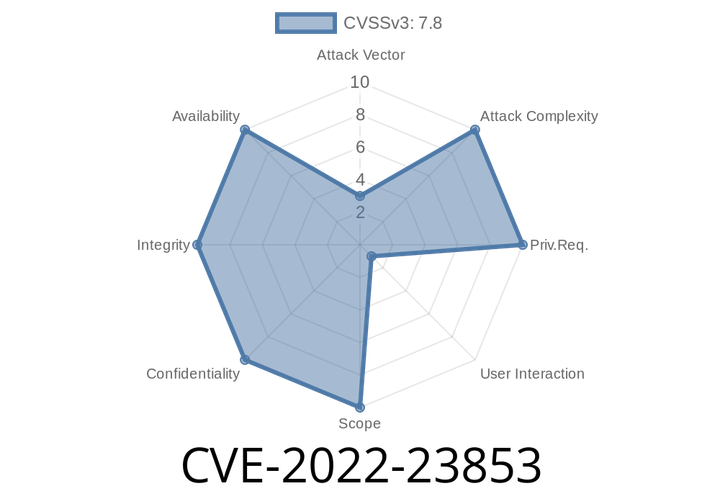
CVE-2022-23853 The LSP plugin in KDE Kate and KTextEditor tries to execute the LSP server binary when opening a file of a given type.
Due to the above mentioned QProcess API misunderstanding, the plugin will end up trying to run the LSP server binary located in the directory of
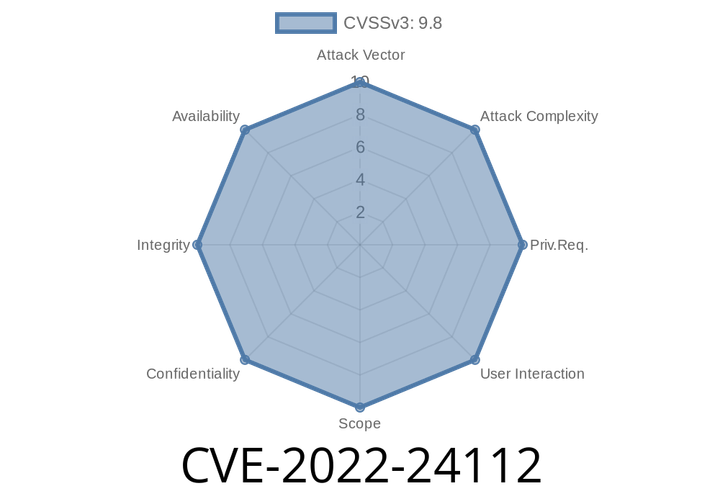
CVE-2022-24112 - How Attackers Bypass IP Restrictions in APISIX’s Batch-Requests Plugin (with Exploit Details)
Published: June, 2024
Author: Security Insights Lab
Apache APISIX is a widely used open-source API gateway. It helps organizations route, secure, and manage their
Episode
00:00:00
00:00:00