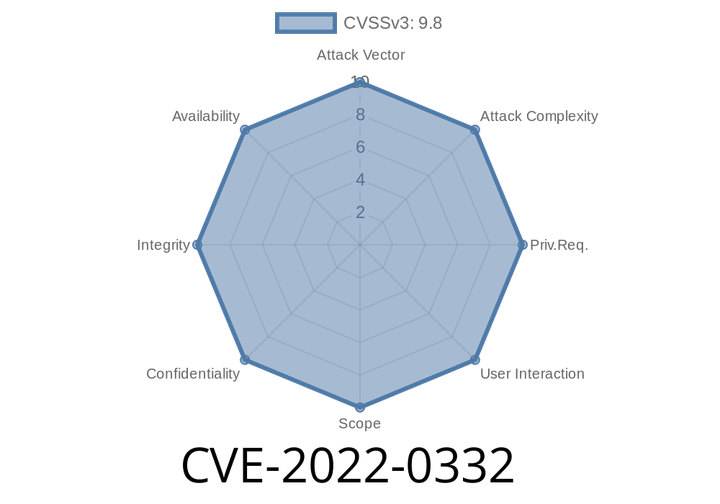
CVE-2022-0332 - SQL Injection Vulnerability in Moodle’s H5P Activity Web Service (Exclusive Exploit Analysis)
Moodle is one of the world’s most popular open-source learning management systems, used by universities, schools, and businesses around the globe. In early
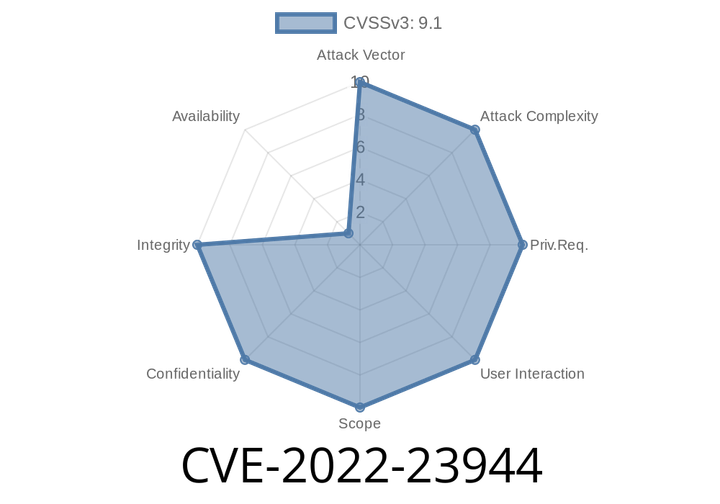
CVE-2022-23944 - Unauthenticated Access to /plugin API in Apache ShenYu 2.4. and 2.4.1 – Exploit Details & Explanation
CVE-2022-23944 is a critical security vulnerability found in Apache ShenYu, a popular API Gateway. This bug affects versions 2.4. and 2.4.
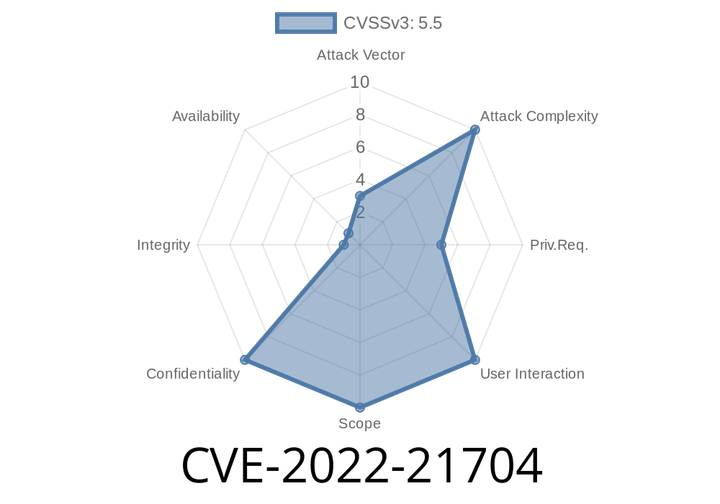
CVE-2022-21704 - How log4js-node Made Your Log Files World-Readable (and What to Do)
When you trust a logging library like log4js-node to keep track of what happens in your application, the last thing you want is that
CVE-2022-21679 - Istio Host-Based Authorization Policy Bypass Explained
Istio is a powerful open-source platform for connecting, managing, and securing microservices. It acts as a network "service mesh" that makes it
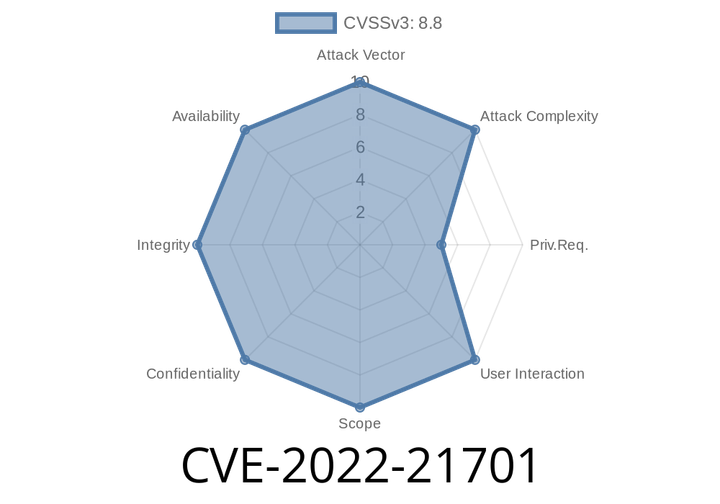
CVE-2022-21701 - Privilege Escalation in Istio via Kubernetes Gateway API
Istio is one of the most popular open-source service meshes used to connect, manage, and secure microservices in modern environments. However, in versions 1.
Episode
00:00:00
00:00:00