
CVE-2024-21207 - Crashing Oracle MySQL Server’s InnoDB Engine – A Deep Dive
*Published: June 2024*
*By: [Your Name]*
CVE-2024-21207 describes a significant denial-of-service (DoS) vulnerability in Oracle MySQL Server’s InnoDB storage engine.
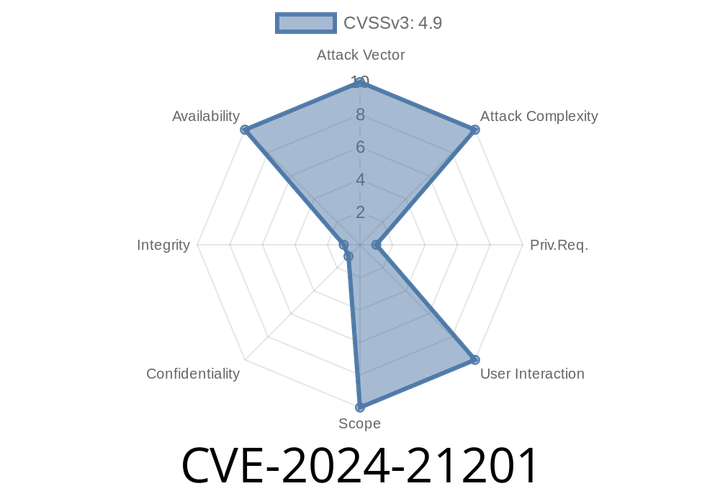
CVE-2024-21201 - MySQL Optimizer DoS Vulnerability (Crash & Hang Exploit Guide)
A serious vulnerability (CVE-2024-21201) has been discovered in Oracle MySQL Server, specifically in the Optimizer component. This flaw affects all supported versions up
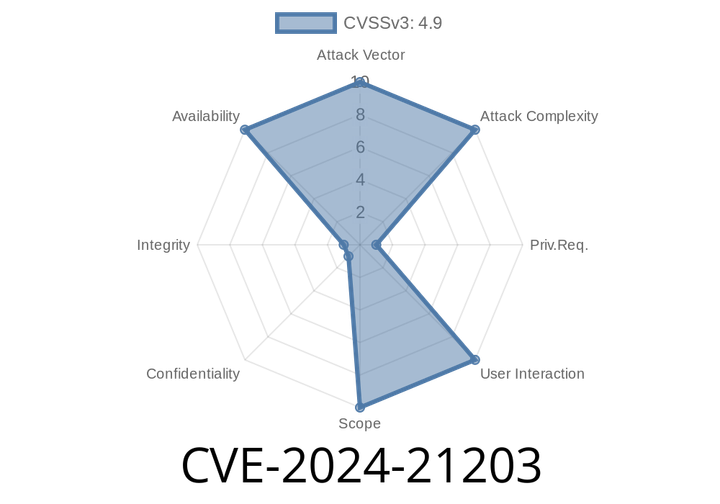
CVE-2024-21203 - Oracle MySQL FTS Vulnerability – Full Exploit Analysis & Crash Demo
In June 2024, Oracle published a security advisory about a new vulnerability: CVE-2024-21203. This security bug affects the Full Text Search (FTS) feature
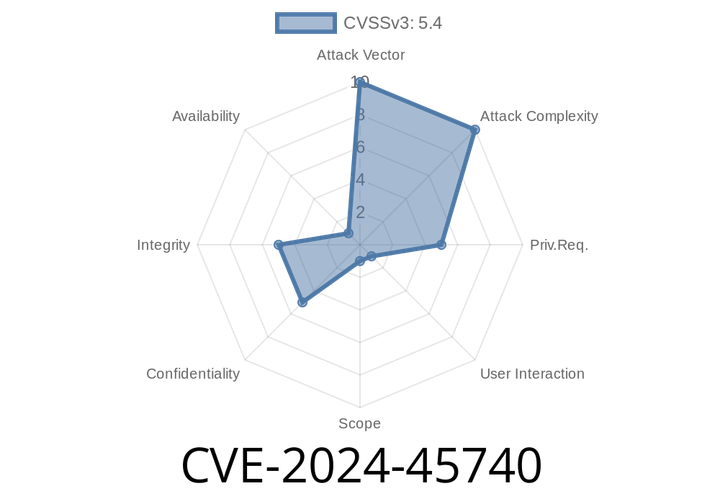
CVE-2024-45740 - Simple Guide to the Splunk Scheduled Views XSS Vulnerability (with Code, Examples, and References)
In May 2024, a critical security flaw—CVE-2024-45740—was discovered in Splunk Enterprise (versions below 9.2.3 and 9.1.6) and
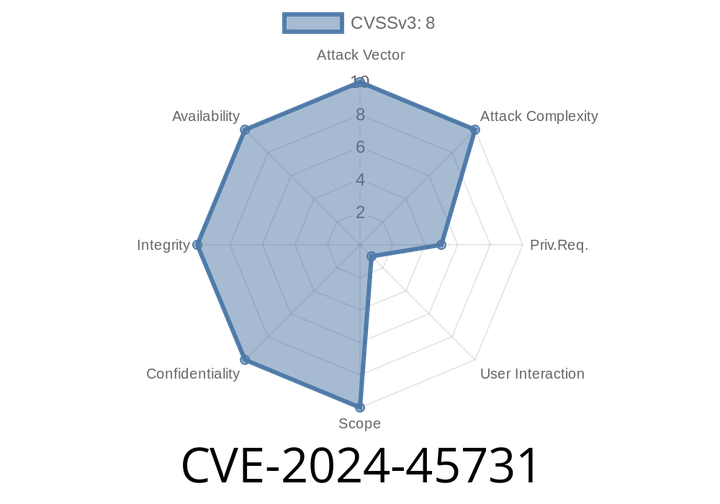
CVE-2024-45731 - Exploiting Path Traversal in Splunk Enterprise for Windows to Write Files in System32
In May 2024, a critical security vulnerability—CVE-2024-45731—was disclosed affecting Splunk Enterprise for Windows. This flaw allows any non-admin, non-power
Episode
00:00:00
00:00:00